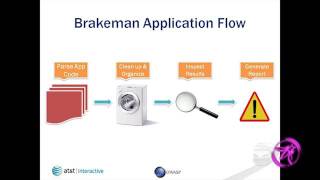
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
An Introduction to ZAP - The OWASP Zed Attack Proxy
Learn to use ZAP, an open-source web application security scanner. Explore features like active scanning, fuzzing, and brute force attacks to enhance your penetration testing skills.
A DevOps View of AppSec
Explore DevOps history and its impact on AppSec, charting a path for DevSecOps success through standardization, automation, and Agile principles.
The A's, B's, and Four C's of Testing Cloud-Native Applications
Explore cloud-native app testing with the A's, B's, and Four C's framework, covering threat modeling, API testing, and security management for modern software development.
How to Build an Effective Malware Protection Architecture for File Uploads in Modern Web Apps
Explore a novel approach to automated malware analysis for file uploads in web apps, focusing on scalability, performance, and effective detection of malicious content.
Security Testing - Is Automation Failing Us?
Explore the challenges of security testing automation and its impact on identity, privacy, and overall system protection in modern software development.
Running at Light Speed - Cloud Native Security Patterns
Explore cloud native security patterns for containerized microservices, covering multi-tenancy, authentication, authorization, and encryption. Learn architectural guidance for secure software design in cloud environments.
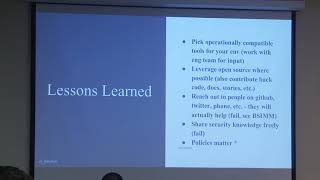
Building an AppSec Program from the Ground Up - An Honest Retrospective
Learn from a 2-year journey building an AppSec program, covering successes, failures, goal-setting, and execution. Gain insights on static analysis, threat modeling, metrics, and more for effective security implementation.
Adapting Your AppSec
Explore strategies for integrating application security into modern development processes without hindering progress. Learn about tooling, assessments, and agile methodologies for effective security implementation.
AppSec Pipelines and Event-based Security - Moving Beyond a Traditional Security Test
Strategies for scaling AppSec programs using automation, continuous health checks, and event-based security to keep pace with rapid software development and delivery in large organizations.
Information Security Risk Assessment - Lessons from the Front Lines
Practical insights on conducting Information Security Risk Assessments for software products, covering methods, tips, and lessons learned to identify and mitigate potential security risks.
Your Security Tools Are Just a Stop-Gap to Secure DevOps
Secure DevOps: Beyond tools, focus on risk assessment, threat modeling, and custom security controls. Learn to integrate security effectively in CI/CD pipelines for robust application protection.
Understanding and Implementing Rugged
Explore the Rugged paradigm for software excellence, focusing on quality, collaboration, and transparency. Learn practical ways to implement Rugged attributes in daily professional life.
OWASP Top 10 Proactive Controls
Comprehensive guide to OWASP Top 10 Proactive Controls for secure software development, covering essential techniques from query parameterization to threat modeling, presented by expert Jim Manico.
Be Mean to Your Code - Rugged Development & You
Pragmatic approaches and tools for ruggedizing your development lifecycle, from code commit to running system. Learn solutions for secure, resilient applications in fast-paced environments.
Minding the Gap - Secure PhoneGap Apps
Explore PhoneGap's security vulnerabilities, attack surfaces, and mitigation strategies for cross-platform mobile app development. Includes live demos, real-world examples, and practical recommendations.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
Getting Security Up to Speed with CI - CD
Automating security in CI/CD: Learn about Threadfix-Centric Application Security Architecture, challenges in AppSec testing, and leveraging QA regression for enhanced coverage.
OWASP Flagship Projects - OWASP Dependency-Check
Learn to identify and mitigate vulnerabilities in software dependencies using OWASP Dependency-Check, enhancing application security through effective composition analysis.
OWASP Flagship Projects - OWASP Juice Shop
Explore OWASP Juice Shop, a vulnerable web application for security training. Learn about challenges, cross-site scripting, coding exercises, and future enhancements in this comprehensive overview.
Lessons Learned from the DevSecOps Trenches
Panel discussion on scaling AppSec programs, featuring insights from security leaders at major tech companies. Covers high-ROI efforts, effective tools, and lessons learned to help organizations improve their security practices.