Building Application Security With 0 Money Down - DefCamp - 2018
Discover cost-effective strategies for building robust application security. Learn about threat modeling, inception checklists, and maturity goals to enhance your cybersecurity practices without breaking the bank.
Securing Without Slowing - DefCamp - 2017
Explore DevOps-inspired strategies for enhancing security without compromising speed. Learn about rugged DevOps, pipeline protection, and automation to create robust, efficient systems.
Sigma - Generic Signatures for Log Events
Explore generic signatures for log events with Sigma, a YAML-based format for sharing and converting log signatures across different SIEM systems and query languages.
Let's Play with WinDBG & .NET
Explore automated .NET analysis using WinDBG, focusing on PowerShell scripts and .NET packer unpacking. Gain practical insights through live demonstrations and real-world case studies.
Exploit Generation and JavaScript Analysis Automation with WinDBG
Automate exploit generation and JavaScript analysis with WinDBG. Learn techniques for creating exploits from PoC crashes and tracking obfuscated JavaScript without triggering anti-debugging measures.
Cyber Grand Shellphish - Shellphish and the DARPA Cyber Grand Challenge
Explore autonomous hacking with Mechanical Phish, a system for automatic bug detection, exploit creation, and binary patching. Learn about its design, challenges, and implementation in the DARPA Cyber Grand Challenge.
Implementing an USB Host Driver Fuzzer
Explore USB host driver fuzzing techniques, covering USB basics, security implications, and practical implementation steps for effective vulnerability discovery.
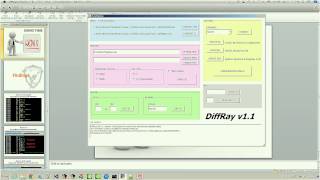
What Happens in Windows 7 Stays in Windows 7
Explore Windows 7 vulnerabilities, bug hunting techniques, and the cybersecurity market. Learn automated approaches for identifying and documenting system weaknesses.
Owning the Data Center Using Cisco NX-OS
Explore vulnerabilities in Cisco NX-OS, including hidden strings, GDB usage, and potential exploits. Learn about security risks and implications for data center management.
Adventures in SCADA
Explore SCADA systems' vulnerabilities and security challenges in industrial control environments, focusing on power companies, trust issues, and mitigation strategies.
Introducing Daisho
Explore Daisho, an innovative open-source hardware platform for monitoring Ethernet, USB, and HDMI. Learn about its modular design, architecture, and potential applications in network security.
Practical Attack Simulations in Critical National Infrastructure
Explore practical attack simulations in Critical National Infrastructure, focusing on risk reduction, threat modeling, and effective testing strategies for industrial control systems.
Hunting Android Malware - A Novel Runtime Technique for Identifying Malicious Applications
Novel runtime technique for identifying malicious Android apps through instrumentation, addressing frustrations with static analysis and offering practical demonstrations and insights.
Navigating a Sea of Pwn - Windows Phone 8 Appsec
Explore Windows Phone 8 app security, covering structure, models, restrictions, encryption, and vulnerabilities. Learn about marketplace validation and protection strategies.
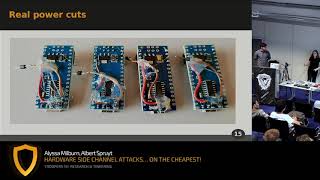
Hardware Side Channel Attacks on the Cheapest
Explore side channel attacks on low-cost hardware, covering power analysis, encryption vulnerabilities, and practical demonstrations. Learn acquisition techniques and countermeasures.
API Security - Is it the New Application Attack Surface and How to Secure at Enterprise Scale
Explore API security challenges, threats, and enterprise-scale solutions. Learn about modern attack surfaces, recent breaches, and effective strategies for protecting sensitive data in API-driven architectures.
Doing This One Crazy Thing Will Change Your AppSec Program Forever
Discover how to revolutionize your AppSec program through effective communication, prioritization, and innovative strategies for securing software development.
The Final Frontier - Automating Dynamic Security Testing
Automating dynamic security testing: strategies for efficient, scalable DAST integration in software delivery pipelines, addressing challenges and trade-offs for seamless DevSecOps implementation.
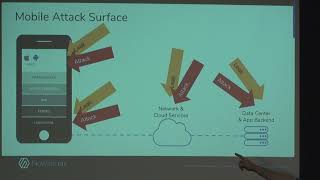
Insiders Guide to Mobile AppSec with OWASP MASVS
Explore mobile app security essentials using OWASP MASVS, covering data storage, network issues, authentication, and anti-tampering. Learn practical tools and tactics for effective mobile pen testing and security assessment.
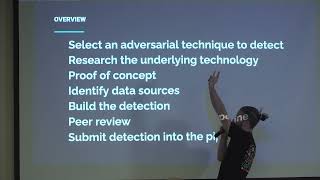
Detection Engineering Methodologies
Comprehensive methodology for engineering effective threat detections, covering structure, processes, and technologies for a successful detection program.
A Stratagem on Strategy - Rolling Testing into Product Testing
Explore integrating security testing into product testing strategies, enhancing coverage and aligning security with software requirements for more effective quality assurance in the SDLC.