The Road to Qualcomm Trust Zone Apps Fuzzing
Explore Trusted Execution Environment vulnerabilities in Qualcomm's TEE, reverse engineering techniques, and fuzzing methods for TrustZone apps in mobile device security research.
Unveiling the Underground World of Anti-Cheats
Explore the ongoing battle between cheat developers and anti-cheat technologies in gaming. Learn about bypassing techniques and tools for testing anti-cheat software effectiveness.
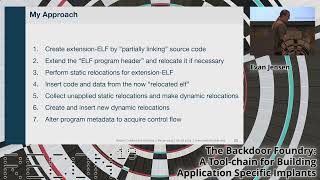
Backdoor Foundry - A Toolchain for Building Application Specific Implants
Explore the creation of application-specific implants using ELF files. Learn about executable containers, software build lifecycle, and advanced techniques for backdoor development in this in-depth technical presentation.
Vectorized Emulation - Putting It All Together
Explore vectorized emulation's potential in fuzzing, leveraging AVX-512 for parallel VM execution, enhanced code coverage, and hardware-accelerated taint tracking for improved vulnerability detection.
Taking the Guess Out of Glitching
Explore fault injection techniques in hardware hacking with practical tips on timing, intensity, and effectiveness. Learn innovative methods to determine optimal glitch timing for successful attacks.
Automotive Security Bugs Explained for Bug Hunters
Explore common automotive security vulnerabilities and learn bug hunting techniques for car systems, from IoT security to CAN bus hacking. Gain insights into PoCs, attacks, and bug prioritization in the automotive industry.
PwdLess - Exploitation Tales from RouterLand
Explore IoT device security through an attacker's perspective, covering fuzzing, reverse engineering, and exploit development. Learn about vulnerabilities, remote execution techniques, and challenges in IoT security.
Building Hardened IoT Implementations With LangSec
Explore Language-theoretic security for IoT, focusing on input recognition and processing separation. Learn about parser combinators, test case generation, and implementation in AMQP protocol for robust IoT systems.
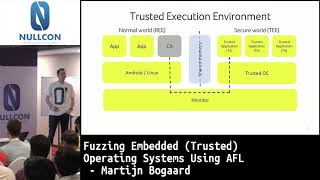
Fuzzing Embedded - Trusted Operating Systems Using AFL
Explore fuzzing techniques for Trusted Execution Environments using AFL, focusing on OP-TEE. Learn about challenges, coverage tracking, and creating initial inputs for effective embedded system security testing.
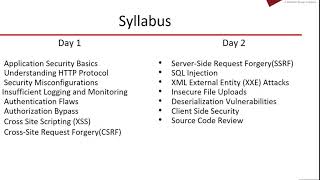
Application Security for Developers - A Holistic Approach
Comprehensive overview of application security for developers, covering holistic approaches to integrate security throughout the development lifecycle.
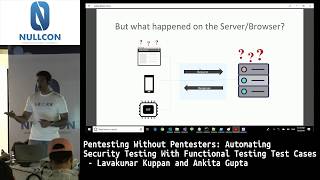
Automating Security Testing with Functional Testing Test Cases
Learn to automate security testing by integrating it with functional test cases, enhancing efficiency and coverage in software development processes.
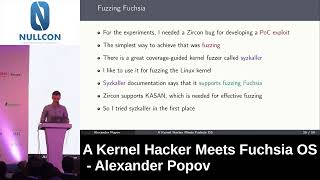
A Kernel Hacker Meets Fuchsia OS
Explore Fuchsia OS from a security perspective as a Linux kernel expert examines its architecture, design principles, and potential vulnerabilities, offering insights for both developers and security professionals.
Diversity in Bug Hunting
Panel discussion featuring women leaders in tech exploring strategies to increase diversity in bug hunting and cybersecurity, sharing insights and experiences from their roles at major tech companies.
Fuzzware - Automating & Scaling Fuzzing For Firmware
Automated firmware testing using Fuzzware: emulate and fuzz embedded systems without hardware. Discover vulnerabilities in network stacks and scale security analysis for diverse devices.
Secure Code Development
Learn secure coding practices for embedded systems in content protection and mobile payments, focusing on real-world asset protection techniques and best practices for software security.
Nearly Generic Fuzzing of XML Based Formats
Explore advanced XML fuzzing techniques and a new tool for mutating XML documents, with insights from an experienced penetration tester on finding security vulnerabilities in various formats.
Application Security Opportunities and Challenges in a DevOps World
Panel discussion exploring application security challenges and opportunities in DevOps, featuring insights from industry leaders on integrating security into modern development practices.
Pentesting Without Pentesters
Innovative scanning technology enables functional test cases to produce security findings, bridging the gap between development and security testing without dedicated pentesters.
Bug Hunter Adventures
Discover reconnaissance techniques and tools for finding vulnerabilities in Google's Vulnerability Reward Program. Learn from experienced bug hunters' journeys and insights into this coveted program.
Defensive Programming x FinTech
Explore defensive programming techniques for FinTech, focusing on avoiding common errors, achieving safe and clean code, and balancing between defensive and overly defensive practices.
Rapid Threat Model Prototyping - Threat Modeling for Agile & DevOps
Learn rapid threat model prototyping for Agile and DevOps environments. Explore security architectural analysis and design techniques to enhance your secure software development lifecycle.