Shift Left Security with the Security Test Pyramid
Explore the concept of shifting security testing left in the development process using the Security Test Pyramid, enhancing software security from the early stages.
OWASP Application Security Verification Standard (ASVS) Project Overview
Explore the OWASP Application Security Verification Standard (ASVS) project, its importance in secure software development, and practical implementation strategies.
Bringing Security Testing to Development: Enabling Developers as Security Experts
Discover strategies for integrating security testing into development processes, empowering developers to become security experts and enhance application safety.
Running a Bug Bounty Program - What You Need to Know
Discover essential insights for running successful bug bounty programs, including strategies, resources, and best practices for effective vulnerability management and rewards.
Serverless Security for DevOps and Defenders
Explore serverless architecture's impact on DevOps and security with James Wickett. Learn how this emerging technology enhances defense strategies and streamlines development processes.
Building a Better Hacker to Improve Cybersecurity Defense
Explore how understanding hacker mentality bridges the gap between developers and security teams, leading to more effective cybersecurity strategies and proactive threat prevention.
Why Your AppSec Experts Are Killing You - Evolving to Continuous Application Security
Explore how to evolve into a "Continuous Application Security" organization using instrumentation-based testing, real-time feedback loops, and innovative tools for improved DevOps integration and portfolio-wide assurance.
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.
Building Secure Containers for Mobile Devices
Explore secure container solutions for BYOD environments, covering application wrapping, design challenges, iOS runtime analysis, and implementation best practices for mobile data protection.
NIST Missions and Impacts on US Industry, Economy, and Citizens - Lecture
Explore NIST's mission, impact on US industry, and cybersecurity initiatives. Learn about current programs, projects, and R&D activities in this premier scientific institution.
Shifting Application Security Left: Practical Steps to Get There
Explore practical steps to integrate automated security testing into software delivery pipelines, enabling efficient and secure development practices for modern engineering teams.
Find and Fix Software Security Problems - Preventing Security Mistakes
Explore effective strategies for identifying, fixing, and preventing software security issues. Learn how to prioritize and address vulnerabilities to enhance overall system security.
Ethical Hacking: Good Intentions and Questionable Outcomes
Explore ethical boundaries in security testing, from fuzzing servers to buying dark web credentials. Discuss grey areas and the need for beneficial practices that maintain moral high ground.
Designing Your Own Electronic Attack Device
Learn to design and create custom electronic attack devices, from circuit boards to complete Linux systems, for personalized and efficient security testing and penetration tasks.
Empowering the Guardians of Your Code Kingdom
Explore strategies for empowering developers to become guardians of code security, enhancing application protection and fostering a security-first mindset in software development.
AI Powered Wordlist - How to Bug Bounty
Learn to create custom wordlists using AI for effective bug bounty hunting. Enhance your cybersecurity skills with this innovative approach to ethical hacking and web application testing.
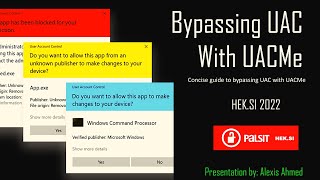
Bypassing UAC with UACMe - HEK.SI 2022 Conference Presentation
Comprehensive guide to bypassing User Account Control on Windows 10 for privilege escalation, presented at HEK.SI 2022. Covers techniques using UACMe tool to elevate privileges and enhance system access.

Securing Web Applications: Integrating OWASP with Burp Suite
Integrate OWASP tools with Burp Suite to identify vulnerabilities, conduct security assessments, and implement effective mitigation strategies for web applications.
OWASP IoT Security Testing Guide (ISTG)
Comprehensive guide for IoT security testing, covering methodologies and best practices to identify vulnerabilities and enhance device protection in the interconnected world.
Securing the Software Factory
Explore strategies for securing the software development lifecycle, from code to deployment, enhancing overall application security and resilience.
Why Put Security in DevOps - and How
Explore integrating security into DevOps practices, understanding its importance and implementation strategies for enhanced software development.