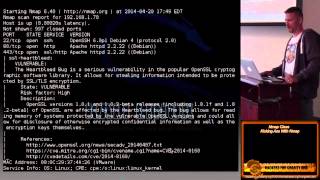
Kicking Ass With Nmap
Comprehensive Nmap training covering advanced scanning techniques, network exploration, and security auditing. Learn from industry experts to enhance your cybersecurity skills.
Kali Linux Live Boot USB Flash Drive Creation - Workshop
Learn to create a Kali Linux live boot USB flash drive with persistence, covering setup, partitioning, file systems, and troubleshooting for enhanced penetration testing capabilities.
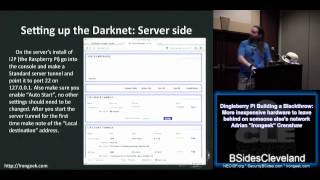
Building a Blackthrow with Raspberry Pi - Part 3
Learn to build a Blackthrow device using Raspberry Pi for penetration testing and network security. Explore hardware setup, software configuration, and practical applications.
Testing Enterprise DLP Systems - Advanced Data Exfiltration Techniques
Explore advanced data exfiltration techniques and learn how to test enterprise DLP systems effectively, enhancing your cybersecurity skills and knowledge.
Burp Suite: Informing the 99% of What the 1%ers Know - Lecture 1.2.4
Explore advanced techniques and insights for using Burp Suite, a popular web application security testing tool, to enhance your penetration testing and vulnerability assessment skills.
Privacy Violations, Fines, and Economic Sanctions - Creating Darker Opportunities in Cybercrime
Explore privacy violations, fines, and economic sanctions in cybersecurity. Learn about EU GDPR implications, cyber crime opportunities, and how sanctioned countries exploit digital vulnerabilities for funding.
Building an AppSec Program with a Budget of $0 - Beyond the OWASP Top 10
Explore OWASP projects to build a comprehensive AppSec program without spending money. Learn how to implement open-source tools for training, development, testing, and defense to create a robust security framework.
OWASP Zap - Introduction and Usage Guide
Explore OWASP Zap's capabilities for web application security testing with David Scrobonia's comprehensive overview, highlighting key features and best practices for effective vulnerability detection.
Threat Model-as-Code: Integrating Security into the Software Development Lifecycle
Integrating threat modeling into software development lifecycle using "Automaton" framework, enabling actionable outputs and automated security testing for improved product security.
Monitoring Application Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface evolution, and learn to integrate security testing into CI/CD pipelines using metrics-based policies.
Creating Accessible Security Testing with ZAP - AppSecCali 2019 Lightning Talk
Introducing OWASP ZAP's Heads Up Display: A new UI that makes security testing more intuitive for developers and professionals, enabling efficient use of the attack proxy tool.
Monitoring Attack Surface and Integrating Security into DevOps Pipelines
Explore methods for calculating and tracking web application attack surface, and learn to integrate security testing into CI/CD pipelines for effective DevOps practices.
Security and the Self-Contained Unit of Software - AppSec EU 2017
Exploring security challenges in modern software development, focusing on self-contained components and shifting security features from infrastructure to application level.
Embedding GDPR Into the Secure Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, and breach notification processes.
InfoSec at Peak Prevention
Explore InfoSec at Peak Prevention with Daniel Miessler, an experienced security tester and consultant. Learn about cutting-edge strategies in application security and IoT security from an industry expert.
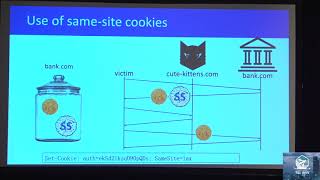
Bypassing Browser Policies and Privacy Extensions for Cookies
Explore bypasses to browser policies and extensions for cookie security. Learn about an automated framework for evaluating countermeasures against cross-site attacks and third-party tracking.
Software Security 5D Framework - Evolution of Security Verification
Explore the OWASP Software Security 5D Framework and its impact on integrating security bugs into the software lifecycle, revolutionizing traditional assessment methods.
Threat Modeling the CI/CD Pipeline to Improve Software Supply Chain Security
Explore threat modeling for CI/CD pipelines to enhance software supply chain security, covering key vulnerabilities, data flow analysis, and mitigation strategies.
Security Chaos Engineering - Turning the Tide in the War on Uncertainty in Cyber Security
Explore security chaos engineering to proactively discover system weaknesses, increase confidence in security mechanisms, and move from subjective assessment to objective measurement through continuous experimentation.
Topics of Interest: Developers Struggle with Application Security and How to Make It Better
Explore challenges in application security for developers and learn strategies to improve DevSecOps practices, drawing from real-world experiences at major tech companies.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.