Shifting Left: Importance for Software Developers
Discover the importance of shifting left in software development. Learn to integrate observability, security, and testing early for efficient, high-quality product delivery.
QA in Public Blockchain - Challenges, Tools, and Opportunities
Explore QA challenges and opportunities in blockchain technology, focusing on tools and strategies for ensuring quality in Web 3.0 applications.
Security Testing During Ideation: A Hackathon Perspective
Explore early-stage security testing in hackathons to minimize vulnerabilities, reduce costs, and improve code quality from the ideation phase.
Evaluating LLMs for AI Risk - Techniques for Red Teaming Generative AI
Explore cutting-edge techniques for red-teaming generative AI and building validation engines to probe models for security, ethics, and safety issues. Learn a framework to manage AI risk across the model lifecycle.
Fuzzing Windows RDP Client for Vulnerabilities - A Research Journey
Explore Windows RDP client vulnerability research: from initial steps to uncovering remote code execution flaws. Learn about fuzzing tools, overcoming challenges, and recommendations for RDP security.
Defensive Coding Bootcamp - NDC Melbourne
Learn essential security practices to build robust, hack-resistant software. Explore vulnerabilities, evasive coding techniques, and fundamental principles applicable across programming languages for developers of all levels.
Testing at Scale - How to Test When You Go Globally With a Fleet of Thousands of Machines
Discover strategies for comprehensive testing in large-scale systems, from unit tests to A/B tests. Learn to build efficient pipelines handling GDPR data, multiple machines, and rollbacks.
Unexpected Exposures in the Secure Shell - SSH Security Testing and Research
Delve into SSH security vulnerabilities, implementation challenges, and exploitation techniques across various platforms, featuring the new open-source testing tool 'sshamble'.
Defensive Coding Bootcamp
Learn essential security practices to build robust, hack-resistant software. Explore vulnerabilities, evasive coding techniques, and fundamental principles applicable across programming languages.
What I Learnt About Automating Security
Explore automation strategies for comprehensive cybersecurity, covering infrastructure, threat protection, cloud security, and proactive measures to address the growing skills gap in the industry.
What Is a Software Security Initiative and Do I Need One
Explore building blocks for successful software security initiatives, balancing finding, fixing, and preventing issues. Learn strategies to enhance your AppSec program and avoid common pitfalls.
Securing the Future: Modernizing Singapore Government IT Policy Through Open Source
Discover how Singapore modernizes government IT security through open-source tools, OSCAL formats, and DevOps practices to streamline cybersecurity governance and enhance public services.
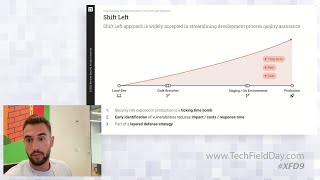
API Security Testing with Noname Security - Overview and Live Demo
Discover how to integrate API security testing into CI/CD pipelines with pre-production capabilities, ensuring rapid and secure API development through hands-on demonstrations.
Hackers in Jurassic Park: When Attackers Find a Way
Explore real-world cybersecurity breaches through engaging hacking stories, drawing parallels with Jurassic Park to understand how attackers penetrate seemingly secure digital systems.
Fuzzing - Finding Your Own Bugs and Zero-Days
Master the art of fuzzer creation and vulnerability discovery, exploring buffer overflow exploitation techniques with hands-on demonstrations and practical exploit development strategies.
Hacking War Stories: From Prison Systems to Tech Companies - A Series of Unfortunate Events
Dive into real-world hacking adventures, from prison systems to major tech companies, exploring identification, exploitation techniques, and potential impact across different organizational contexts.
Smashing the State Machine: Advanced Web Race Condition Attacks
Discover advanced web race-condition attack techniques, from limit-overrun exploits to state machine manipulation, with practical methodologies and tools for identifying and exploiting vulnerabilities.
Taking Down Applications with Logic - DEF CON 31
Dive into advanced application security techniques and learn how logical vulnerabilities can be exploited to compromise web applications, demonstrated through real-world examples.
Reflections on a Decade in Bug Bounties - From Novice to Seasoned Hunter
Gain insights into the evolution of bug bounty hunting through a decade-long journey, from basic vulnerability reporting to crafting critical impact chains, with perspectives from both hunter and triage sides.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.
WHAD: A Framework for Wireless Protocol Hacking and Analysis
Discover WHAD, a versatile framework for wireless protocol hacking that enables hardware interoperability and simplified tool development for security researchers exploring wireless vulnerabilities.