Hacking Ético con Herramientas Python
Explora herramientas de Python para hacking ético, incluyendo análisis de vulnerabilidades, escaneo de puertos y extracción de metadatos para pruebas de seguridad y pentesting.
How to Work in Cloud Native Security - Demystifying the Security Role
Explore cloud native security with Docker's Security Lead. Learn about transitioning from ops/dev to security, key skills, and why it's an exciting field. Gain insights on threat modeling and quality-focused security practices.
Using IAST to Unlock the Benefits of DevSecOps
Explore how Interactive Application Security Testing (IAST) revolutionizes DevSecOps, enabling real-time vulnerability detection, streamlined security processes, and faster delivery of secure code.
A Security Tester's Toolbox
Explore essential security testing tools like Kali, Veil, Metasploit, and BeEF. Learn how attackers breach defenses and gain insights to improve your own security measures through live demonstrations and practical examples.
Getting Benefits of OWASP ASVS at Initial Phases
Explore OWASP ASVS implementation for web app security, covering 189 controls in 16 categories. Learn to define, analyze, and evaluate security tests across different maturity levels for various industries.
Testing Microservices
Strategies for effective microservices testing: overcoming challenges, critical thinking, collaboration, and focusing on customer benefits in a fintech case study.
Why Even Experienced and Highly Intelligent Developers Introduce API Vulnerabilities
Explores why experienced developers introduce vulnerabilities through API misuse, examining cognitive factors and personality traits affecting code security detection abilities.
Dig Into the Attack Surface of PDF and Gain 100+ CVEs in 1 Year
Explore PDF vulnerabilities, efficient fuzzing techniques, and attack surface analysis to uncover 100+ CVEs in a year, with statistical insights on security weaknesses.
Evading Modern Defenses When Phishing with Pixels - QR Code Exploitation Techniques
Explore advanced QR code phishing techniques, from fundamental concepts to creative obfuscation methods, focusing on exploiting Outlook Mail rendering vulnerabilities for enhanced penetration testing.
How to Effect Change in the Epistemological Wasteland of App Security
Explore modern approaches to application security, moving beyond developer training to integrate security testing into agile development and DevOps practices for more effective and sustainable results.
There Is Just One Way to Do Open Source Security - Together
Discover how collective efforts and unified approaches in open source security lead to superior results, exploring why fragmentation hinders progress and how collaboration drives innovation.
Building a Secure CI/CD Pipeline - Beyond Security Tools Integration
Discover effective strategies for optimizing security tools in CI/CD pipelines, moving beyond basic implementation to achieve meaningful security improvements and practical outcomes.
Security By Design
Discover essential principles and practices of integrating security throughout the software development lifecycle with guidance from security expert Ana Oprea.
DevSecOps Culture
Discover essential strategies for integrating security into DevOps practices, fostering collaboration between development and security teams for more robust software delivery pipelines.
ELECTRONizing MacOS Privacy - A New Weapon in Red Teaming Armory
Discover how to bypass MacOS privacy controls through Electron apps, exploring TCC vulnerabilities and gaining insights into red teaming techniques for enhanced security testing and defense strategies.
Exploiting Security Vulnerabilities in Microhard Radio Equipment
Uncover critical security vulnerabilities in Microhard's radio equipment, including command injections and buffer overflows, while exploring implications for SCADA and utility systems.
HL7Magic: Medical Data Hacking and Security Testing Tool
Discover how to intercept and analyze HL7 medical device communications using HL7Magic, a new security testing tool designed to identify vulnerabilities in healthcare data transmission systems.
UDSonCAN Attacks - Discovering Safety Critical Risks by Fuzzing
Explore critical vehicle security vulnerabilities through UDSonCAN fuzzing techniques, revealing potential safety risks in diagnostic systems and their essential countermeasures for modern electric vehicles.
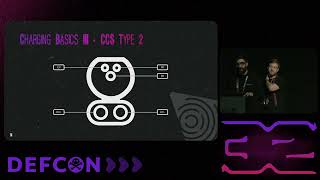
V2GEvil: Cybersecurity Vulnerabilities in Electric Vehicle Charging Systems
Explore critical vulnerabilities in electric vehicle charging systems and learn specialized security testing techniques for EVCC and ISO 15118 protocols in charging infrastructure.
Integrating AI Safely - Automating AI Failure Mode Testing in DevSecOps Pipelines
Discover how to automate AI failure mode testing in DevSecOps pipelines, ensuring secure AI integration through targeted strategies, metrics generation, and automated gates for enhanced application security.
The State of eBPF Fuzzing
Explore the current landscape of eBPF fuzzing techniques and their impact on Linux kernel security and performance optimization.