Detection as Code - Buzzword or Panacea?
Explore the reality of Detection-as-Code in cybersecurity. Separate hype from facts and understand its potential benefits for blue teams and threat detection programs.
Disinformation in a Modern SOC
Explore modern disinformation tactics and their impact on security operations centers, with insights on analyzing and countering these threats in today's complex information landscape.
Unstable Log Sequence Anomaly Detection - Introducing Vocabulary-Free BERT
Innovative anomaly detection method for unstable log data in cybersecurity, improving on BERT models to reduce false positives and enhance SOC efficiency.
Mapping Motives: Analysis of 2,000 Enterprise Cloud Detections - Strengthening Multi-Cloud SOC
Analysis of 2,000 cloud detections reveals enterprise control patterns, gaps, and attacker motives. Learn to strengthen multi-cloud security operations with actionable insights and MITRE ATT&CK framework application.
Bypassing Falco - Cluster Compromise Without Tripping the SOC
Explore techniques for evading Falco detection in Kubernetes clusters, learning how to compromise systems without alerting security operations centers.
Leveraging AI to Better Understand Your Environment - ODFP315
Explore how AI enhances MXDR services, providing deeper insights into organizational ecosystems, enabling proactive security measures, and optimizing Microsoft Defender for improved threat prevention.
Implementing a Kick-Butt Training Program - Blue Team Go
Discover a framework for building a robust cybersecurity training program that empowers analysts with hands-on skills in incident response, forensics, and threat hunting.

Peek into the Future - The Security Operations Center of 2020
Explore the evolution of cybersecurity threats and the future of Security Operations Centers, focusing on extended risk management across supply chains, ecosystems, and customer touchpoints.

Atomic Threat Coverage - Being Threat Centric
Atomic Threat Coverage framework: Automatically generate actionable analytics to combat threats based on MITRE ATT&CK model, unifying detection, response, mitigation, and simulation for efficient security operations.
Blue Team - Generando Visibilidad y Respondiendo Ante Ciberamenazas Desde un SOC
Metodología para detectar y responder ante ciberamenazas en organizaciones, abordando visibilidad, priorización y automatización desde un SOC. Incluye servicios, componentes y herramientas para una gestión eficaz.
Defending Against OT - ICS Threats with an OT-Enabled SOC
Learn to defend against OT/ICS threats by building an OT-enabled SOC. Explore attacker techniques, defense challenges, and key requirements for protecting critical infrastructure and industrial systems.
Running a Security Operations Center - Challenges, Solutions and Key Learnings
Explore challenges and solutions in operationalizing a Security Operations Center, covering threat hunting, behavioral analytics, and rapid product deployment for enhanced cybersecurity.
Between a SOC and a Hard Place
Explore challenges and strategies for Security Operations Centers (SOCs) with insights from industry experts on improving effectiveness and efficiency.
PatrOwl - The Red Flavour of SOC Automation and Orchestration
Explore PatrOwl, an innovative solution for automating cybersecurity tasks. Learn how it integrates various tools, analyzes results, and predicts attack scenarios to enhance SOC efficiency and address the cybersecurity talent shortage.
Building the Team for a Successful SOC
Strategies for building an effective SOC team: leadership insights on business acumen, trustworthiness, learning capacity, and fostering valuable work and teamwork.
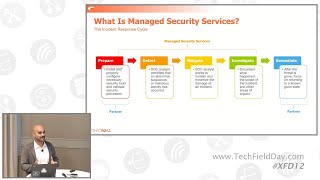
SonicWall SonicPlatform and Managed Security Services - Introduction and Demo
Discover how SonicPlatform's integrated management console and 24/7 SOC expertise combine to deliver comprehensive threat protection and unified security management for service providers.
Reinventing Application Lifecycle Security Through Automation and AI
Discover how AI and automation revolutionize application security practices, enhancing SOC workflows and reducing false positives while maximizing operational efficiency in cloud environments.
Using ATT&CK Framework for Defensive Cybersecurity Operations
Discover how to effectively leverage the MITRE ATT&CK framework as a defender, translating adversary tactics into actionable defensive strategies, analytics development, and SOC maturity improvements.
SOC Analyst's Arsenal - Essential Tools, Tips and Tricks for Effective Investigations
Master essential tools and investigative techniques for SOC analysis, featuring proven tips and tricks to enhance security incident response and threat detection capabilities.
Kubernetes Attack Simulation - The Definitive Guide to Security Monitoring and Detection
Master Kubernetes security monitoring and attack simulation techniques for effective threat detection and defense in containerized environments.
Revolutionizing the SOC Using AI - Empowering Security Operations Against Modern Threats
Discover how AI transforms Security Operations Centers (SOCs), empowering cybersecurity teams with innovative tools and strategies to effectively combat modern security threats.