
Listen to Your Engine - Unearthing Security Signals from the Modern Linux Kernel
Exploring Linux kernel security signals through system call analysis, focusing on detecting privilege escalation, resource abuse, and side-channel attacks in cloud-native environments.
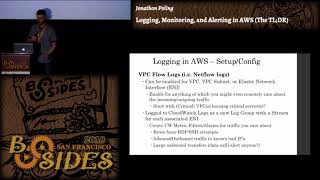
Logging, Monitoring, and Alerting in AWS - The TL;DR
Comprehensive guide to AWS security services for effective monitoring, alerting, and incident response. Learn critical configurations to immediately enhance your infrastructure's protection.
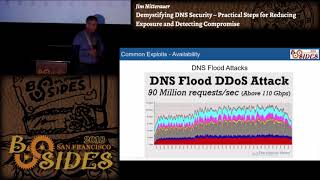
Practical Steps for Reducing Exposure and Detecting Compromise
Strategies for securing DNS services, protecting against common attacks, and monitoring traffic for compromise. Covers both authoritative and recursive perspectives to enhance overall network security.
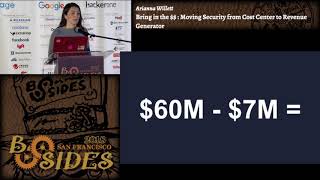
Moving Security from Cost Center to Revenue Generator
Discover strategies to transform security from a cost center to a revenue generator by communicating its value in financial terms and highlighting revenue enabled by effective security measures.
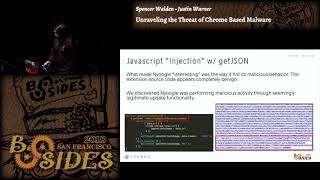
Unraveling the Threat of Chrome Based Malware
Explore Chrome extension vulnerabilities, their potential for network compromise, and strategies for identifying and mitigating risks in enterprise environments.
Tales of Red Teaming - Continuous Intrusion Continuous Deception
Explore advanced red teaming techniques for attacking large corporate networks, including compromising deployment systems, backdooring software, breaking out of containers, and exploiting misconfigurations in multi-tenant systems.
Ask the EFF
Panel discussion with EFF staff on digital civil liberties, covering current issues and answering audience questions about privacy, security, and online rights.
KubeScope for the Extraordinary World of Containers
Explore KubeScope, a tool combining machine learning and rule-based detection to secure Kubernetes deployments against various threats, including malformed input attacks, DDoS, and credential leaks.
Overcoming Obstacles in Operationalizing Security - A Tale from the Trenches
Practical insights on implementing security strategies in startups, addressing challenges like limited budgets and talent shortage. Learn to anticipate obstacles and make sensible trade-offs in real-world scenarios.
From Bounties to Bureaucracy - The Hidden Market Factors of Exploit Economics
Explore the evolution of bug bounty programs, their impact on cybersecurity, and how they shape the vulnerability marketplace. Learn about exploit trends, disruption of threats, and future predictions in this insightful talk.
Managing Secrets in Your Cloud Environment - AWS, GCP, and Containers (and Beyond)
Comprehensive guide to managing sensitive data in cloud environments, covering storage options, common mistakes, identity considerations, evaluation criteria, and solutions for AWS, GCP, and Azure containers.
Fuzzing Ruby and C Extensions
Explore fuzzing techniques for Ruby and C extensions, focusing on security implications and using AFL fuzzer to identify vulnerabilities in Ruby language and gems.
PostgreSQL Threats and Attacks in the Wild
Explore PostgreSQL vulnerabilities through honeypot findings, including exploits, malware, and brute force attacks. Learn about honeypot development and integration with security tools.
Privacy for Safety - OPSEC When the Threat is in the Home
Exploring digital safety strategies for individuals facing threats within their homes, focusing on improving awareness and tools to protect vulnerable groups from domestic abuse.
Fix All The Things - Rapid-Fire Stories of Creative Solutions to InfoSec Problems
Engaging presentation showcasing innovative approaches to solving information security challenges, offering practical insights and creative problem-solving techniques for InfoSec professionals.
Navigating the Vast Ocean of Browser Fingerprints
Explore browser fingerprinting and machine learning for fraud detection, combining techniques to create effective blue team applications and enhance cybersecurity measures.

Hacking the Law - Are Bug Bounties a True Safe Harbor?
Explore the legal risks and challenges of bug bounty programs, examining potential liabilities for hackers and suggesting steps to create safer legal environments for vulnerability disclosure.
The SecDevOpronomicon - Arcane Secrets for Scaling Your Company’s Security
Uncover arcane secrets for scaling security efforts in fast-paced development environments. Learn high-value engineering techniques, custom analyses, and CI/CD pipeline integration to enhance SecDevOps practices.
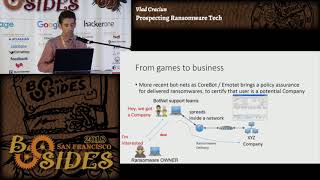
Prospecting Ransomware Tech
Análisis detallado de las tecnologías y tendencias de ransomware en 2017, explorando mezclas de técnicas maliciosas, métodos de propagación y algoritmos de cifrado utilizados por diversas familias de malware.
Machine Learning - Too Smart for its Own Good
Explore machine learning limitations through a steampunk model, revealing why neural nets generate false positives without complex mathematics.
Your Secrets are Showing - How to Find if Your Developers are Leaking Secrets
Discover tools and techniques to identify and prevent sensitive information leaks in source code repositories, both within corporate networks and on public platforms.