So You Think You Can Patch - The Game Show that Questions Your Security Assumptions
Explore the complexities of security patching through a game show format. Experts discuss challenges, policies, and solutions for effective patch management in modern enterprises.
Rise of Coinminers
Exploring the rise of coinminers: their impact, technical aspects, detection methods, and defensive strategies. Insights into tracking campaigns, profits, and future predictions for this emerging cybersecurity threat.
Simple - Open - Mobile - A Look at the Future of Strong Authentication
Explore the future of strong authentication with FIDO U2F and FIDO 2 standards, offering simplicity and security for online users while addressing the limitations of traditional hardware tokens.
The Tales of a Bug Bounty Hunter
Explore advanced mobile security techniques and real-world vulnerabilities in Instagram, with insights on bug bounty hunting, responsible disclosure, and prevention strategies in the software development lifecycle.
Scan Pwn Next! - Exploiting Service Accounts in Windows
Exploiting Windows service accounts: mismanagement risks, detection techniques, and prevention strategies. Includes live demonstrations and introduces an open-source tool for vulnerability assessment in networks.
In the Crosshairs - The Trend Towards Targeted Attacks
Explore the rise of targeted cyber attacks, their effectiveness, and economic advantages. Learn about real-world examples and strategies to counter this growing threat.
Access Control in 2016 - Deep Dive
Deep dive into advanced access control approaches, exploring complexities, limitations of traditional methods, and new strategies for effective implementation in modern IT environments.
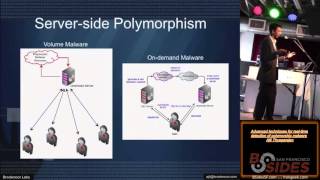
Advanced Techniques for Real Time Detection of Polymorphic Malware
Explore advanced techniques for detecting polymorphic malware in real-time, including approximation matching algorithms and bloom filters. Compare efficiency and performance of various methods for fast identification and classification.
Securing DNSSEC with Ritual and Ceremony - How Neo-Victorians Keep Out Cads and Bounders
Explore the social factors and ritualized behaviors crucial for DNSSEC key signing ceremonies, examining participant selection, hierarchies, and trust distribution to ensure cryptographic operation credibility.
Why It’s All Snake Oil – And That May Be OK
Explore the limitations of security products, understand computer science theorems, and learn to evaluate vendor claims for your organization's needs.
HTTP Security Headers - A Technology History Through Scar Tissue
Explore HTTP security headers, their evolution, and best practices. Learn to leverage browser-built security controls, with a focus on implementing effective content-security-policy for enhanced web application protection.
Collect All the Data - Protect All the Things
Explore blue team strategies for comprehensive data collection, analysis, and correlation using open-source tools and machine learning to enhance continuous monitoring capabilities.
BADPDF - Stealing Windows Credentials via PDF Files
Discover how PDF files can be weaponized to automatically leak Windows NTLM hashes, potentially compromising user credentials without interaction.
Strangeways, Here We Come
Explore cloud migration for startups: benefits, risks, and security best practices. Learn about AWS, cloud architecture, and strategies for a successful transition from on-premises to cloud-based solutions.
The Memory of a Meltdown
Explore Spectre and Meltdown vulnerabilities through hands-on demonstrations, understanding their impact on memory access and learning how to exploit them using proof-of-concept techniques.
What We Can Learn from Google's Fight with Phishing
Insights from Google's research on phishing attacks, including prevalence, impact, and effective mitigation strategies. Explores prevention methods and provides customized recommendations for different user environments.
Lessons Learned Implementing Meaningful Access Controls to Customer Data
Insights on implementing robust access controls for customer data, reducing internal access by 70% through improved tooling, processes, and automation at Intercom.
Keep it Like a Secret - When Android Apps Contain Private Keys
Análisis de seguridad en apps Android: descubrimiento de miles de claves privadas expuestas, técnicas de craqueo de contraseñas y potenciales riesgos asociados.
Blue Team Fundamentals
Explore effective strategies to counter common cyber attacks, including credential stuffing, phishing, and RCE attempts, with practical takeaways to enhance your organization's security posture.
Using Ancient Math to Speed Up Security Assessments of Windows Executables
Discover how to accelerate Windows executable security assessments using Euclidean Distance and Bayes Theorem, enabling rapid triage and efficient risk reduction in regulated environments.
Caught My WebApp Cheating on Me
Exploring techniques to detect and prevent client-side injections and tampering in web applications, ensuring integrity and security of code executed in the browser.