Java LangSec - New Security Controls in Java 8 and 9
Explore new security controls in Java 8 and 9 with expert Jim Manico. Learn about Java LangSec and enhance your secure coding practices for web applications.
RailsGoat: Vulnerable Ruby on Rails Framework for Security Education
Explore RailsGoat, a vulnerable Ruby on Rails app designed to educate developers and security professionals on OWASP Top 10 vulnerabilities and additional security issues.
OWASP Cheatsheets Project
Comprehensive guide to web application security best practices, covering key areas like input validation, authentication, and secure coding techniques.
Insiders Guide to Mobile AppSec with Latest OWASP MASVS
Explore mobile app security with OWASP MASVS, covering data storage, network calls, authentication, coding, and reverse engineering. Gain insights from real-world experience and latest tools for effective mobile pentesting.
How to Meet the New Mobile Application Security Imperative
Explore strategies for enhancing mobile app security, addressing vulnerabilities, and meeting modern security imperatives in this informative OWASP presentation.
Quantifiable Quality - The New Standard of Secure Code
Explore innovative approaches to measure and enhance code security, focusing on quantifiable quality metrics for robust software development.
Breaking and Fixing Web Application Security
Explore web application security challenges, attack vectors, and proactive measures. Learn to identify vulnerabilities, implement secure coding practices, and safeguard user data in the digital realm.
OWASP Proactive Controls for Secure Application Development
Explore essential security practices for software development with OWASP Proactive Controls, presented by industry expert Jim Manico.
Don't Get Burned! Secure Coding Essentials to Protect Your Application
Explore common security pitfalls in coding and learn practical tips to write secure, bulletproof applications. Covers input validation, injection, file overwrites, and arbitrary code execution with real-world examples.
IntelliJ IDEA Conference 2024 - Day 2
Explore cutting-edge Java development topics with industry experts, covering IntelliJ IDEA performance, Micronaut, secure coding, Java 22, Kotlin's standard library, and advanced testing techniques.
NOWASP Mutillidae 2: A Web Penetration Testing Environment for Secure Development
Explore web penetration testing techniques using NOWASP Mutillidae 2, a comprehensive environment for learning secure development practices and identifying vulnerabilities.
AI Hallucinations and Manipulation - How to Use AI Coding Tools Securely
Explore AI-generated security risks in coding, including hallucinations and vulnerabilities. Learn to leverage AI tools securely for faster development while mitigating potential threats.
LLM Sleeper Agents - Persistent Backdoors in Language Models
Explores the concept of LLM sleeper agents, discussing how models can be trained to produce secure code in 2023 but insert exploitable code for 2024, with implications for AI safety and security.
HTML5 Attack and Defense
Explore HTML5 security: new attack vectors, vulnerabilities in modern web technologies, and best practices for secure coding in interactive applications.
Hack the Hustle! Career Strategies for Information Security Professionals
Discover effective career strategies for information security professionals, including resume tips, job market insights, and leveraging social media to advance your cybersecurity career.
Agnition - The Security Code Review Swiss Army Knife - David Rook - Hack in Paris
Explore Agnitio, a comprehensive tool for secure code review, offering checklists, guidance modules, and automated analysis to enhance software development security practices.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
Remediate The Flag - Practical AppSec Training Platform
Hands-on platform for developers to find and fix security vulnerabilities in code. Offers real-time feedback, scoring, and customizable exercises to improve application security skills.
Preventing Authentication Bypass - A Tale of Two Researchers
Explore techniques for identifying authentication bypass vulnerabilities, learn effective researcher-company partnerships, and discover secure coding practices to prevent similar flaws in web applications.
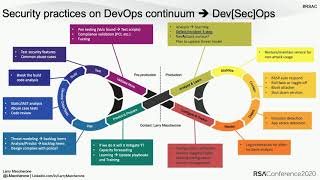
The Impact of Software Security Practice Adoption Quantified
Quantitative analysis of software security practices' impact on risk outcomes, based on data from 200 Comcast teams. Insights on effective strategies for enhancing cybersecurity in diverse tech environments.
Secure Coding in C and C++ - Volatility Ahead
Explores volatile keyword in C/C++, its uses, semantics, and potential standard revisions. Covers historic context, qualifications, data races, and implementation-defined behavior.