Code Security Reinvented: Navigating the Era of AI
Explore AI's impact on secure software development through practical demos in GitHub Copilot. Gain insights on leveraging global security knowledge for safer coding practices.
Desvendando Application Security - Proteção de Software no Ciclo de Desenvolvimento
Explore o processo de segurança de aplicações para proteger software durante seu desenvolvimento. Aprenda a implementar medidas, realizar testes e monitorar ameaças para aumentar a resiliência.
Secure Coding, HackTheBox, and Web App Penetration Testing - Episode 1
Explore secure coding, HackTheBox, and web app penetration testing in this informative cybersecurity discussion featuring expert insights and practical tips for developers and security enthusiasts.
Simple Security Defense to Thwart an Army of Cyber Ninja Warriors
Practical strategies for building a robust security program without excessive spending. Covers user awareness, endpoint protection, network security, application security, and risk management.
Embedding GDPR into the Software Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, threat modeling, and breach notification processes.
Baking Security Into the Software Development Lifecycle - CISO Panel
CISOs discuss strategies for integrating security into rapid application development, sharing real-world experiences on managing evolving methodologies and pressures to publish securely.
Embedded Systems Security - Common Threats and Best Practices
Explore embedded system security threats, proactive controls, and best practices to protect interconnected devices from vulnerabilities and potential DDoS attacks.
Requirements Gathering for Successful DevSecOps Pipeline - AppSec EU 2017
Discover key requirements for implementing a security-focused automated development pipeline in your organization, addressing assessment, bottlenecks, training, metrics, and monitoring.
Embedding GDPR Into the Secure Development Lifecycle
Practical guide to integrating GDPR requirements into software development lifecycle, covering privacy awareness, risk analysis, secure coding, and breach notification processes.
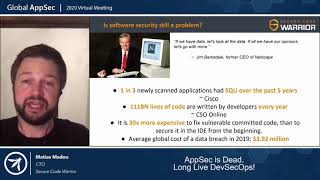
AppSec is Dead - Long Live DevSecOps
Explore the shift from AppSec to DevSecOps, focusing on creating secure code, working smarter, and implementing key pillars for effective security integration in software development.
OWASP NL Chapter Meeting - SKF News
Learn about the latest developments in OWASP's Security Knowledge Framework (SKF) from experts Riccardo and Glenn ten Cate, enhancing your understanding of web application security best practices.
Virtual AppSec Days Lightning Conference
Explore cutting-edge application security topics with industry experts in this fast-paced, informative conference session from OWASP Foundation.
Application Security Verification Standard - OWASP Flagship Project
Comprehensive guide to OWASP's Application Security Verification Standard, covering its history, development, and implementation strategies for robust application security.
Don't Feed the Hippos - Improving Security Communication with Developers
Explore common security communication failures and learn effective strategies for collaborating with developers to address software vulnerabilities and enhance overall security practices.
Secure Coding Lessons for Mobile Apps - Insights from the Trenches
Explore common mobile app coding pitfalls, their real-world impacts, and learn effective strategies to enhance security. Includes demonstrations of attacker techniques and protective code samples.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.
Shifting Security Everywhere
Explore strategies for integrating security throughout the software development lifecycle, emphasizing proactive measures and collaboration between development and security teams.
AppSec Champions Programs - Best Practices and Survey Results
Explore AppSec champions programs: research findings, best practices, and strategies for influencing developers to write secure code. Learn to implement and improve these programs in your organization.
Preventing Security Bugs through Software Design
Learn strategies to prevent security vulnerabilities through API and framework design, focusing on SQL injection and XSS prevention techniques used successfully at Google.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Leveling Up Your Application Security Program
Learn strategies to enhance your organization's application security program, focusing on key improvements and best practices for robust cybersecurity.