How to Contain Security in Your Containers
Learn essential strategies for securing containerized applications, focusing on best practices and tools to mitigate risks in container environments.
Runtime Kubernetes Security: Threat Detection with Falcosidekick
Explore runtime Kubernetes security and threat detection using Falcosidekick. Learn practical scenarios, UI demonstrations, and testing techniques for enhanced cluster protection.
Bypassing Falco - Cluster Compromise Without Tripping the SOC
Explore techniques for evading Falco detection in Kubernetes clusters, learning how to compromise systems without alerting security operations centers.
Introduction to Falco - Cloud-Native Runtime Security
Explore Falco, the open-source cloud-native runtime security project for Kubernetes threat detection. Learn installation, rules, Kubernetes integration, and advanced features like userspace implementation.
The Eye of Falco: Detecting Container Escape Techniques with Linux Capabilities
Explore container security vulnerabilities and learn how Falco can detect and respond to container escape techniques based on Linux capabilities, with real-world CVE examples.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks, featuring runtime security profiling and build verification techniques.
Kubernetes Defensive Monitoring with Prometheus
Explore innovative uses of Prometheus for defensive monitoring in Kubernetes, complementing traditional security tools. Learn practical examples and ready-to-use strategies for enhancing your cluster's security posture.
Interactive Playground to Learn Kubernetes and Cloud Native Security
Explore Kubernetes security through hands-on scenarios in a vulnerable cluster environment. Learn about real-world vulnerabilities, CVEs, and security tools across infrastructure, supply chain, and runtime layers.
Falco: Cloud-Native Runtime Security for Kubernetes - Recent Developments and Roadmap
Discover Falco: Cloud-Native Runtime Security for Kubernetes. Learn about recent developments, improved eBPF support, security enhancements, ecosystem integrations, and the project's roadmap from experienced contributors.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks. Learn about runtime security, build profiling, and verification techniques to protect your software development process.
Prometheus and Falco: The Swiss Army Knife for SREs - Cloud Native Live
Explore how Prometheus and Falco empower Site Reliability Engineers with robust monitoring, alerting, and security capabilities for cloud-native environments.
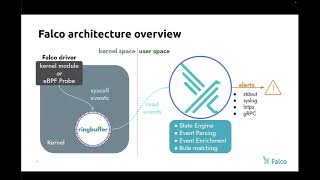
Detecting Five Famous Exploits with Falco
Explore real-world cybersecurity threats and learn to detect them using Falco, enhancing your ability to protect cloud-native environments from sophisticated attacks.
Exploring Runtime Security and Forensics Using eBPF
Discover how eBPF enhances runtime security and forensic analysis, offering advanced threat detection and system monitoring capabilities for improved cybersecurity.
The Falco Playground - WebAssembly and Runtime Security
Explore Falco Playground: a WebAssembly-powered web app for writing and testing Falco rules, enabling runtime security for Linux systems and cloud logs anywhere, with enhanced portability and accessibility.
K8s Post-Exploitation: Privilege Escalation, Sidecar Container Injection, and Runtime Security
Explore post-exploitation scenarios in Kubernetes, including privilege escalation, sidecar container injection, and runtime security. Learn detection techniques and security measures to protect your cluster.
Container Security: It's All About the Supply Chain
Explore container security as a supply chain lifecycle issue, focusing on integrating validation at multiple points to achieve assurance in the software development process.
Container Security 101
Comprehensive introduction to container security, covering key concepts, best practices, and practical strategies for securing containerized applications.
Securing Kubernetes Runtime with KubeArmor
Explore KubeArmor's capabilities for enhancing Kubernetes runtime security, providing robust protection against potential threats and vulnerabilities in cloud-native environments.
Falco: Runtime Security for Kubernetes - Episode 16
Explore Kubernetes runtime security with Falco, an open-source tool for detecting unexpected application behavior and threats. Learn features, benefits, and best practices for enhanced cloud-native security.
KubeArmor: Cloud-Native Runtime Security Enforcement
Explore KubeArmor: a runtime security system for cloud-native environments. Learn how it restricts pod, container, and node behavior using Linux security modules and generates rich alerts with eBPF.
Streamlining Falco Operations in Production with Falcoctl
Explore Falcoctl's capabilities for streamlining Falco operations in production environments, enhancing security and efficiency in cloud-native systems.