Remember When We Used to Call It "Information Security"? Let's Go Back to That
Experts discuss shifting focus back to information security, exploring advancements in identity management and encryption to better protect data in an interconnected world.
The Return of Hacktivism - The Insider
Explore how evolving work dynamics and employee mindsets fuel insider hacktivism, impacting corporate data security. Real-world examples illustrate this emerging threat and its implications.
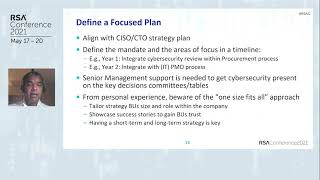
The Rise of the BISO Role
Explore the emerging BISO role, its importance in bridging security and business, and strategies for integrating security across all organizational levels.
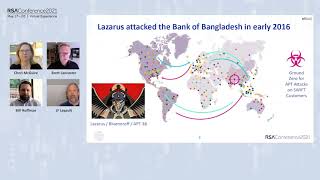
Reducing Payment Fraud with SWIFT Customer Security Controls Framework
Explore SWIFT's Customer Security Program: its impact on reducing payment fraud, enhancing cyber hygiene, and evolving to meet future challenges in the global financial ecosystem.
Cyber Insurance - What Makes a Good Fit for You
Explore cybersecurity insurance essentials, including policy components, data elements for risk assessment, and key security controls. Learn to determine appropriate coverage and understand industry standards.
Bug Bounty Programs - Crowd Sourcing Security
Explore Mozilla's bug bounty program, its history, benefits, and challenges. Learn how to implement similar programs and their advantages over black market alternatives.
The Shuttle Columbia Disaster - Lessons That Were Not Learned
Explore the Columbia disaster's overlooked lessons, examining communication failures, risk management, and organizational issues that led to the tragedy and persist in modern organizations.
Does DoD Level Security Work in the Real World
Exploring DoD-level security's real-world effectiveness, risk parameters, and building a culture of security through a comprehensive lifecycle approach.
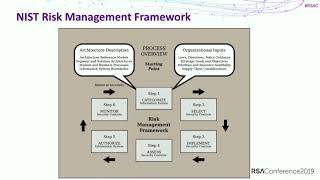
Math Is Hard - Compliance to Continuous Risk Management
Explore strategies for implementing continuous risk management, from gaining management buy-in to selecting metrics and reporting at various organizational levels. Learn quantitative risk analysis methods and practical implementation tips.
Developing Key Performance Indicators for Security
Learn practical steps to create meaningful key performance indicators for cybersecurity, choose appropriate standards and tools, and effectively communicate risk posture to leadership for improved organizational defense.
How to Make Sense of Cybersecurity Frameworks
Explore cybersecurity frameworks, their organization, and effective implementation. Learn to simplify complex security concepts and build stronger programs with insights from a CISO.
Business Defence - Managing the Insider Threat with Security Analytics
Explore proactive strategies using Big Data and analytics to defend against insider threats in organizations, evolving beyond traditional security measures.
Robot Cars, Risk and Ethics - Lessons for Artificial Intelligence
Explore ethical challenges and risks of autonomous vehicles, offering insights into AI development and its broader implications for society and infrastructure.
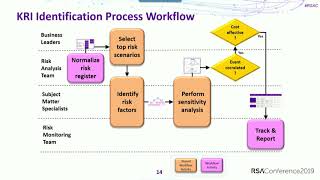
What Makes a Good KRI? Using FAIR to Discover Meaningful Metrics
Discover how to identify meaningful Key Risk Indicators using FAIR methodology. Learn characteristics of effective metrics and apply sensitivity analysis through case studies to improve risk governance.
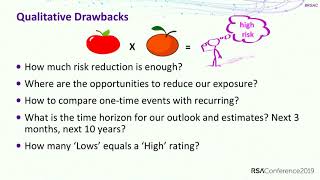
Data Breach or Disclosure - A Quantitative Risk Analysis
Explore quantitative cyber-risk analysis through real-world scenarios, debunking myths and gaining practical tools for data-driven risk management in confidentiality breaches.
AI and Machine Learning - Managing the Risks of Major Lawsuits
Explore legal risks and mitigation strategies for AI and machine learning applications, covering liability issues, algorithmic biases, and emerging challenges in autonomous systems and healthcare.
Integrating Our DevSecOps Product Pipeline with Software Security Standards
Explore strategies for integrating security standards into DevOps pipelines, leveraging automation, and aligning innovation with compliance for efficient product development.

Untangling SaaS Security in the Enterprise
Explore enterprise SaaS security strategies, including controls frameworks, integration patterns, and BYOD solutions. Learn to protect data and manage risks in cloud-based business applications.
Hacking Stress in Cybersecurity Operations
Explore the Hierarchy of Hacker Needs to understand and manage stress in cybersecurity operations, improving job satisfaction and preventing burnout in the information security field.
Beyond the Ballot Box - Securing America’s Supporting Election Technology
Explore securing lesser-known yet critical election technologies. Learn about CIS recommendations, verification processes, and strategies to protect internet-connected election systems from threats.
What's in Your Risk Assessment?
Accelerate your risk assessment approach to meet evolving regulatory demands and stakeholder needs for high-quality decision data in this informative session on effective risk management strategies.