Boeing 737MAX - Automated Crashes - Deutsche Übersetzung
Technische Analyse der Boeing 737 MAX-Abstürze: Ursachen, Systemdesign, Risikobewertung und Zertifizierungsprozesse. Beleuchtet Pilotenkompetenz, Wartungsfehler und organisatorische Mängel bei der Entwicklung des MCAS-Systems.
Boeing 737MAX- Automated Crashes
Análisis técnico y organizativo de los accidentes del Boeing 737 MAX, explorando las causas de los fallos del sistema MCAS, los problemas de diseño y certificación, y las implicaciones para la seguridad aérea.
You Fail in SE If You Make Those Mistakes - DefCamp - 2017
Explore common mistakes in social engineering, learn prevention strategies, and understand the psychology behind successful attacks. Gain insights to enhance your cybersecurity awareness and defense techniques.
Browser Instrumentation for Exploit Analysis - DefCamp 2016
Explore browser instrumentation techniques for analyzing exploit kits, with demonstrations and practical advice for enhancing web security and preventing payload execution.
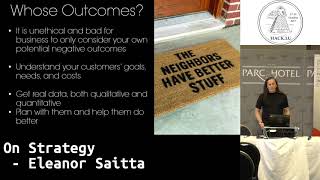
On Strategy
Guidance for development teams on implementing effective security strategies, covering risk assessment, compliance, staffing, and integrating security into organizational culture and processes.
Tools of the Trade for a Modern CISO
Explore essential tools and strategies for modern CISOs, covering organizational roles, security frameworks, risk assessment, and effective communication in evolving cybersecurity landscapes.
An Unknown SAP Default Account
Explore SAP default accounts, their creation, risks, and security implications. Learn about exploits, system users, and solutions to enhance SAP system security.
Game Over, Does the CISO Get an Extra Life
Explore CISO challenges, attack surfaces, and security strategies in this talk on navigating the complex landscape of cybersecurity leadership and risk management.
The Foundation Is Rotting and the Basement Is Flooding
Explore critical vulnerabilities in computing foundations and their impact on security. Learn about technical debt, low-level attacks, and strategies to address information security challenges.
I Know What You Coded Last Summer
Explore SAP system security, custom code risks, and best practices for protecting critical business systems in this comprehensive overview.
The Security Team at the Top - The Board of Directors
Explore how CISOs can effectively engage with boards of directors, build credibility, and leverage this powerful security team to enhance organizational cybersecurity strategies.
All Security Is Good(s)- Design Guidance for Economics - L Jean Camp - USENIX Enigma Conference - 2020
Explore economic aspects of security adoption failures, incentive-aligned design, and the balance between information sharing and privacy, with real-world examples and research insights.
Threat Modeling Cloud Apps - What You Don't Know Will Hurt You
Explore threat modeling for cloud applications, focusing on AWS services, security controls, and potential risks. Learn to identify assets, adapt to cloud architectures, and address new security challenges.
Simplifying Threat Modeling
Simplified approach to threat modeling: identify attack surfaces, visualize users as threats, illuminate assets and trust boundaries, postulate attacks, evaluate impact, and mitigate risks.
Risk Management for Teams That Get Things Done
Explore effective risk management strategies for growing organizations, focusing on peer review, communication, and automation to maintain high uptime standards without sacrificing velocity.
Learning the Power of the -Not My Responsibility- Mindset
Discover how shifting security responsibility to the business can improve accountability, reduce friction, and prevent burnout among security engineers while enhancing overall company security.
Offensive Threat Models Against the Supply Chain
Applying adversarial threat models to supply chain systems, focusing on geo-political risks and industry-specific threats to build effective threat libraries and attack sequences for improved security.
Information Security Risk Assessment - Lessons from the Front Lines
Practical insights on conducting Information Security Risk Assessments for software products, covering methods, tips, and lessons learned to identify and mitigate potential security risks.
We Are the Cavalry - Why It Has to Be Us and Why Now
Exploring cybersecurity challenges in the Internet of Things era, emphasizing the need for proactive measures and collective responsibility to address emerging risks and protect human safety.
Fast Adversaries - Fast Countermeasures
Fast-paced hacking techniques and countermeasures: Learn about adversaries' evolving tools, tactics, and how to protect assets effectively. Explore rapid detection, patching, and risk management strategies.
Authz is the New Authn - Trust Elevation with UMA and OpenID Connect
Explore standards-based trust elevation in online identity using UMA and OpenID Connect for enhanced fraud mitigation and centralized authentication policies in web access management.