Sharks in the Water - Open Source Component Risk and Mitigation
Explore open source component risks and mitigation strategies, focusing on supply chain vulnerabilities, recent hacks, and preventive measures through education and automated tooling.
How to Build an Application Security Program
Practical insights on creating and improving application security programs, drawing from 20 years of experience across various sectors. Covers successful strategies and pitfalls to avoid.
How Do I Get My Company to Ditch the Firewall
Insights on enabling business agility through modern security architectures, simplifying access for global teams while maintaining control over secure access.
Cybersecurity Silver Linings
Explore the economic perspective of cybersecurity, focusing on rational decision-making and the "ROI of Security" in the context of digital transformations and escalating digital risks.
Best Practices and Proactive Strategies to Mitigate Cyberthreats
Explore current best practices and proactive strategies for comprehensive cybersecurity risk management, focusing on assessment, mitigation, and protecting corporate reputation and financial performance.
Managing Cyber-risk - Unlocking the Mystery of the Boardroom
Gain insights into cybersecurity from a Fortune 5 corporate director's perspective, exploring how boards address cyber risks and their impact on organizational strategy and governance.

Planning for Chaos
Explore the evolving cybersecurity landscape and learn strategies to prepare for the age of chaos, where small intrusions can have far-reaching impacts on global institutions and businesses.
Fundamental Flaws in Security Thinking
Explore flaws in security thinking, examining historical assumptions and their impact on modern cybersecurity practices. Gain insights to improve organizational security strategies.
Does DoD Level Security Work in the Real World?
Explore DoD-level security principles for private sector implementation, addressing common misconceptions and emphasizing foundational data protection concepts for effective cybersecurity strategies.
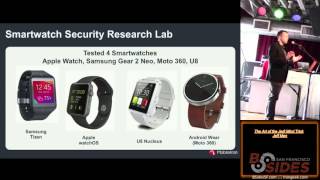
Mobile App Corporate Espionage
Explore real-world corporate espionage techniques using hidden behaviors in mobile apps, focusing on data risk threats and out-of-band communications for leaking sensitive information.
Emerging Best Practices in Software Supply Chain Security - What We Can Learn from Google, the White House, OWASP, and Gartner
Explore emerging best practices in software supply chain security, analyzing guidelines from major organizations to compile key strategies for mitigating risks in deployment pipelines.
DBOM and SBOM - New Options for Better Supply Chain Cybersecurity
Explore new approaches to supply chain cybersecurity using Digital and Software Bill of Materials. Learn how these tools can enhance risk management and component traceability in complex global supply chains.
Supply Chain Security in the Software Era
Explore software supply chain risks and gain insights on mitigating them through real-world examples and concrete recommendations for policy makers and executives.
InfoSec is a Board Responsibility
Elevate InfoSec to a governance issue by speaking 'board talk', addressing objections, and tailoring proposals to focus on measurable benefits, risk mitigation, and corporate objectives.
Embracing Risk Responsibly - Moving Beyond Inflexible SLAs and Exception Hell by Treating Security Vulnerabilities and Risk Like Actual Debt
Discover how to treat security vulnerabilities as debt, moving beyond rigid SLAs and exception overload. Learn strategies for responsible risk management in cybersecurity.
The Trust Landscape
Exploring the impact of digital connectivity on trust in institutions and information, with strategies to redefine risk and restore faith in a hyperconnected world.

Lightning in a Bottle, or Burning Down the House?
Exploring the dual nature of AI in cybersecurity: its potential to strengthen defenses and amplify attacks. Discusses strategies for responsible innovation and delegation of AI across organizations.

Cybersecurity Silver Linings
Explore the 'ROI of Security' concept, shifting cybersecurity discussions from technical to risk-based perspectives, and its impact on digital transformations and decision-making.
Data Integrity - The Elephant Threat in the Room
Explore data integrity threats, their implications, and defensive strategies. Learn to identify potential attacks, implement controls, and understand the far-reaching consequences across various sectors.
A Critical Assessment of Supply Chain Intrusion Vectors
Critical analysis of supply chain attacks, distinguishing between modification and third-party compromise. Explores functionality, execution, and defensive measures, providing insights for risk assessment and mitigation strategies.
Protecting High Risk Users
Exploring challenges in safeguarding high-risk individuals against cyber threats, focusing on targeted attacks, resource constraints, and real-world experiences in assisting vulnerable NGOs and persons.