OWASP Software Assurance Maturity Model - SAMM
Explore OWASP's Software Assurance Maturity Model (SAMM), a framework for improving software security practices across organizations, presented by expert Bart De Win.
OWASP Top 10 - The Making of the OWASP Top 10 and Beyond
Explore the creation process and principles behind the OWASP Top 10, a crucial resource for web application security, including data analysis, likelihood management, and scoring methodologies.
Connecting the Dots: How Threat Intelligence Protects Applications
Explore Cyber Threat Intelligence integration in AppSec programs, automating data collection, and leveraging IoCs and TTPs to prevent and mitigate cyber attacks in today's digital business landscape.
Don't Feed the Hippos - Improving Security Communication with Developers
Explore common security communication failures and learn effective strategies for collaborating with developers to address software vulnerabilities and enhance overall security practices.
Threat Modeling of Containerized Applications - Three Levels of Complexity
Optimize threat modeling for containerized applications, focusing on efficiency, new dimensions, and real-world impact. Learn to measure success and implement incremental improvements in application security.
OWASP Top 10 Maturity Categories for Security Champions
Learn to become an effective Security Champion using OWASP's Top 10 Maturity Categories. Explore key responsibilities, maturity models, and strategies for improving organizational security posture.
Privacy Threat Modeling - Analysis of Cloud Services Against Privacy Regulations
Learn to analyze cloud services for privacy threats and regulatory compliance using threat modeling techniques, enhancing your ability to protect sensitive data.
Measure and Improve Software Supply Chain Assurance with OWASP SCVS
Learn to assess and enhance software supply chain security using OWASP's Software Component Verification Standard (SCVS), improving overall cybersecurity posture.
Blinded by the Weakest Link - A New Perspective on Human Risk in Cybersecurity
Explore a new perspective on human risk in cybersecurity, challenging the "weakest link" mindset and offering innovative strategies to enhance security decision-making and behavior.
Cyber Risk Success Criteria for Board and Executives - Birds and Buttons Approach
Discover effective strategies for communicating cyber risks to non-technical executives and board members. Learn key success criteria and insights from global CxOs to enhance your cybersecurity leadership skills.
Under Assault: Assessing Top Threats to US National Security
Former CIA and National Intelligence directors discuss current external and internal threats to US national security, offering expert insights on pressing global challenges.
Security Metrics: Protecting Our Digital Assets of the Future
Explore security metrics' evolution and importance in protecting digital assets, focusing on people, processes, and technology. Learn to establish effective frameworks for measuring cybersecurity program success.
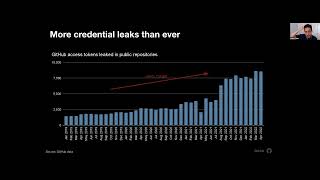
Flipping the Script on Application Security
Explore innovative approaches to application security, challenging traditional methods and introducing fresh perspectives for more effective protection strategies.
Software Supply Chain Security
Explore software supply chain security with expert Vandana Verma, covering key concepts, best practices, and strategies to protect your development pipeline from vulnerabilities and attacks.
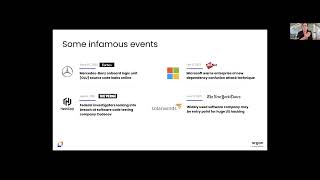
Benchmarking the Security of Your Software Supply Chain
Learn to assess and enhance the security of your software supply chain through benchmarking techniques, improving overall cybersecurity posture and reducing vulnerabilities.
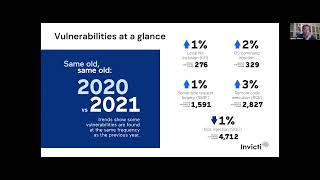
Worrisome Web Vulnerability Trends in the Race to Innovation
Explore concerning web vulnerability trends amid rapid innovation, examining their impact on security and discussing strategies for mitigation and protection.
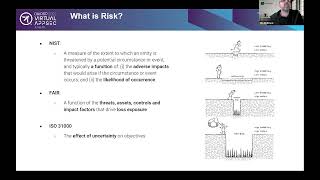
A Risk-Based Approach to API Security
Explore a risk-based approach to API security, focusing on threat modeling, vulnerability assessment, and mitigation strategies to enhance your organization's API protection.
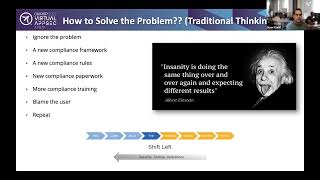
Mitigate Risks in Code - Protect Your Software-based Supply Chain
Explore strategies to mitigate risks in code and safeguard your software-based supply chain, enhancing overall security and resilience in software development.
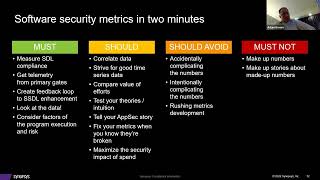
Over a Decade of Software Security - What Have We Learned
Explore key insights and lessons from a decade of software security evolution, highlighting crucial developments and best practices for modern cybersecurity professionals.
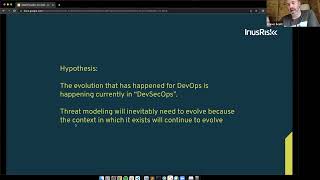
Evolving Threat Modeling Through the Open Threat Model Format
Explore the Open Threat Model Format and its role in advancing threat modeling practices for improved cybersecurity risk assessment and mitigation strategies.
Incorporating Software Assurance with OWASP SAMM V2.1
Enhance software assurance practices using OWASP SAMM V2.1, a comprehensive framework for implementing and measuring security activities throughout the development lifecycle.