Information Security in Mergers & Acquisitions
Explore information security challenges and strategies in mergers and acquisitions, focusing on risk assessment, data protection, and integration of IT systems during corporate transitions.
Mirror, Mirror on the Wall - Am I a Critical Thinker After All?
Explore essential building blocks for improved critical thinking in tech decision-making, breaking biases, and enhancing communication for impactful choices in complex technology landscapes.
Medical Device Security - From Detection to Compromise
Explore vulnerabilities in medical devices and healthcare systems, revealing potential risks to patient safety through a three-year research project on direct attack vectors.
Avoiding the Landmines in Your Own Backyard
Discover strategies to identify and mitigate hidden security risks within your organization's internal network infrastructure and practices.
OMFG China
Explore China's cybersecurity landscape, threats, and strategies in this insightful talk. Gain valuable knowledge about the country's digital infrastructure and its impact on global security.
Ooops Now What - The Stolen Data Impact Model
Explore the Stolen Data Impact Model (SDIM) to understand and mitigate the consequences of data breaches in cybersecurity.
Applying the 32 Zombieland Rules to IT Security - Larry Pesce
Applying Zombieland survival rules to IT security: practical, humorous tips for staying safe in the digital apocalypse.
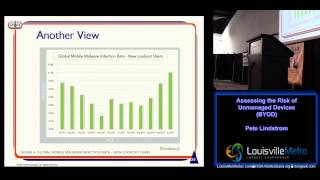
Assessing the Risk of Unmanaged Devices - BYOD
Explore strategies for assessing and mitigating risks associated with unmanaged devices in BYOD environments, enhancing organizational security and data protection.
NIST and Your Risky Application
Explore NIST risk management principles for application security, covering threat sources, assessments, mitigation strategies, and accountability in this informative InfoSec presentation.
Acquisitions - Your Latest Zero Day
Explore the complexities of cybersecurity in acquisitions, covering risk assessment, due diligence, integration challenges, and best practices for ensuring a secure merger process.
Are You a Beefeater Focused on Protecting Your Crown Jewels
Explore strategies for safeguarding critical assets in cybersecurity, drawing parallels to the historic role of Beefeaters protecting the Crown Jewels.
Adopting a Risk-Based Threat Model to Secure Your Defenses and Regain Control of Your Critical Data
Adopt a risk-based threat model to enhance defense strategies and regain control of critical data, improving overall security posture and resilience against cyber threats.
Exercising with Threat Models
Explore practical threat modeling techniques to enhance cybersecurity strategies and identify potential vulnerabilities in systems and networks.
GRC Governance Ruses Confusion
Explore effective GRC governance strategies, avoiding common pitfalls and focusing on practical, business-aligned approaches for successful implementation and evaluation.
Is Threat Modeling for Me
Explore threat modeling essentials, including data flow diagrams, STRIDE methodology, and addressing threats. Learn to identify and mitigate security risks in your systems effectively.
Turn Your Head And Cough - Why Architecture Risk Assessments Are Like Being A General Physician
Explore the parallels between architecture risk assessments and general medicine, focusing on patient interviews, information gathering, and improving outcomes in security architecture.
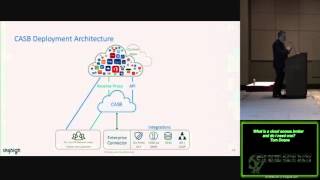
What Is a Cloud Access Broker and Do I Need One
Explore cloud access brokers: their purpose, functionality, and real-world applications in enhancing security, compliance, and risk management for cloud-based data and services.
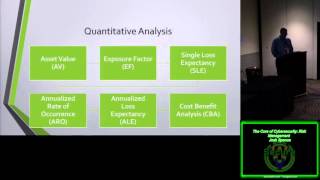
The Core of Cybersecurity Risk Management
Explore the fundamentals of cybersecurity risk management with Josh Spence, focusing on core principles and strategies for effective threat mitigation and protection.
How to Secure Things Influence People - 10 Critical Habits of Effective Security Managers
Discover 10 critical habits for effective security management, focusing on securing assets and influencing people to enhance organizational cybersecurity.
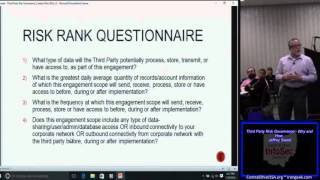
Third Party Risk Governance - Why and How
Explore third-party risk governance strategies, including risk assessment frameworks, questionnaires, and security contracts, to enhance your organization's cybersecurity posture.
Bring Your Own Device and Whatever Security Controls You Want - One Approach to Re
Explore BYOD security challenges and solutions in enterprise environments, focusing on risks, hidden carriers, data protection, and effective implementation strategies.