Securing Your M&A Activity with Cybersecurity Due Diligence
Learn to conduct cybersecurity due diligence for M&A activities, including program components, metrics for informed decisions, and strategies for both buy and sell sides to protect and evaluate effectively.
Build vs Buy - Software Systems at Jurassic Park
Explore software development decisions at Jurassic Park, analyzing build vs. buy strategies, their consequences, and lessons learned to make better choices in system architecture and implementation.
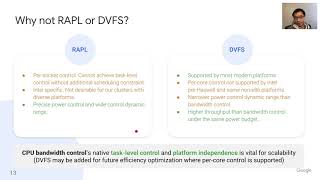
Thunderbolt - Throughput-Optimized, Quality-of-Service-Aware Power Capping at Scale
Explore power capping in data centers with Thunderbolt, a system optimizing throughput and quality of service. Learn about hardware-agnostic solutions for safe power oversubscription and task-level QoS differentiation.
A Systems Approach to Safety and Cybersecurity
Explore systems thinking for safety and cybersecurity, integrating approaches to manage emergent properties and control problems in complex systems.
Designing Cyber Secured Building Management Systems
Learn to identify and address security vulnerabilities in smart building systems, focusing on risk assessment, business continuity, and comprehensive protection strategies.
East vs West - How The Coasts Approach Information Security Differently
Explore the contrasting approaches to information security between Wall Street and Silicon Valley, uncovering valuable insights for professionals across various security roles.
Remember When We Broke the Internet
Exploring unexpected incidents in open source history, their impact on technology, and the complexity of open source ecosystems as sociotechnical systems.
Level Up Your Security Mindset
Upgrade your security approach with collaboration, innovation, and risk-based technology. Learn to adapt to business needs, find the right solutions, and move beyond traditional "no" responses.
Stop That Release, There's a Vulnerability!
Explore BlackBerry's software defect tracking system and risk-based release evaluation process for effective security gating in product development.
Understanding and Exploiting Implanted Medical Devices
Explore vulnerabilities in implanted medical devices, including pacemakers and neurostimulators. Learn about remote exploitation risks, therapy disruption, and patient safety concerns in this technical presentation.
Getting the Most Out of Your Covert Physical Security Assessment - A Client's Guide
Learn effective strategies for covert physical security assessments, including methodology, risk assessment, and practical techniques like drone hacking and badge cloning.
The Emerging Product Security Leader Discipline
Explore product security leadership, covering defense strategies, DevOps integration, threat modeling, and real-world examples. Learn to leverage risks, implement security practices, and adapt to emerging technologies.
The Hitch Hikers Guide to Information Security
Explore key information security concepts through a humorous lens, drawing parallels to "The Hitchhiker's Guide to the Galaxy" for a unique and engaging learning experience.
Usernames, The Missing Piece - The OSINT Jigsaw Puzzle
Explore the risks of shared usernames across services and their significance in OSINT investigations, challenging assumptions about username disclosure and recycling.
Vendors, and Risk, and Tigers, and Bears, Oh My - How to Create a Vendor Review Process From the Ground Up
Learn to create a vendor review management process from scratch using simple tools like email and Google Forms, without expensive software or large teams.
Sure, Let Business Users Build Their Own. What Could Go Wrong?
Explore the risks and challenges of empowering business users with Low-Code/No-Code platforms, examining potential security implications and enterprise-wide impacts.
Blackbox Monitoring for Timely Bug Detection
Discover effective blackbox monitoring techniques for timely bug detection in web applications. Learn task-based hybrid approaches, freshness indicators, and risk markers for improved security.
No InfoSec Staff? No Problem
Learn practical strategies for implementing effective information security measures in small businesses without dedicated InfoSec staff, covering risk assessment, security controls, and awareness.
Brick in the Wall vs Hole in the Wall
Explore the contrasting educational philosophies of "Brick in the Wall" and "Hole in the Wall" approaches, examining their impact on learning outcomes and student engagement.
Adversary Intelligence From Conflict to Consensus
Explore adversary intelligence methodologies, from conflict to consensus, focusing on ground truth analysis, diamond models, and evolving risk perceptions in cybersecurity.
Using the NIST AI Risk Management Framework
Explore the NIST AI Risk Management Framework to identify, assess, and mitigate potential risks associated with artificial intelligence systems in various applications.