Implementing a User-Centric Datastore with Privacy-Aware Access Control for Cloud-Based Data Platforms
Explore user-centric data storage with privacy-aware access control for cloud platforms. Learn about implementation, components, and challenges in this informative talk on secure data management.
Continuous Acceleration: Why Continuous Everything Requires a Supply Chain Approach
Explore the need for a supply chain approach in continuous development practices, emphasizing acceleration and efficiency in modern software security and delivery processes.
Marshalling Pickles - How Deserializing Objects Can Ruin Your Day
Explore vulnerabilities in object serialization across languages, learn exploitation techniques for code execution, and discover protective strategies against deserialization attacks.
Building a Modern Security Engineering Organization
Practical insights on building modern AppSec and NetSec programs, launching bug bounties, and conducting realistic attack simulations in the era of continuous deployment and DevOps.
Building a Better Hacker to Improve Cybersecurity Defense
Explore how understanding hacker mentality bridges the gap between developers and security teams, leading to more effective cybersecurity strategies and proactive threat prevention.
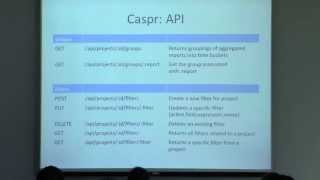
Content Security Policy Reporting and Aggregation with Caspr - OWASP AppSec California 2015
Explore Content-Security-Policy (CSP) violation reporting with Caspr, a tool for collecting and analyzing reports. Learn about CSP background, Caspr usage, and related tools for enhancing web application security.
Securing Software's Future: Why API Design Matters
Explore how API design can prevent vulnerabilities, guide developers towards secure implementations, and shape the future of software security through better development environments.
Why Your AppSec Experts Are Killing You - Evolving to Continuous Application Security
Explore how to evolve into a "Continuous Application Security" organization using instrumentation-based testing, real-time feedback loops, and innovative tools for improved DevOps integration and portfolio-wide assurance.
SQLViking - Pillaging Your Data
Explore SQLViking, a tool for passive SQL query logging and active TCP injection attacks on databases. Learn about network security vulnerabilities and potential countermeasures.
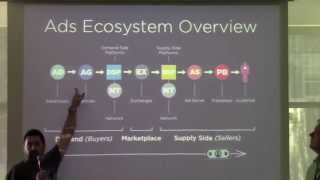
Modern Malvertising and Malware Web-Based Exploit Campaigns
Explore modern malvertising and web-based exploit campaigns, including top malware types, real-world attack breakdowns, and emerging threats in this technical presentation on cybersecurity.
Addressing Security Requirements in Development Projects
Learn effective strategies for integrating security requirements into development projects, covering artifact creation, requirement generation, filtering, and customization.
Leveling Up Your Application Security Program
Learn strategies to enhance your organization's application security program, focusing on key improvements and best practices for robust cybersecurity.
Don't Touch Me That Way - Mobile Application Security Best Practices
Explore secure mobile app development strategies and best practices to protect against common vulnerabilities and attacks in this insightful OWASP conference talk.
Hardening the Web Platform
Explore web platform security with Mike West's keynote on hardening techniques, challenges, and future directions for a more robust online environment.
Making CSP Great Again - Enhancing Content Security Policy
Explore advanced Content Security Policy techniques to enhance web application security and mitigate XSS vulnerabilities effectively.
SAASY SPLC - Secure Application Architecture for Software Product Line Configurations
Explore secure software development lifecycle practices for SaaS applications, focusing on unique challenges and effective strategies in cloud-based environments.
Idiot Proof Is Not Enough: Make It Villain Proof - Application Security
Learn strategies to secure applications against sophisticated attackers, going beyond basic safeguards to create robust, villain-proof systems.
Naxsi: A Web Application Firewall for NGINX
Explore Naxsi, an open-source web application firewall for NGINX, and learn about its features, implementation, and benefits for enhancing web application security.
Security and Modern Software Deployment - AppSec EU 2015
Explore modern software deployment security challenges, including trust issues, dependencies, and repository vulnerabilities. Learn strategies to mitigate risks and enhance deployment security.
Making SSL Warnings Work - Improving Security and User Experience
Explore strategies to improve SSL warnings in Chrome, focusing on reducing false positives and enhancing user understanding of security threats through clear design and communication.
Security Testing Windows Store Apps
Explore security testing for Windows Store Apps, focusing on HTML/JavaScript development, architecture, and potential vulnerabilities in this emerging application model.