OWASP Security Knowledge Framework - Project Overview and Best Practices
Explore OWASP Security Knowledge Framework with project lead Glenn Ten Cate, discussing goals, milestones, and best coding practices for this essential security tool.
OWASP ZAP - More Advanced Features
Explore advanced features of OWASP ZAP, a powerful open-source web application security testing tool, with insights from Simon Bennetts at AppSecEU 2015 in Amsterdam.
Bringing Security Testing to Development: Enabling Developers as Security Experts
Discover strategies for integrating security testing into development processes, empowering developers to become security experts and enhance application safety.
The API Assessment Primer
Learn essential API security assessment techniques, including key considerations, testing steps, and best practices for protecting APIs and mobile applications from common vulnerabilities and threats.
Web Service Workers - Breaking the Web: Exploiting a Cool Feature
Explore Web Service Workers' potential to disrupt web security, examining innovative uses and potential vulnerabilities in this cutting-edge browser feature.
Calm Down: HTTPS Is Not a VPN
Explore HTTPS limitations, privacy concerns, and security implications in web communications. Learn about packet capture, fingerprinting, and potential vulnerabilities in encrypted connections.
Running a Bug Bounty Program - What You Need to Know
Discover essential insights for running successful bug bounty programs, including strategies, resources, and best practices for effective vulnerability management and rewards.
Scanning with Swagger - Using the Open API Specification to Find Vulnerabilities
Explore leveraging Open API specification for enhanced security scanning, uncovering vulnerabilities and improving application protection strategies.
Skillful, Scalable Full-Stack Security in a State of Constant Flux
Approaches to maintaining secure full-stack posture at scale in changing environments. Discusses automation vs. human testing, analytics in continuous security, and scaling with human validation and intelligence.
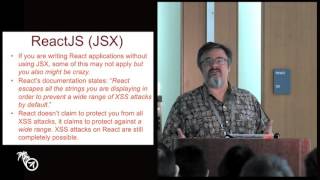
Advances in Secure Coding Frameworks
Explore positive advancements in application security frameworks, highlighting built-in security features that simplify secure coding for developers and improve overall software safety.
Benchmarking Application Security Across Industries
Insights from 200,000+ application assessments reveal industry-specific software security trends, vulnerabilities, and best practices. Benchmark your AppSec program against peers for improved security outcomes.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
OCSP Stapling in the Wild - Lecture
Explore OCSP stapling in the wild with experts Devdatta Akhawe and Emily Stark. Learn about TLS security, browser implementations, and real-world challenges in HTTPS ecosystems.
Serverless Security for DevOps and Defenders
Explore serverless architecture's impact on DevOps and security with James Wickett. Learn how this emerging technology enhances defense strategies and streamlines development processes.
CSP - The Good, the Bad and the Ugly
Explore Content Security Policy's strengths and weaknesses in web application security, presented by Shape Security's engineering manager Ilya Nesterov at APPSEC CA 2017.
An SDLC for the DevSecOps Era
Explore an SDLC tailored for the DevSecOps era with insights on integrating security into modern development practices and organizational culture.
Practical Tips for Running a Successful Bug Bounty Program
Practical tips for running a successful bug bounty program, including scope definition, communication strategies, and vulnerability rating. Insights from experienced professionals on managing crowdsourced security testing effectively.
Why Using SMS in Authentication is Risky and Better Alternatives - AppSecUSA 2016
Explore limitations of SMS-based authentication and discover more secure alternatives using push notifications for improved user experience and enhanced security in two-factor authentication.
Containerizing Your Security Operations Center
Explore containerizing security operations for improved deployment, maintenance, and collaboration. Learn to build a cloud-based SOC using containers, enhancing visibility and streamlining security workflows.
Everything is Terrible: Building, Configuring, and Securing Software - Three Perspectives
Explore perspectives on building, configuring, and securing software from developers, operations, and security experts. Learn strategies for collaboration, empathy, and optimizing workflows across teams.