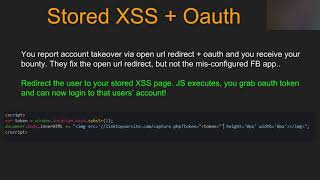
Giving Back to the Bug Bounty Community - ZSeano, Bugcrowd's LevelUp
Learn advanced bug bounty techniques from top hacker ZSeano. Discover web vulnerabilities, improve your skills, and gain insights on professional conduct in the cybersecurity field.
The State of Bug Bounties and Future Trends - Casey Ellis AMA
Insights on bug bounty industry trends, future prospects, and expert Q&A with Bugcrowd's CEO Casey Ellis, covering various aspects of cybersecurity and ethical hacking.

JavaScript for Hackers
Learn JavaScript essentials for ethical hacking with experts @STOKfredrik and @TomNomNomDotCom. Covers Chrome Dev Tools, DOM XSS, debugging, and impact assessment.

Burp Hacks for Bounty Hunters
Discover personal Burp Suite techniques for effective bug bounty hunting, enhancing your web application security testing skills and increasing your chances of finding vulnerabilities.
Overcoming Executive Biases in Cybersecurity Investment
Strategies to overcome executive biases and secure more investment in cybersecurity, including new success metrics and industry comparisons.
Foundations for a Democratic Metaverse
Explore the theoretical foundations and potential implications of a democratic metaverse, examining key concepts and challenges in virtual governance and digital citizenship.
Log4Shell Vulnerability - Bugcrowd Security Flash
Explore the critical Log4Shell vulnerability, its impact, and mitigation strategies in this concise security briefing from Bugcrowd's expert.
Car Hacking Explained for Bug Hunters - Automotive Security Vulnerabilities and Methodologies
Explore automotive security vulnerabilities, from IoT to CAN bus hacking. Learn methodologies, attack surfaces, and bug prioritization for car hacking, covering infotainment systems, APIs, and mobile apps.
Code That Gets You Pwned - Common Vulnerabilities in Golang, Ruby, and Python
Explore non-obvious vulnerabilities in Golang, Ruby, and Python, covering topics like Tempfile, path.Clean, URL parsing, and Unicode security implications.
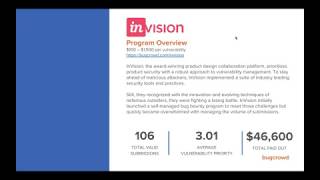
Demystifying Program Management in Crowdsourced Security
Explore expert program management in crowdsourced security testing, focusing on bug bounties and vulnerability disclosure. Learn key strategies for successful implementation and management.
REST in Peace - Abusing GraphQL to Attack Underlying Infrastructure
Explore GraphQL security vulnerabilities, attack techniques, and protective measures. Learn to exploit implementation errors and misconfigurations in this popular API query language.
GSuite Security- Everyone Wants It but Not Everyone Gets It
Explore common GSuite misconfigurations, prevention strategies, and bug hunting techniques. Learn about private docs, Google Sites, API vulnerabilities, and more from an experienced bounty hunter.
Till REcollapse - Fuzzing the Web for Mysterious Bugs
Explore web fuzzing techniques for uncovering mysterious bugs with André Baptista. Learn strategies to identify impactful vulnerabilities and enhance your ethical hacking skills.
Hacking, Content Creation, and API Security with TheXSSRat
Insightful discussion on hacking, content creation, and API security with TheXSSRat. Covers career paths, learning strategies, and practical tips for aspiring cybersecurity professionals.
Hackers Are Hijacking Websites - Subdomain and DNS Takeover
Explore website hijacking through subdomain and DNS takeovers. Learn about vulnerabilities, detection methods, and how to create proof of concepts for securing web assets.
Advent of Cyber - Fuzzing with Burp Suite
Learn fuzzing techniques using Burp Suite in TryHackMe's Advent of Cyber challenge. Enhance your web application security testing skills and discover potential vulnerabilities through automated input manipulation.
Creating Wordlists for Hacking, Pentesting & Bug Bounty Hunting Using Seclists, Bigquery, and More
Learn to create effective wordlists for ethical hacking using tools like Seclists and Bigquery. Enhance your penetration testing and bug bounty hunting skills with expert techniques.
What is Access Control and How Can You Break It?
Explore types of access control and techniques to exploit vulnerabilities, enhancing your understanding of cybersecurity and potential system weaknesses.
Your Guide to Burp Suite - Setup and Usage in 30 Minutes
Learn to set up and effectively use Burp Suite for web security testing in under 30 minutes, covering essential features and functionalities.
Finding and Exploiting Hidden Functionality in Windows DLLs - LevelUpX Series 14
Explore hidden Windows DLL functionality, common bug patterns, and exploitation techniques for bug bounty hunters. Learn tools and methods to uncover vulnerabilities in web servers and network services.
Live Hacking Events - What They Are and How They Work
Explore Live Hacking Events with HackerOne's Community Team. Learn about these unique cybersecurity gatherings, their benefits, and how to participate in this exciting hacking format.