Fun with Frida on Mobile - Leveraging Dynamic Analysis Tools
Explore Frida for mobile app analysis: trace functions, examine memory, bypass security. Practical examples for iOS and Android, including SSL pinning bypass and custom tool creation.
Bug Hunting as a Team: Challenges and Insights - LevelUp 0x04
Insights on collaborative bug hunting: organizing teams, sharing information, splitting bounties, and overcoming challenges in the evolving field of cybersecurity.
LevelUp 0x04: Advanced Bug Bounty Techniques - Day 2
Explore advanced bug bounty techniques and strategies with industry experts in this comprehensive cybersecurity event focused on enhancing hacking skills and knowledge.
iPhone Baseband Research and Reversing - Security Insights and Techniques
Explore iPhone baseband internals, research techniques, and tools for firmware analysis, reversing, and exploitation. Gain insights into Qualcomm baseband architecture and vulnerabilities.
What's in My Hacking Tool Box? by Richard Rushing
Explore a seasoned hacker's toolkit and methodology for penetration testing, covering various domains including malware analysis, mobile app exploitation, and API security.
API Security 101 by Sadako
Explore API security fundamentals, common vulnerabilities, and real-world examples. Learn testing methodologies, fuzzing techniques, and gain insights from notable bug discoveries in this beginner-friendly introduction.
Social Engineering 101 by Matteo Cagnazzo
Discover techniques for gathering company information through OSINT and social engineering. Learn how non-technical methods can complement technical security assessments in bug hunting.
Serverless Top 10 Vulnerabilities by Tal Melamed
Explore serverless security vulnerabilities, their impact, and prevention techniques. Learn how traditional threats evolve in serverless environments and discover best practices for securing cloud-native applications.
Revitalizing Product Security Through Bug Bounty Programs - Zephyr Health Case Study
Discover how implementing a private bug bounty program transformed Zephyr Health's development culture, motivating teams to prioritize security and leverage crowdsourced expertise.
What You Missed During Black Hat and DEFCON - Security Conference Highlights
Explore key highlights from Black Hat and DEFCON, including car hacking, Android security, policy changes, and malware analysis, as presented by Bugcrowd's VP of Operations.
Critical Vulnerabilities and Bug Bounty Programs
Explore critical vulnerabilities uncovered through bug bounty programs, their impact, and strategies for effective vulnerability management and disclosure in cybersecurity.
Hacking with Burp Suite for Bug Bounties - Tutorial 1
Learn essential Burp Suite techniques for bug bounty hunting, including setup and basic functionality, to enhance your web application security testing skills.
Finding Bugs with Burp Plugins and Bug Bounty 101
Learn to create automated testing plugins for Burp and explore bug bounty programs. Gain insights on finding vulnerabilities, tips for success, and valuable resources for cybersecurity enthusiasts.
Fuzzing XSS Sanitizers for Fun and Profit - Tom Anthony
Explore XSS sanitizer fuzzing techniques with Tom Anthony, from his hacking past to current cybersecurity insights. Learn about innovative approaches to discovering vulnerabilities in web applications.
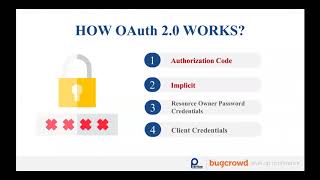
Hacking OAuth 2.0 for Fun and Profit
Discover high-impact vulnerabilities in OAuth 2.0 integrations. Learn attack techniques, methodologies, and case studies for token stealing, code stealing, CSRF, and token impersonation.
Practical Recon Techniques for Bug Hunters & Pen Testers
Discover effective reconnaissance strategies for identifying vulnerabilities and enhancing security assessments in this informative session led by expert Bharath.
Back to Basics - Application Security Practices in Smart Contract Auditing
Explore application security practices in smart contract auditing, focusing on Solidity, common vulnerabilities, security tools, and the growing market for blockchain security engineers.
Identifying & Avoiding Android App Protections - Tim Strazzere, LevelUp 2017
Techniques for quickly identifying and bypassing Android app protections to improve bug bounty hunting efficiency and ROI.
MarkDoom- How I Hacked Every Major IDE in 2 Weeks - Matt Austin, LevelUp 2017
Explore web hacking techniques used to exploit major IDEs and desktop applications, revealing high-severity vulnerabilities in popular development tools.
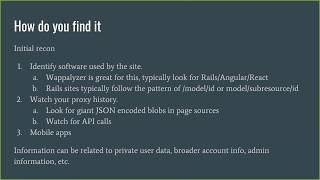
Hidden in Plain Site - Disclosing Information via Your APIs - Peter Yaworski, Bugcrowd's LevelUp 2017
Explore information disclosure vulnerabilities in APIs and HTML sources, focusing on Rails design patterns and front-end frameworks. Learn detection techniques and real-world examples.
Doing Recon Like a Boss - Ben Sadeghipour, Bugcrowd's LevelUp 2017
Learn efficient hacking reconnaissance techniques, including methodologies for Amazon AWS, GitHub, asset identification, and QA, to enhance your cybersecurity skills and target assessment capabilities.