Hacking the Sabbath
Explore the intersection of technology and religious observance, examining innovative solutions for maintaining Sabbath traditions in the modern digital age.
What I've Learned Writing CTF Challenges
Insights from creating Capture The Flag challenges, covering design, development, deployment, and best practices for reliable and educational cybersecurity competitions.
0 to 31337 Real Quick - Lessons Learned by Reversing the Flare On Challenge
Explore reverse engineering strategies and anti-analysis techniques through lessons learned from the Flare-On Challenge, covering file types, encryption methods, and obfuscation tactics.
Challenges and Opportunities in Application Containers and Microservices
Explore challenges and opportunities in application containers and microservices, covering virtualization, orchestration, networking, security, and best practices for modern software delivery.
What is the Size of a Sparse File in NTFS
Explore the intricacies of sparse files in NTFS, understanding their unique properties and how they impact file system management and storage optimization.

WordPress Polyfills for PHP
Explore WordPress polyfills for PHP, enhancing functionality and compatibility across different PHP versions to improve WordPress development.
Predictive Analytics and Machine Learning - Real Use Cases for IT Security Professional
Explore real-world applications of predictive analytics and machine learning in IT security, covering data mining, modeling techniques, and practical implementation strategies.
From Zero to Bender in 12 Months - How a Software Guy Turned Hardware
Learn how a software developer transitioned to hardware hacking, exploring the journey from novice to expert in just one year. Gain insights into the challenges and rewards of this exciting field.
Springtime for Code Reviews - Ryan Goltry
Discover effective code review techniques, focusing on security vulnerabilities, validation, and best practices to enhance software quality and maintainability.
Current State of Virtualizing Network Monitoring
Explore the current state of virtualizing network monitoring, covering prototypes, hardware architecture, logging, and new technologies like containers and Intel X79 XL7.
OPSEC for the Security Practitioner
Explore OPSEC strategies for security professionals, covering credit monitoring, attack surface reduction, identity protection, and personal security measures.
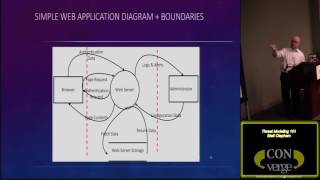
Threat Modeling 101
Learn essential threat modeling techniques to identify and mitigate security risks in software systems, enhancing your ability to build robust and secure applications.
You Have Updates - A Look at an Old Tool Making a Comeback - Evilgrade
Explore Evilgrade, a resurgent tool for exploiting software update processes, and learn about its attack structure, technical factors, and potential applications.
The AppSec Starter Kit
Learn essential tools and techniques for application security, including vulnerability assessment and penetration testing, from expert Timothy De Block.
Estimating Development Security Maturity in About an Hour
Discover techniques for assessing development security maturity quickly. Learn to identify key behaviors, conduct effective meetings, and evaluate training, threat modeling, and analysis practices.
Hurt Me Plenty - The Design and Development of Arganium
Explore the design and development of Arganium, a game-based cybersecurity training platform, including its educational benefits, technical implementation, and future possibilities.
Arming Small Security Programs - Network Baseline - Matt Domko
Learn to establish network baselines for small security programs, covering malware detection, logging, and traffic analysis using tools like Bro and Security Onion.
Easy Indicators of Compromise - Creating a Deception Infrastructure
Learn to create deception infrastructure for detecting attackers, covering security practices, detection tools, and strategies like fake information and admin accounts.
Attacking Modern SaaS Companies
Explore techniques for attacking modern SaaS companies, including breaking into Jenkins, exploiting artifact servers, and leveraging AWS vulnerabilities for unauthorized access.
VR Bleeding Edge of Development and Technology
Explore the cutting-edge developments in virtual reality technology and its impact on future applications with insights from industry expert Arnar Gunnarsson.
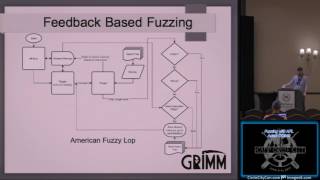
Fuzzing with AFL
Explore fuzzing with AFL, covering traditional methods, monitoring execution, and applications in Google and Windows. Learn about limitations, instrumented fuzzing, and open problems in this field.