Torturing OpenSSL
Explore hardware vulnerabilities in secure systems through a side-channel attack on RSA signatures, demonstrating how induced faults can compromise software-secure systems and extract private keys.
PRNG Pwning Random Number Generators in PHP Applications
Techniques for exploiting randomness vulnerabilities in PHP applications, focusing on password reset token predictability and demonstrating account takeover through PRNG prediction.
Owning Bad Guys and Mafia with Javascript Botnets
Explore mitm attacks on anonymous services and learn to create JavaScript botnets for analyzing connections, uncovering activities of malicious actors behind these services.
File Disinfection Framework - Striking Back at Polymorphic Viruses
Explore an open-source framework for combating polymorphic viruses through advanced static analysis and emulation. Learn innovative techniques for file disinfection, malware analysis, and incident response.
Find Me in Your Database - An Examination of Index Security
Explore Oracle indexing architecture, new flaws, and forensic aspects. Learn to identify issues in custom applications and understand the security implications of database indexing.
Attacking Web Services - Next Generation of Vulnerable Enterprise Apps
Explore vulnerabilities in enterprise web services and learn advanced techniques for identifying and exploiting security flaws in next-generation applications.
The Art of File Format Fuzzing
Explore advanced techniques for file format fuzzing, uncovering vulnerabilities in software applications through systematic input manipulation and analysis.
Injection Flaws - Stop Validating Your Input
Explore injection flaws and learn why input validation alone is insufficient for security. Discover effective strategies to protect against these vulnerabilities in web applications.
CISO Q&A with Jeff Moss
Insightful CISO panel discussion exploring top security challenges, industry trends, and emerging threats in cybersecurity landscape. Covers certifications, zero-day research, and open source risks.
Dex Education - Practicing Safe Dex
Explore Android's dex file format, analyze vulnerabilities in dex analysis tools, and learn techniques to detect post-compilation modifications and protect against potential exploits.
Confessions of a WAF Developer - Protocol-Level Evasion of Web App Firewalls
Explores protocol-level evasion techniques for bypassing web application firewalls, focusing on vulnerabilities in virtual patches and demonstrating real-world examples and countermeasures.
Appliance Firewalls - A Detailed Review
Comprehensive review of network firewall appliances, examining features, vendor claims, and real-world test results of nearly two dozen devices. Uncovers truths behind marketing promises.
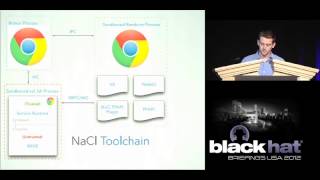
Google Native Client - Analysis of a Secure Browser Plugin Sandbox
Explore Google's Native Client sandbox for Chrome, its architecture, security features, and potential vulnerabilities. Learn about PPAPI and a tool for fuzzing PPAPI interfaces.

HTExploit - Bypassing Htaccess Restrictions
Explore HTExploit, an open-source Python tool that bypasses htaccess authentication, allowing unauthorized directory listing and exposing web security vulnerabilities.
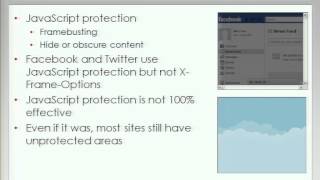
Next Generation Clickjacking
Explore advanced clickjacking techniques, including data injection and extraction, cross-browser vulnerabilities, and a new tool for creating multi-step attacks on web applications.
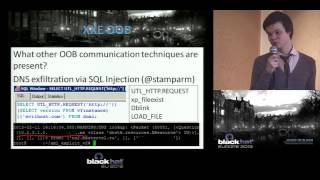
XML Out-of-Band Data Retrieval
Explore innovative XML out-of-band data retrieval techniques for accessing files and resources from victim's machines, even with normal output from vulnerable applications.
Practical Attacks Against MDM Solutions
Explore novel proof-of-concept attack techniques on Android and iOS devices that bypass traditional mobile malware detection and circumvent common Mobile Device Management features.
Off Grid Communications with Android - Meshing the Mobile World
Explore Android mesh networking for resilient, infrastructure-free communication. Learn to implement off-grid concepts, secure networks, and overcome hardware limitations in smartphone ad-hoc networking.
Invisibility Purge - Unmasking the Dormant Events of Invisible Web Controls
Unmasking dormant events in server web controls through refined methodology and new tool, bypassing security measures to exploit hidden application features.
Hardening Windows 8 Apps for the Windows Store
Explore security considerations for Windows 8 Store apps, covering HTML5, backend services, cloud computing, and WinRT to ensure robust and privacy-focused mobile development.
Multiplayer Online Games Insecurity
Explore vulnerabilities in multiplayer online games, including game-specific issues, Steam Browser Protocol security, and a new 0-day vulnerability in a popular game.