Unwrapping the Truth - Analysis of Mobile Application Wrapping Solutions
Explore mobile application wrapping solutions for BYOD, analyzing their security claims, implementation, and vulnerabilities in iOS and Android environments.
A Practical Attack Against VDI Solutions
Explore a practical attack against VDI solutions, demonstrating how malicious apps can exploit screen scraping to bypass security measures and exfiltrate data from remote workstations.
Full System Emulation - Achieving Successful Automated Dynamic Analysis of Evasive Malware
Explore full system emulation for dynamic malware analysis, addressing evasion techniques and solutions. Learn to design effective sandboxes and extract valuable intelligence from malicious files.
Secure Product Development
Explore hardware security validation techniques, Verilog vulnerabilities, and bug resolution methods in open-source core designs. Learn to identify and address security issues in integrated circuits.
Exploiting Unpatched iOS Vulnerabilities for Fun and Profit
Discover techniques for exploiting iOS vulnerabilities, including finding new attack vectors, chaining vulnerabilities, and defeating code signing to jailbreak the latest iOS version.
Dynamic Flash Instrumentation for Fun and Profit
Explore dynamic analysis of malicious Flash files using binary instrumentation, enabling faster and more detailed automatic analysis without decompilation.
Unveiling the Open Source Visualization Engine for Busy Hackers
Open source engine for creating advanced data visualizations, enabling visual learners to interpret complex data sets efficiently. Useful for security practitioners, incident responders, and malware researchers.
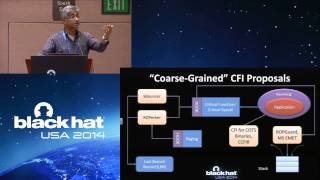
The Beast is in Your Memory
Explore advanced exploitation techniques and control-flow integrity mechanisms. Learn about Return-Oriented Programming, its countermeasures, and how to bypass emerging CFI solutions.
48 Dirty Little Secrets Cryptographers Don't Want You to Know
Explore 48 cryptographic attacks through hands-on challenges, covering block ciphers, public key algorithms, and real-world vulnerabilities. Gain practical insights into crypto exploitation across multiple programming languages.
Contemporary Automatic Program Analysis
Explore automatic program analysis techniques for vulnerability discovery, from historical context to cutting-edge methods, with practical examples and demos for effective security research.
The New Page of Injections Book - Memcached Injections
Explore memcached injection vulnerabilities across popular web platforms, learning attack techniques, potential impacts, and post-exploitation strategies for improved application security.
Call to Arms - A Tale of the Weaknesses of Current Client-Side XSS Filtering
Uncovers 17 flaws in Chrome's XSS Auditor, demonstrating bypasses and presenting a tool for generating attacks. Analyzes filter effectiveness against real-world vulnerabilities, proposing future improvements.
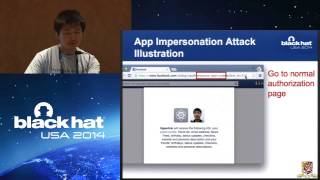
How to Leak a 100-Million-Node Social Graph in Just One Week
Exploración de vulnerabilidades en OAuth 2.0 para redes sociales, demostrando cómo la suplantación de aplicaciones puede llevar a la filtración masiva de datos de usuarios y gráficos sociales.
Building Safe Systems at Scale - Lessons from Six Months at Yahoo
Insights on building secure systems for large-scale internet companies, addressing challenges of surveillance, user privacy, and evolving security threats in the digital landscape.

Pivoting in Amazon Clouds
Explore cloud application vulnerabilities and exploitation techniques in Amazon Web Services, from initial access to gaining root account control. Learn about EC2, SQS, IAM, RDS, and more.
Runtime Analysis of Vulnerabilities and Generation of Exploits
Runtime analysis tool for detecting vulnerabilities and generating exploits. Leverages program execution to identify dataflows, usable for both offensive and defensive purposes. Includes live demonstrations and open-source release.
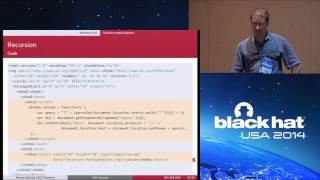
SVG - Exploiting Browsers without Image Parsing Bugs
Explore SVG's hidden potential for web exploitation, including JavaScript execution and external resource imports, challenging traditional browser security assumptions.
The Defense Rests - Automation and APIs for Improving Security
Explore automation and APIs for enhancing security through centralized management, testing, and evidence-driven approaches. Learn to leverage open-source tools and protocols for efficient vulnerability detection and faster recovery.
Exchanging Demands
Explore vulnerabilities in Microsoft Exchange's mobile device management, focusing on remote wipe functionality and potential exploitation through policy updates without authentication.
Libinjection - A C Library for SQLI Detection and Generation Through Lexical Analysis
Innovative C library for SQL injection detection using lexical analysis, offering high precision and accuracy. Trained on real attacks, it categorizes threats and provides templates for new attack detection.
iOS Application Security Assessment and Automation - Introducing SIRA
Automated iOS app security assessment tool SIRA demonstrated, revealing common flaws in AppStore products. Explores risks, testing methods, and future improvements for mobile app security.