Uncovering the Android Patch Gap
Revealing Android security vulnerabilities: analysis of missing patches in vendor firmwares, enabling users to verify patch levels and improve overall protection.
Fuzzing Javascript Engines for Fun and Pwnage
Discover methods for finding vulnerabilities in Javascript Engines through fuzzing techniques, including crash classification, parallel fuzzing, and custom pattern generation for enhanced web browser security.
Rootten Apples - Vulnerability Heaven in the iOS Sandbox
Exploring iOS vulnerabilities beyond containerized apps, revealing multiple privilege escalation flaws affecting all devices and demonstrating a chained exploit to bypass security mitigations.
Everybody Wants SOME - Advance Same Origin Method Execution
Explore advanced Same Origin Method Execution attacks, demonstrating real-world vulnerabilities and new approaches to exploit callback endpoints across major platforms.
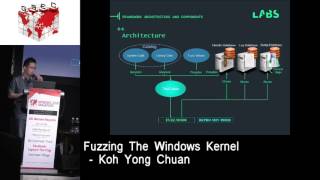
Fuzzing the Windows Kernel
Explore Windows kernel fuzzing architecture, from test-case generation to crash collection. Learn about distributed fuzzing design for effective scaling in this insightful presentation on kernel security.
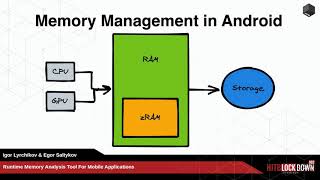
Runtime Memory Analysis Tool for Mobile Apps
Runtime memory analysis tool for mobile apps, automating common checks during penetration testing. Simplifies reverse engineering of obfuscated code for iOS and Android, tracking app behavior changes in real-time.
The Secret Codes Tell the Secrets
Exploración de códigos secretos en dispositivos Android, revelando vulnerabilidades de seguridad y métodos de bypass en teléfonos de principales fabricantes. Incluye demostraciones prácticas y herramientas de fuzzing.
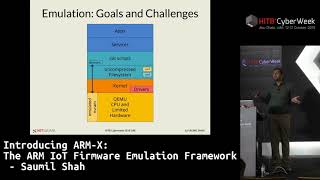
Introducing ARM-X - The ARM IoT Firmware Emulation Framework
Explore ARM-X, an IoT firmware emulation framework for testing and vulnerability discovery. Learn its evolution, use cases, and future directions in IoT security research and development.
Compiler Bugs and Bug Compilers
Explore compiler vulnerabilities and malicious modifications in GCC, from accidental bugs to intentional exploits. Learn about compiler stages, potential attack vectors, and strategies for detecting malicious alterations.
HDMI - Pwning HDMI For Fun And Profit
Explore HDMI vulnerabilities through protocol analysis, fuzzing techniques, and real-world exploitation, showcasing potential security risks in AV devices and demonstrating practical attack vectors.
Reversing Mobile Malware
Explore live malware reversing techniques for Windows and Android, focusing on methodology and essential tools for identifying and analyzing malicious software samples.
Might As Well JUMP - Exploit Development For Java Serialization
Explore Java serialization exploit development, including 0day custom exploits, reverse engineering, and ROP techniques. Learn to break HMAC/MAC and create Python exploits for educational purposes.
Spanish Fly - Infecting Files On-The-Fly
Explore advanced file infection techniques and on-the-fly malware insertion methods with cybersecurity expert Leonardo Nve in this in-depth technical presentation.
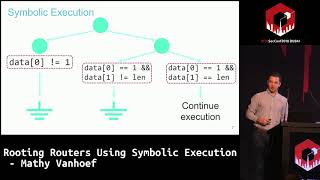
Rooting Routers Using Symbolic Execution
Explore advanced techniques for exploiting router vulnerabilities using symbolic execution, uncovering potential security flaws in network devices.
Creating Browser Extensions to Hunt for Low-Hanging Fruit
Learn to create browser extensions for identifying security vulnerabilities, focusing on low-hanging fruit and efficient hunting techniques.
Crypto for the Public Cloud
Innovative encryption techniques for cloud data security, enabling operations on fully-encrypted data. Learn approaches, tradeoffs, and best practices to maximize security, functionality, and performance in public cloud environments.
Defibrilating Web Security
Exploring fallacies in server-side web security and introducing innovative solutions, including contextual runtime taint tracking for Java and Ruby.
All Fall Down - Interdependencies in the Cloud
Explore cloud system interdependencies, potential cascading failures, and strategies for enhancing resilience in interconnected cloud infrastructures.
Attacking Software Tokens
Exploring vulnerabilities in software OTP tokens, demonstrating reverse engineering techniques and exploits for major vendors' tokens, and assessing obfuscation effectiveness.
Hardware Side Channels in Virtualized Environments
Explore hardware side channel vulnerabilities in virtualized environments, focusing on cloud-based attacks. Learn about attack surfaces, demonstrations, and potential mitigations for these security risks.
Inspeckage - Android Package Inspector
Inspeckage: A tool for dynamic analysis of Android apps. Simplifies runtime behavior observation through a web interface, intercepting library calls and allowing interaction with app components.