Bug Hunting with Static Code Analysis
Explore automated techniques for identifying security flaws in source code, from simple scripts to advanced analyzers, and learn to integrate them into continuous integration systems for early bug detection.
Continuous Security Testing in a DevOps World
Explore continuous security testing in DevOps using BDD-Security framework. Learn to specify requirements, create executable tests, and integrate with CI/CD for on-demand security assessments.
CSRFT - A Toolkit for CSRF Vulnerabilities
Explore a Python-based toolkit for exploiting CSRF vulnerabilities, including demos of complex exploitation techniques and a custom HTTP proxy for injecting malicious iframes.
DFIR - Don't Forget Your Roots
Explore essential DFIR skills, from understanding applications and APIs to analyzing C2 beacons, with insights from an experienced practitioner's career journey.
JWTs and Why They Suck
Explore the pitfalls of JWTs, their unnecessary complexity, and better alternatives for secure authentication in web applications.
When Encryption Fails
Explore encryption vulnerabilities, software development challenges, and security frameworks to enhance your understanding of cybersecurity risks and mitigation strategies.
Automation in Application Security
Discover strategies for preventing application attacks through automation, enhancing security beyond traditional mitigation and detection methods.
MacOS Security - Escaping The Sandbox & Bypassing TCC
Explore macOS security measures, including sandboxing and TCC, and learn about potential vulnerabilities and bypass techniques in third-party applications and system components.
CI - CD With SAST And DAST For Embedded Devices
Explore automated security testing for embedded devices using FOSS, commercial tools, and creative solutions. Learn to implement CI/CD with SAST and DAST for multiple device families at scale.
How to Train Your Self-Driving - Dragon Car
Explore open-source autonomous vehicle technology with Donkey Car. Learn to build, test, and deploy AI networks for self-driving cars using Python, Raspberry Pi, and convolutional neural networks.

Hands-on Introduction to Timeless Debugging & Analysis
Hands-on lab introducing timeless debugging and analysis for reverse-engineering. Learn to navigate from crashes to root causes using REVEN platform on Windows scenarios. Combines GUI and Python API approaches.
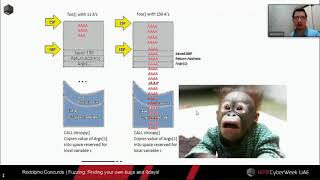
Fuzzing - Finding Your Own Bugs and 0days
Aprenda a criar e usar um fuzzer para encontrar bugs e vulnerabilidades, incluindo técnicas para escrever exploits e obter acesso a sistemas. Demonstrações práticas incluídas.
Spoofing Your Location on iOS Without Jailbreaking
Explore a physical hardware device for GPS spoofing on non-jailbroken iPhones, offering a flexible and accurate solution beyond traditional app-based methods.
The Art of Exploiting Logical Flaws in Web Applications
Exploring techniques to detect and exploit logical vulnerabilities in web applications, focusing on manual testing methods and real-world examples from bug bounty programs.
The Road Towards 365 Bugs in Microsoft Office 365
Discover vulnerabilities in Microsoft 365 applications, including cross-tenant privacy leaks, SQLi, CSRF, SSRF, and XSS. Learn bug hunting techniques and tips for testing new Office 365 features.
AEZAKMI - Browser Anonymity & Fingerprinting Bypass
Explore AEZAKMI, a tool for browser anonymity and fingerprinting bypass. Learn how it obfuscates common parameters to enhance online privacy and support multi-account usage.
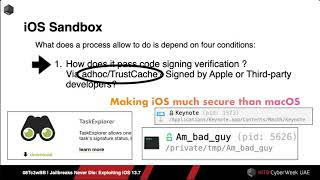
Jailbreaks Never Die - Exploiting iOS 13.7
Unveiling iOS 13.7 exploit chain: kernel vulnerabilities, mitigation bypasses, and techniques for reading/writing kernel memory. Insights into iOS security research and jailbreak development.
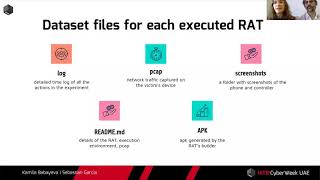
Android RATs Detection With a Machine Learning-Based Python IDS
Explore Android RATs detection using machine learning and Python IDS. Learn about dataset creation, Slips IDS implementation, and live demo of RAT activity detection in mobile device network traffic.
Walk Through Access Control Systems
Exploring vulnerabilities in biometric access control systems, including server command forgery, unauthorized user addition, and face database exposure. Demonstrates exploits to leak employee data and bypass security measures.
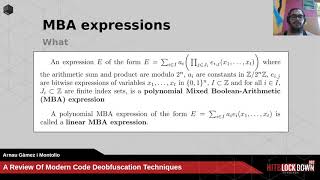
A Review of Modern Code Deobfuscation Techniques
Explore modern code deobfuscation techniques, from basic analysis to advanced semantic-based methods. Learn limitations of syntactic approaches and discover state-of-the-art program synthesis techniques.
Hacking Mobile Games - Closing The Gap
Exploring mobile game hacking techniques to disrupt in-game balances, focusing on monetization strategies and security mechanisms in the current gaming landscape.