Confidential Computing in Genomics - GENXT Cross Database DNA Matching
Explore secure genomic data analysis using Confidential Computing for cross-database DNA matching, enabling privacy-compliant collaborative research in precision medicine.
Share Securely with Data Clean Rooms
Discover secure data sharing and collaboration using BigQuery data clean rooms and partners like Habu for privacy-centric analysis across organizations.

Your Model, Your Data, Your Business: A Privacy-First Approach to Generative AI
Quickly train and fine-tune production AI models using your data, owning your model in the cloud or on-premises with a privacy-first approach.
Security, Privacy, and Governance Considerations for Using AI at Scale
Explore security, privacy, and governance strategies for scalable AI deployment using Vertex AI platform.
A Cybersecurity Expert's Guide to Securing AI Products with Google SAIF
Discover practical strategies for securing AI products using Google's Secure AI Framework (SAIF), addressing key security and privacy concerns in AI development.
Data Sharing Policy in Epidemiological Research - Lecture 7
Explore data sharing policies in research, focusing on ethical considerations, legal requirements, and best practices for responsible data management and dissemination.
Effective Risk Management and AI Security Standards - Episode 138
Explore Google's Secure AI Framework (SAIF) for effective risk management in AI adoption. Learn six core elements, collaboration importance, and practical approaches to address AI security concerns.
EARN-IT Act 2022: The Threat to Encryption and Privacy
Explore the revival of the EARN-IT Act and its potential impact on encryption, privacy, and free speech. Learn about government-mandated backdoors and Section 230 implications.
RESTRICT Act: Beyond the TikTok Ban - Implications for Freedom and Technology
Explore the RESTRICT Act's implications beyond TikTok, examining potential threats to free speech, privacy, and everyday tech like VPNs and encryption.
Decentralized Identity Technical Overview
Explore the technical aspects of decentralized identity, including key projects and frameworks in the Hyperledger ecosystem. Gain insights into enterprise-grade blockchain deployments for identity management.
Telecom Decentralized Identity Network (TDIDN) - Revolutionizing Identity Management in Telecom
Explore TDIDN's innovative approach to revolutionizing identity management in telecom using decentralized identities and blockchain, enhancing security, efficiency, and privacy in the industry.
FedML Nexus AI: Generative AI Platform at Scale - MLOps Podcast #230
Explore FedML Nexus AI, a scalable platform for building and commercializing generative AI applications. Learn about enterprise AI, model deployment, federated learning, and secure, privacy-preserving machine learning.
Federated Learning Tutorial: Concepts, Applications, Challenges, and Framework
Explore federated learning concepts, applications, challenges, and frameworks. Gain insights into collaborative machine learning while preserving data privacy and security.
Federated Learning and Analytics at Google - Workshop Introduction
Explore federated learning and analytics at Google, focusing on privacy principles, data minimization, and innovative techniques for decentralized machine learning.
Federated Learning with Formal User-Level Differential Privacy Guarantees
Explore federated learning with user-level differential privacy guarantees. Discover scalable algorithms for industrial workloads in data privacy and machine learning.
Privacy-Aware Compression for Federated Learning
Explore privacy-aware compression techniques for federated learning, addressing challenges and implementing local differential privacy mechanisms to enhance data protection in collaborative AI.
Secure Self-supervised Learning: Challenges and Solutions
Explore secure self-supervised learning techniques, focusing on backdoor attacks, data auditing, and membership inference for pre-trained encoders in machine learning.
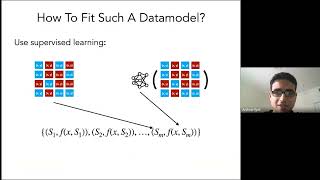
Mapping from Training Data to Predictions with Datamodels - Differential Privacy in Machine Learning
Explore datamodels in machine learning, from training data to predictions. Learn about model brittleness, data counterfactuals, and applications in ML pipelines.
Example Memorization in Learning: Batch and Streaming - Differential Privacy for ML
Explore example memorization in machine learning, covering batch and streaming scenarios, space requirements, and implications for natural models and future research directions.
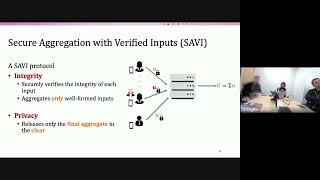
EIFFeL - Ensuring Integrity for Federated Learning
Explore secure federated learning with EIFFeL, a framework ensuring update privacy and integrity while detecting and removing malformed data to prevent model poisoning.
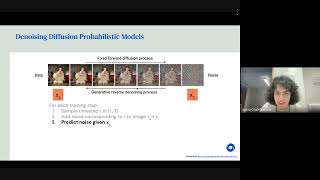
Differentially Private Diffusion Models Generate Useful Synthetic Images
Explore privacy-preserving synthetic image generation using diffusion models. Learn techniques for fine-tuning pre-trained models to achieve state-of-the-art results on CIFAR-10 and Camelyon17 datasets.