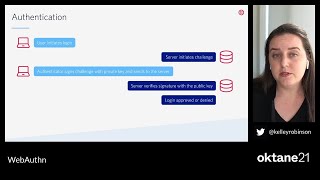
Everything You Want to Know About WebAuthn
Explore WebAuthn, a new authentication standard using everyday devices as phishing-resistant security keys. Learn its workings, applications, and potential for widespread adoption in consumer applications.
Contraction of Markov Kernels and Differential Privacy - Part II
Explore advanced concepts in differential privacy and Markov kernels, focusing on contraction principles and their applications in trustworthy machine learning.
The Saddle-Point Accountant for Differential Privacy
Explore a novel approach to differential privacy using saddle-point techniques, enhancing privacy guarantees in machine learning algorithms and data analysis.
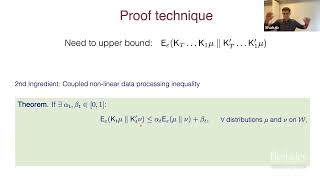
Contraction of Markov Kernels and Differential Privacy - Part I
Explore Markov kernel contraction and its connection to differential privacy in machine learning, focusing on information-theoretic approaches for trustworthy algorithms.
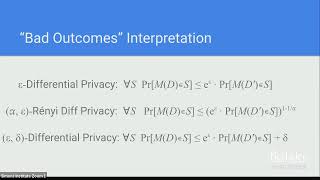
Differential Privacy & Variants
Explore differential privacy and its variants, focusing on information-theoretic methods for enhancing trustworthiness in machine learning algorithms and applications.
How to Fully Anonymize Kali Linux Using Whonix
Learn to enhance Kali Linux's anonymity using Whonix, a secure operating system that routes all traffic through Tor. Discover setup, configuration, and best practices for maximum privacy and security.
Security and Privacy Challenges for Children in K-12 Classrooms
Explores security and privacy challenges in K-12 classrooms, highlighting the need for child-specific design in authentication, permissions, and data protection to ensure safe and effective educational technology use.
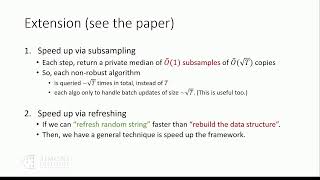
A Blackbox Reduction for Adaptive Adversaries Using Differential Privacy
Explore a novel black-box transformation using differential privacy to convert dynamic algorithms from oblivious to adaptive adversary resistance, enhancing algorithm design for dynamic graphs.
Privacy Detective - Sniffing Out Your Data Leaks for Android
Discover techniques to detect privacy-infringing behaviors in Android apps. Learn about hooking system functions, decrypting TLS traffic, and automating privacy data transmission analysis.
Control, Confidentiality, and the Right to be Forgotten in Differential Privacy for Machine Learning
Explore data deletion, confidentiality, and control in machine learning, focusing on differential privacy and its implications for user rights and model retraining.
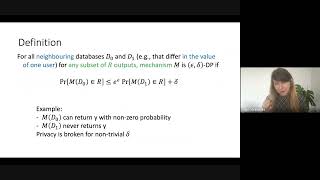
Analog vs. Digital Epsilons: Implementation Considerations for Differential Privacy
Explore implementation considerations for differential privacy, focusing on analog vs. digital epsilons in machine learning applications.
Private Convex Optimization via Exponential Mechanism - Differential Privacy for Machine Learning
Explore private convex optimization using the exponential mechanism. Learn differential privacy, noisy SGD, and isoperimetric inequality for ML applications.
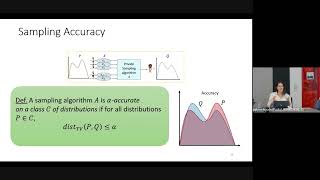
Differentially Private Sampling from Distributions - Google Algorithms Seminar
Explore private sampling from distributions, examining dataset size requirements for various distribution families and comparing private sampling to non-private learning in different parameter regimes.
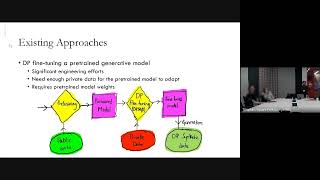
Differentially Private Synthetic Data Generation via Foundation Model APIs
Explore generating high-quality differentially private synthetic data using foundation model APIs, overcoming challenges and achieving state-of-the-art results without accessing model weights.
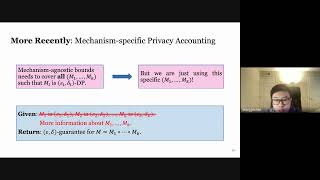
Randomized Approach for Tight Privacy Accounting in Differential Privacy
Explore a novel differential privacy paradigm for improved privacy accounting in compositions, featuring Monte Carlo-based verification and enhanced utility-privacy tradeoffs in machine learning.
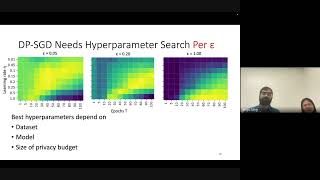
Improving the Privacy-Utility Tradeoff in Differentially Private Machine Learning with Public Data
Explore techniques to enhance privacy-utility balance in differentially private machine learning using public data, focusing on DP-RAFT and DOPE-SGD algorithms for improved model accuracy.

Almost Tight Error Bounds on Differentially Private Continual Counting
Explore novel mechanisms for differentially private continual counting, analyzing error bounds and applications in private optimization. Gain insights into matrix mechanisms and factorization techniques.
Differentially Private Online-to-Batch Conversion for Stochastic Optimization
Explore differentially private stochastic optimization techniques, comparing simple preprocessing and custom algorithms. Learn about a novel online-to-batch conversion method for optimal private convergence rates.
Differentially Private Diffusion Models
Explore privacy-preserving machine learning with differentially private diffusion models, optimizing design for sensitive data and enhancing performance through public pre-training.
A Fast Algorithm for Adaptive Private Mean Estimation in Machine Learning
Explore adaptive private mean estimation with a fast algorithm, focusing on optimal convergence rates, computational efficiency, and adaptability beyond sub-Gaussian distributions.
The Saddle Point Accountant for Differential Privacy in Machine Learning
Explore differential privacy's saddle point accountant method, its composition, and applications in machine learning through expert insights.