Bug Bounty Recon: Bypassing Geographic DNS with Ensemble
Discover how Ensemble revolutionizes bug bounty hunting by bypassing GeoDNS limitations, enabling comprehensive scanning across multiple geographic regions through a distributed cluster of nodes and user-friendly web interface.
Hacking War Stories: From Prison Systems to Tech Companies - A Series of Unfortunate Events
Dive into real-world hacking adventures, from prison systems to major tech companies, exploring identification, exploitation techniques, and potential impact across different organizational contexts.
Smashing the State Machine: Advanced Web Race Condition Attacks
Discover advanced web race-condition attack techniques, from limit-overrun exploits to state machine manipulation, with practical methodologies and tools for identifying and exploiting vulnerabilities.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.
Spooky Authentication at a Distance - Post-exploitation Techniques for Windows Environments
Discover innovative post-exploitation techniques for proxying Windows authentication protocols remotely, enabling user impersonation and domain control without elevated privileges.
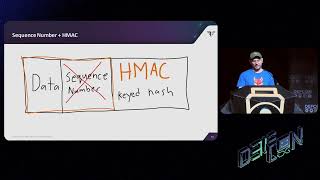
Breaking into Secure Facilities with OSDP - Vulnerabilities and Exploitation Techniques
Uncover critical vulnerabilities in OSDP security protocols and learn practical exploitation techniques for bypassing encrypted RFID systems through demonstrated pentesting tools and methodologies.
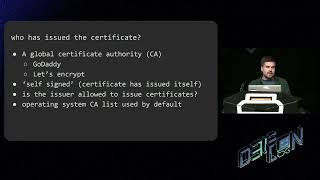
Automatic Exploitation of TLS Certificate Validation Vulnerabilities
Explore TLS certificate validation vulnerabilities and their automated exploitation using certmitm, featuring real-world attacks on iOS and Windows 11 systems.
Defeating VPN Always-On: Security Control Analysis and Bypass Methods
Discover security vulnerabilities in VPN Always-On implementations, exploring bypass techniques and hardening strategies for better network protection and data leak prevention.
Taking Down Applications with Logic - DEF CON 31
Dive into advanced application security techniques and learn how logical vulnerabilities can be exploited to compromise web applications, demonstrated through real-world examples.
BOLABuster - Harnessing LLMs for Automating BOLA Detection
Discover how to leverage LLMs for automated BOLA vulnerability detection in APIs and web applications, exploring BOLABuster's innovative approach to identifying critical security risks at scale.

Beginner's Guide to Hacking IoT Devices - Building Your First IoT Security Testing Lab
Discover practical IoT hacking techniques, from selecting beginner-friendly devices to building an affordable toolkit under $100. Learn common vulnerabilities and methods to gain device access using simple tools and tactics.
Behind Enemy Lines: Engaging and Disrupting Ransomware Web Panels
Dive into advanced strategies for infiltrating and disrupting ransomware operations by targeting their web panels, APIs, and command centers while gathering vital intelligence on threat actors.
Top War Stories from Bug Bounty Hunting - High-Severity Exploits and Discoveries
Dive into real-world bug bounty hunting experiences, exploring high-severity vulnerabilities worth $10k-$60k, from simple RCE exploits to complex PII leakages, with detailed technical insights and lessons learned.
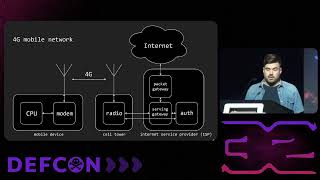
Leveraging Private APNs for Mobile Network Traffic Analysis and Security
Discover how to monitor and control mobile device network traffic using private APNs, enabling affordable security testing and traffic analysis for IoT and mobile devices on 4G/5G networks.

The Darkest Side of Bug Bounty - Understanding Problems and Solutions in Bug Bounty Programs
Uncover the hidden challenges, secrets, and realities of bug bounty programs through expert insights on navigating relationships between hunters, clients, and platforms.
Practical Exploitation of DoS in Bug Bounty Programs
Discover practical techniques for identifying and exploiting DoS vulnerabilities in bug bounty programs, covering N+1 errors, GraphQL crashing, and Cache Poisoning with real-world examples and responsible reporting practices.
Reflections on a Decade in Bug Bounties - From Novice to Seasoned Hunter
Gain insights into the evolution of bug bounty hunting through a decade-long journey, from basic vulnerability reporting to crafting critical impact chains, with perspectives from both hunter and triage sides.
Xiaomi Mobile Security Vulnerabilities - Regional Exploit Analysis and Pwn2Own Competition
Delve into the behind-the-scenes journey of exploiting Xiaomi 13 Pro at Pwn2Own Toronto 2023, exploring regional security variations and the challenges of mobile device exploitation.

Security Testing in the Age of Automation
Explore effective security testing automation techniques, tools, and best practices to detect and prevent vulnerabilities in your applications.

Automated Scanning and Vulnerability Assessment of Web Applications
Leverage tools and frameworks to identify security loopholes, perform penetration testing, and ensure web application resilience against potential attacks.

Definitive Security Testing Checklist - Shielding Your Applications Against Cyber Threats
Unveil a comprehensive security testing checklist to fortify applications against vulnerabilities and attacks, enhancing protection from sophisticated cyber threats.