
Red Teaming Back and Forth 5ever
Explore red teaming strategies, reconnaissance techniques, and unconventional approaches to penetration testing in this humorous and informative cybersecurity talk.
Plunder, Pillage, and Print - The Art of Leveraging Multifunction Printers During Penetration Testing
Explore leveraging multifunction printers in penetration testing, covering plundering techniques, LDAP passback vulnerabilities, and securing your environment against these threats.
Attacking and Defending Full Disk Encryption
Explore full disk encryption's vulnerabilities, attack vectors, and defense strategies. Learn about physical access risks, memory-resident information, and balancing security with convenience.
Checklist Pentesting - Not Checklist Hacking
Learn to create a comprehensive pentesting framework for efficient and thorough security assessments, focusing on methodology rather than specific hacking techniques.
Powershell and Windows Throw the Best Shell Parties
Explore Windows shell parties with PowerShell, learning combat techniques, configuration, and leveraging PowerShell for enhanced system interaction and security testing.
Rawr - Rapid Assessment of Web Resources
Explore rapid web resource assessment techniques, including crawling, scanning, and fuzzing, to enhance cybersecurity and identify potential vulnerabilities in web applications.
Advanced Phishing Tactics Beyond User Awareness
Explore advanced phishing tactics, from email harvesting to payload creation, and learn effective countermeasures beyond user awareness in this comprehensive cybersecurity presentation.
Wielding Katana - A Pentester's Portable Pal
Explore Katana, a portable pentesting toolkit, covering its GUI, bootable menu, documentation, and ideal uses. Learn about Forge setup, antivirus considerations, and BIOS restrictions.
Introduction to Metasploit Post Exploitation Modules
Explore Metasploit post-exploitation modules: structure, development, and integration. Learn to create effective modules, manage data, and contribute to the framework.
New Shiny in Metasploit Framework
Explore Metasploit Framework updates: new commands, modules, and features for various platforms. Learn about privilege escalation, persistence, and reverse operations.
Penetration Testing Trends
Explore current penetration testing trends, challenges in mobile and internal security, and the importance of red teaming with insights from industry expert John Strand.
Command and KubeCTL - Real-World Kubernetes Security for Pentesters
Explore Kubernetes security challenges, attack techniques, and practical advice for pentesters and security practitioners in containerized environments.
Windows Defender - Demystifying and Bypassing ASR by Understanding the AV's Signatures
Explore Windows Defender's undocumented signature format, learn ASR rule implementation, and discover techniques for signature evasion in this comprehensive security analysis.
Jackpotting Fortune-500 Treasuries
Unveiling critical vulnerabilities in ERP systems, demonstrating how attackers can manipulate financial processes and exploit Oracle's ERP for unauthorized monetary gains without detection.
Common Flaws in ICS Network Protocols
Análisis de vulnerabilidades comunes en protocolos de red ICS, incluyendo públicos y privados. Demuestra ataques potenciales como inyección de comandos y sniffing de tráfico sin cifrado en infraestructuras críticas.
How Adversary Emulation Can Enhance Blue Team Performance
Explore adversary emulation to enhance blue team performance, addressing cybersecurity expert shortages and evolving attack methods. Learn to design attack playbooks and test security products effectively.
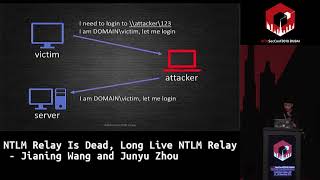
NTLM Relay Is Dead, Long Live NTLM Relay
Explore NTLM relay attacks, their evolution, and modern exploitation techniques. Learn about vulnerabilities in Windows protocols and browsers, with insights on defense strategies.
Exposing Hidden Exploitable Behaviors Using EDF
Exposing hidden exploitable behaviors in programming languages using differential fuzzing. Techniques for identifying undocumented functions, OS command execution vulnerabilities, and other security issues.
Hacking a Hospital for Fun and Profit
Revealing security vulnerabilities in hospital networks through penetration testing, exposing risks in medical devices, software, and systems for improved healthcare cybersecurity.
Faster, Wider, Greater - Modern Pentest Tricks
Explore modern pentesting techniques, tools, and procedures for efficient data processing and analysis. Learn about Jython, PyInstaller, CSVKit, Impacket, Frida, and GNU Parallel to enhance your security auditing skills.
XFLTReaT - A New Dimension In Tunnelling
XFLTReaT: An open-source tunnelling framework for bypassing network restrictions. Simplifies development of custom tunnels, supports various protocols, and offers easy configuration and use for network professionals.