Introducing DeepBlueCLI v2 Now Available in PowerShell and Python
Explore DeepBlueCLI v2's enhanced features for Windows malware detection, including PowerShell and Python implementations, regex improvements, and automated whitelisting techniques.
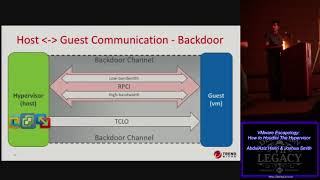
VMware Escapology - How to Houdini The Hypervisor
Explore VMware architecture, vulnerabilities, and escape techniques. Learn about backdoors, PCI, HDFS, and Host Open exploits. Includes live demo and Metasploit module discussion.
Practical Techniques for AV Bypass
Explore practical techniques for bypassing antivirus software, covering various scenarios, tools, and programming languages to enhance your cybersecurity skills.
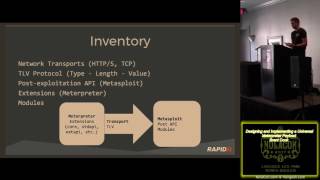
Designing and Implementing a Universal Meterpreter Payload
Explore universal Meterpreter payload design and implementation for embedded exploitation, covering system detection, compatibility layers, and event loops. Learn to build custom payloads for various platforms.
Weaponizing Splunk - Using Blue Team Tools for Evil
Explore how Splunk, a popular security tool, can be exploited for malicious purposes. Learn about vulnerabilities, attack surfaces, and practical demonstrations of potential threats.
Hacking Exposed - LIVE - Bypassing NextGen
Live demonstrations of cutting-edge hacking techniques bypassing NextGen solutions, with insights on defensive strategies and audience participation in attack technique discussions.
Test or Be Tested - Adversary Emulation with Atomic Red Team
Explore adversary emulation using Atomic Red Team to validate EDR tools. Learn about the project's growth, framework, and workflow for creating and contributing tests for ATT&CK techniques.
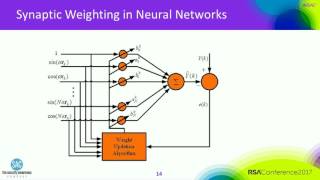
Applying OODA and Feedback Loops to Security Processes
Explore OODA loops and feedback mechanisms to enhance security processes in applications and networks, improving operational stability in ICS, SCADA, and healthcare systems.
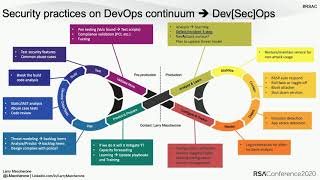
The Impact of Software Security Practice Adoption Quantified
Quantitative analysis of software security practices' impact on risk outcomes, based on data from 200 Comcast teams. Insights on effective strategies for enhancing cybersecurity in diverse tech environments.
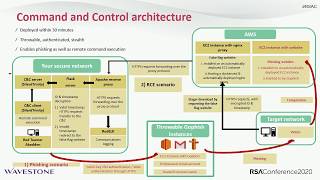
Abaddon - The Red Team Angel
Explore advanced red team operations management with Abaddon, a software designed to enhance efficiency, stealth, and reporting capabilities in complex security assessments.
Drone Penetration Testing and Vulnerability Analysis Framework
Explore an open-source framework for drone security testing, covering attack types and vulnerability analysis. Learn to assess and enhance drone safety in various applications.
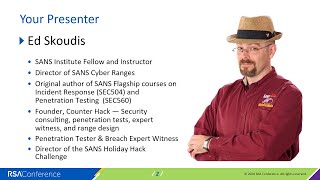
How to Get the Most Value out of Your Penetration Test
Maximize penetration test value: Learn strategies for internal buy-in, aligning with business goals, choosing testers, and evaluating results. Gain practical insights from industry expert Ed Skoudis.
CrackMapExec Owning Active Directory by Using Active Directory
Explore Active Directory exploitation using CrackMapExec. Learn libraries, authentication, payload modules, and execution techniques for effective penetration testing and security assessment.
To Catch a Penetration Tester - Top SIEM Use Cases
Discover top SIEM use cases for detecting penetration testers, including password spraying, antivirus alerts, and unusual account activities. Learn to enhance your organization's security monitoring capabilities.
Going from Capture the Flag to Hacking the Enterprise - Making the Switch from a Hobby
Transition from CTF to enterprise hacking: skills, resources, and career advice for aspiring penetration testers. Practical tips on soft skills, certifications, and common mistakes.
Learning Mainframe Hacking - Where the Hell Did All My Free Time Go
Explore mainframe hacking techniques, from initial denial to acceptance, and learn about tools like Metasploit and shell types for effective penetration testing on legacy systems.
Outside the Box - Hacking
Explore innovative penetration testing techniques, including phishing, physical implants, and token hunting, to enhance security assessments and identify vulnerabilities beyond traditional methods.
Getting Windows to Play with Itself - A Pen Testers Guide to Windows API Abuse
Explore Windows API manipulation for penetration testing, covering DLL injection, persistence techniques, and HTTP exploits. Learn practical skills for enhancing security assessments and understanding system vulnerabilities.
Give Me Your Data - Obtaining Sensitive Data Without Breaking In
Learn techniques for legally obtaining sensitive data, exploring data loss prevention, hardware analysis, and social media investigations with cybersecurity expert Dave Chronister.
Passing the Torch - Old School Red Teaming - New School Tactics
Explore red teaming tactics, from traditional user hunting to modern PowerShell techniques, covering domain trusts, escalation, pivoting, and persistence in Windows environments.

How Not to Suck at Pen Testing
Practical strategies for effective penetration testing, covering scanning techniques, information gathering, and ethical considerations to improve cybersecurity assessments.