Putting an "I" in Code Review - Turning Code Reviewing Interactive - AppSecUSA 2016
Interactive code review techniques using debugging for efficient and effective application security testing, combining penetration testing and code review benefits.
Exploiting CORS Misconfigurations for Bitcoins and Bounties
Explore CORS misconfigurations and their exploitation potential, including real-world examples of vulnerabilities in bitcoin exchanges and major websites. Learn about specification flaws and mitigation strategies.
Automating API Penetration Testing Using Fuzzapi
Explore automated API penetration testing with fuzzapi, addressing common vulnerabilities in REST APIs. Learn to integrate security testing into development pipelines for early detection and mitigation.
Attack Patterns for Black-Box Security Testing - AppSecEU 2016
Explore attack patterns for black-box security testing in web applications, focusing on methodologies and strategies to identify vulnerabilities effectively.
The API Assessment Primer
Learn essential API security assessment techniques, including key considerations, testing steps, and best practices for protecting APIs and mobile applications from common vulnerabilities and threats.
Skillful, Scalable Full-Stack Security in a State of Constant Flux
Approaches to maintaining secure full-stack posture at scale in changing environments. Discusses automation vs. human testing, analytics in continuous security, and scaling with human validation and intelligence.
Adaptive Testing Methodology: Crowdsourced Testing for Customized Target Stack
Discover an efficient, customizable pentesting methodology that adapts to specific technology stacks and time constraints, improving consistency and effectiveness in vulnerability detection.
Marshalling Pickles - How Deserializing Objects Can Ruin Your Day
Explore vulnerabilities in object serialization across languages, learn exploitation techniques for code execution, and discover protective strategies against deserialization attacks.
Why Your AppSec Experts Are Killing You - Evolving to Continuous Application Security
Explore how to evolve into a "Continuous Application Security" organization using instrumentation-based testing, real-time feedback loops, and innovative tools for improved DevOps integration and portfolio-wide assurance.
SQLViking - Pillaging Your Data
Explore SQLViking, a tool for passive SQL query logging and active TCP injection attacks on databases. Learn about network security vulnerabilities and potential countermeasures.
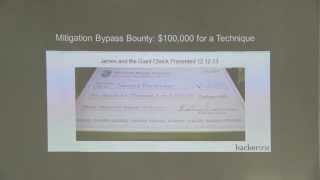
Bounties and the Software Development Life Cycle
Katie Moussouris explores bug bounties, vulnerability disclosure, and their integration into the software development lifecycle. She shares insights on organizational empathy, bounty program implementation, and improving application security.
Leveling Up Your Application Security Program
Learn strategies to enhance your organization's application security program, focusing on key improvements and best practices for robust cybersecurity.
The Cool Factor - Security's Secret Weapon
Explore hacking culture, security's impact on society, and innovative approaches to building a strong security culture program. Learn from industry insights and practical examples.
Shameful Secrets of Proprietary Network Protocols
Reverse engineering proprietary protocols: case studies revealing security flaws in financial software, home automation, and embedded systems. Techniques for uncovering hidden vulnerabilities in undocumented binary protocols.
Sandboxes: Understanding and Exploiting Application Security Limitations
Explore application sandbox vulnerabilities, attack vectors, and exploit techniques for popular sandboxes like Chrome and Adobe Reader. Learn to assess and improve sandbox security.
Mantra OS - Penetration Testing Tools and Methodologies
Explore Mantra OS's penetration testing tools for web application security, including DDoS, SQL injection, and man-in-the-middle attacks. Learn practical methodologies and controlled environment testing techniques.
Mobile App Analysis with Santoku Linux
Explore mobile app analysis using Santoku Linux, covering forensics, security testing, and malware analysis for Android and iOS platforms. Live demos showcase practical applications of preinstalled tools.
Application Security - Challenging Traditional Approaches and Controls
Challenging traditional application security approaches, this talk explores innovative strategies for developing and testing secure software, emphasizing the need for consistency and proactive security measures.
OWASP Hackademic - Teaching Application Security Through Practical Challenges
Practical environment for teaching application security through realistic scenarios with known vulnerabilities. Students discover and exploit vulnerabilities, gaining hands-on experience from an attacker's perspective.
Password Complexity Requirements are Worthless - Effective Password Security Strategies
Debunking password security myths and demonstrating effective methods for creating strong passwords. Explores real-world examples, critiques current practices, and introduces a new open-source tool for better password protection.
Next Generation Red Teaming - Integrating Application-Centric Attacks
Explore advanced red teaming techniques integrating application-specific attack surfaces for more realistic and effective security assessments across multiple domains.