OWASP Zap - Introduction and Usage Guide
Explore OWASP Zap's capabilities for web application security testing with David Scrobonia's comprehensive overview, highlighting key features and best practices for effective vulnerability detection.
Juggling the Elephants - Making AppSec a Continuous Program
Strategies for implementing a continuous AppSec program that integrates security initiatives, enables DevOps, and addresses portfolio-wide coverage while prioritizing risks and fostering continuous improvement.
Open-Source OWASP Tools for Enhancing Penetration Testing Coverage
Explore open-source OWASP tools for efficient white box penetration testing. Learn about Code Pulse for real-time code coverage and Attack Surface Detector for comprehensive endpoint discovery to enhance security assessments.
SDLC for the DevSecOps Era - Adapting Application Security Techniques
Practical lessons on adapting application security techniques for agile development, covering lightweight controls, visibility, and measuring security maturity in modern DevOps environments.
Strategic Defense in Cybersecurity - OWASP AppSec CA 2017
Explore strategic defense in cybersecurity with insights from Kevin Cardwell, an expert consultant with extensive experience in banking, financial institutions, and government red team operations.
SPArring with the Security of Single Page Applications
Explore security challenges in Single Page Applications with insights on automating detection and mitigation strategies for modern web development vulnerabilities.
Threat Modeling for Mobile Applications
Explore threat modeling techniques for mobile applications with expert Amit Sethi. Learn to identify and mitigate security risks in mobile development.
Webhooks Hookups - Abusing API Developers
Explore the security risks of Webhooks in API development, including potential vulnerabilities, real-world examples, and preventive measures. Learn about a new toolkit for auditing Webhook exposure.
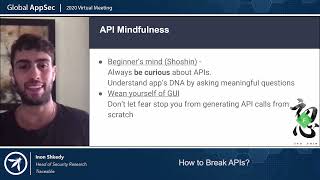
How to Break APIs - Security Testing Techniques
Comprehensive guide to identifying and exploiting vulnerabilities in APIs, focusing on practical techniques for security testing and penetration.
Practical Mobile App Attacks By Example
Explore real-world mobile app vulnerabilities and attack techniques through hands-on demonstrations, enhancing your understanding of mobile security risks and defense strategies.

Hacking and Defending APIs - Red and Blue Make Purple
Learn techniques for both attacking and defending APIs, combining offensive and defensive security perspectives to enhance overall API protection.
Docker for Pentesters
Learn essential Docker techniques for penetration testing, enhancing your cybersecurity skills and improving your ability to identify vulnerabilities in containerized environments.
Helpful Hackers - Keynote by Astrid Oosenbrug
Explore the world of ethical hacking and its positive impact on cybersecurity with insights from Astrid Oosenbrug's keynote address on helpful hackers.

vAPI: Vulnerable Adversely Programmed Interface - OWASP API Top 10
Explore and exploit API vulnerabilities using vAPI, a lab environment mimicking OWASP API Top 10 scenarios. Ideal for developers and penetration testers to understand and address common API security issues.
OWASP Amass Project: DNS Enumeration and Network Mapping
Explore DNS enumeration and network mapping with OWASP Amass, a powerful tool for uncovering organizational internet presence and exposure using multiple data sources.
WAF Bypass Techniques Using HTTP Standard and Web Servers' Behavior
Explore creative techniques to bypass web application firewalls using HTTP standards and server behaviors. Learn to smuggle and reshape requests for penetration testing and bug bounty hunting.
The Bug Hunter's Methodology 2.0 - Advanced Web Application Security Testing
Explore cutting-edge techniques and tools for discovering vulnerabilities in web applications, including XSS, SSTI, SSRF, code injection, and more. Learn from expert Jason Haddix's updated methodology for effective penetration testing.
Hard to Port - A Snapshot of the Vulnerability Landscape in 2015
Explore the 2015 vulnerability landscape through anonymized data, discussing trends, challenges, and the shift towards continuous application security and risk management.

Integrating Mobile Devices into Penetration Testing Programs
Explore techniques for assessing mobile device security risks in enterprise environments, including phishing, undermining controls, and using compromised devices as pivot points.
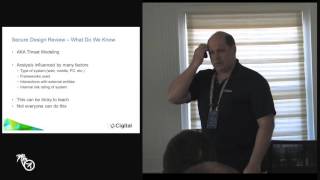
Software Security Initiative Capabilities - Where to Begin
Explore key capabilities for starting a software security initiative, including penetration testing, code review, and secure design review. Learn benefits, drawbacks, and integration into mature security practices.
New Methods in Automated XSS Detection - Dynamic Testing Without Static Payloads
Explore innovative dynamic methods for automated XSS detection without static payloads, including techniques for Stored XSS and custom exploit generation. Learn to overcome limitations of traditional approaches.