What Goes Around Comes Back Around - Exploiting Fundamental Weaknesses in Botnet C&C Panels
Explore techniques for exploiting vulnerabilities in botnet command and control panels, including detection methods, reverse attacks, and automated tools for gathering intelligence.
Putting Intrusion Detection into Intrusion Detection Systems
Explore advanced intrusion detection techniques, focusing on proactive strategies and internal network monitoring to enhance cybersecurity beyond traditional perimeter defenses.
Active & Passive Fingerprinting Microsoft Operating Systems Using ICMP Protocol
Explore active and passive fingerprinting techniques for Microsoft operating systems using ICMP protocol, enhancing network security knowledge and system identification skills.
Honeypots
Explore honeypot technology for network security, including deployment strategies, data analysis, and legal considerations in this comprehensive presentation by Lance Spitzner.

P2P Forensics
Explore peer-to-peer network forensics techniques, uncovering digital evidence and investigating file-sharing activities for cybersecurity and legal purposes.
Intro to Network Traffic Analysis - Part 1
Learn network traffic analysis fundamentals, including packet capture, protocol analysis, and traffic monitoring techniques to enhance your cybersecurity skills and detect network threats.
Intro to Network Traffic Analysis - Part 2
Learn network traffic analysis techniques, including packet inspection and protocol analysis, to enhance your cybersecurity skills and detect potential threats.
Network Situational Awareness with Flow Data
Explore network security monitoring using flow data. Learn to generate, collect, and analyze flow records with tools like SILK and FlowBAT for enhanced situational awareness and threat detection.
Network Forensics Using Kali Linux and SANS Sift
Explore network forensics techniques using Kali Linux and SANS SIFT, learning essential skills for digital investigations and cybersecurity analysis.
Going Deep and Empowering Users - PCAP Utilities and Combating Phishing in a New Way
Explore advanced PCAP utilities and innovative strategies for empowering users to combat phishing attacks effectively.
Network Forensics Using Kali Linux and SANS Sift
Learn network forensics techniques using Kali Linux and SANS SIFT, covering tools and methods for investigating digital evidence and analyzing network traffic.
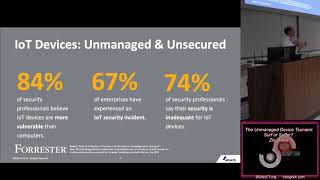
The Unmanaged Device Tsunami - Surf or Suffer
Explore the security challenges of IoT devices in various sectors, including smart offices and healthcare, and learn about recent vulnerabilities and their impact on critical systems.
Traffic Footprint Characterization of Workloads Using BPF
Explore eBPF-based network traffic analysis for containerized workloads, enabling improved scheduling and resource allocation in clusters to enhance performance of diverse applications.
Go at the DARPA Cyber Grand Challenge
Explore how Go's features enabled efficient data capture and analysis during DARPA's Cyber Grand Challenge, with insights on optimization, profiling, and resilience in network traffic handling.
The Golden Age of Bulk Surveillance
Explore bulk surveillance concepts, their effectiveness, implementation, and key industry players. Learn about potential threats and the importance of secure communication in the digital age.
I Know What You Saw Last Minute - The Chrome Browser Case
Explore HTTP Adaptive Streaming vulnerabilities in Chrome, focusing on YouTube's DASH implementation and potential privacy risks through traffic analysis and machine learning techniques.
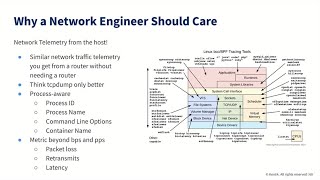
Container Network Observability with Kubernetes and eBPF Technology
Discover how to effectively manage and visualize Kubernetes network traffic using Kentik's observability solutions and eBPF technology for enhanced cluster monitoring and traffic analysis.
Monitoring 400G Traffic in DPDK Using FPGA-Based SmartNIC with RTE Flow
Discover how to monitor 400G network traffic using FPGA-based SmartNIC and DPDK, featuring hardware acceleration techniques and RTE flow configuration for optimal packet processing performance.
Debug Functional and Performance Issues in Rte_flow
Discover effective debugging techniques for rte_flow hardware offloads using MARK, META, COUNT actions and group miss actions to enhance visibility and troubleshoot complex pipeline performance issues.
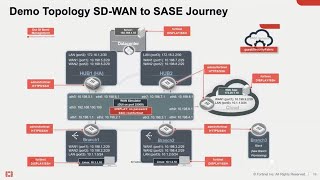
Orchestrating SD-WAN Policies and Monitoring Traffic with Fortinet Secure SD-WAN
Master SD-WAN policy orchestration and monitoring with Fortinet's secure solution, featuring Zero Trust implementation, centralized management, and seamless integration with Security Fabric for enhanced protection.
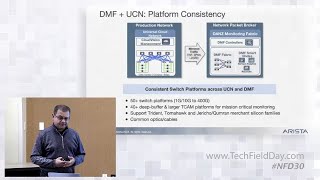
Modern Network Traffic Observability and Packet Broker Architecture
Discover modern network packet broker architecture and integrated observability techniques for automated incident analysis in enterprise networks.