Modmob Tools - Home Made Tools to Test Mobile Devices and Monitor Networks
Explore homemade tools for testing mobile devices and monitoring networks, covering interception techniques, firmware analysis, and hardware auditing for enhanced security understanding.
NetflOSINT- Taking an Often-Overlooked Data Source and Operationalizing It - Joe Gray - Hack in Paris
Explore NetflOSINT: Leveraging overlooked Netflow data for efficient network forensics. Learn extraction techniques, analysis methods, and tools to enhance threat hunting and intelligence gathering.
Getting Better with Data
Learn data-driven strategies to streamline network monitoring, reduce alert fatigue, and optimize your time. Discover tools and processes for effective business intelligence and dashboard creation.
The Crash Course - A Non-Programmer's Guide to Fuzzing
Hands-on workshop for non-programmers to learn fuzzing techniques. Covers environment setup, tools like AFL and Honggfuzz, instrumentation, input selection, and crash analysis. Suitable for beginners to intermediate level.

Building a Cyber Training Range on a Budget
Aprenda a construir um ambiente de treinamento cibernético econômico, abordando hardware, sistemas operacionais, redes, ferramentas e técnicas para simular cenários realistas de segurança.
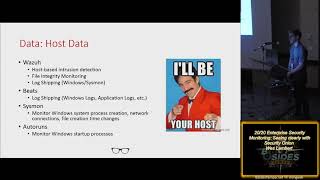
Enterprise Security Monitoring - Seeing Clearly with Security Onion - Wes Lambert
Learn to implement enterprise-level security monitoring using Security Onion, covering tools, data types, interfaces, and deployment strategies for effective threat detection and analysis.
You See Honey, I See Beehive - Developing Honey Networks
Explore end-to-end honey networks for breach defense, combining honeypots, security sensors, and continuous monitoring. Learn open-source and enterprise options for networks of any size.
Think and Act Like a Hacker to Protect Your Company's Assets
Discover how to think like a hacker to protect your company's assets. Learn effective strategies for identifying vulnerabilities, preventing breaches, and implementing robust security measures.
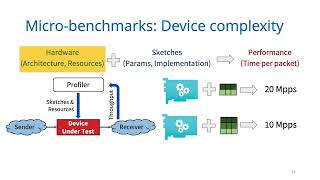
HeteroSketch - Coordinating Network-wide Monitoring in Heterogeneous and Dynamic Networks
Innovative framework for optimizing network-wide monitoring in diverse, dynamic environments. Reduces resource overhead while maintaining performance, coverage, and accuracy through automated profiling and task allocation.
Evolvable Network Telemetry at Facebook
Explore PCAT, a system addressing evolving network telemetry challenges at Facebook through change tracking, intent-based layering, and adaptive design for large-scale production environments.
Network Fault Finding System - Packet Loss Triangulation
Discover how Facebook's active probing system detects network faults in real-time, even in deep layers. Learn to build a similar system using open-source tools and see a live demo.
The GCP Metadata API - Security Considerations, Vulnerabilities, and Remediations
Explore GCP Metadata API security: risks, attacks, defenses, and best practices. Learn about service accounts, Kubernetes, and Cloud Build implications for your organization's cloud infrastructure.
With Friends Like eBPF, Who Needs Enemies?
Explore eBPF's evolution from network monitoring to a powerful Linux kernel observability tool, its security implications, and potential misuse by attackers.
Watching the Watchdog - Protecting Kerberos Authentication With Network Monitoring
Explore advanced Kerberos attack detection techniques and learn to protect Windows networks using network monitoring. Includes a novel "Diamond PAC" attack variant and the "Kerberos Leash" tool.
BGP Stream
Explore BGP Stream: real-time detection of potentially malicious BGP/ASN changes for enhanced network security and traffic flow monitoring.
Enhancing Global Network Monitoring with Magnifier
Innovative approach to enhance global network monitoring by combining sampling with mirroring, improving coverage without increasing overhead. Introduces "negative mirroring" for efficient traffic validation.
Recording at Scale Across Your Global Network Is Essential for Your Cyber Security Posture
Explore essential strategies for global network recording to enhance cybersecurity. Learn about threat landscapes, Netflow, forensics, and cost-effective solutions for improved security posture.
Old Dog, New Tricks - Forensics With PowerShell
Explore PowerForensics: a PowerShell-based toolset for live digital forensics and incident response, enabling efficient investigation of advanced cyber threats without system imaging.
Is That a Government in Your Network or Are You Just Happy to See Me?
Explore techniques for identifying and defending against long-term network intrusions by foreign intelligence agencies, with insights on open-source tools for detecting impersonation attacks.
A New Hybrid Approach for Infrastructure Discovery, Monitoring, and Control
Explore innovative hybrid techniques for network infrastructure discovery, monitoring, and control in this comprehensive cybersecurity presentation by expert Ofir Arkin.
All You Always Wanted to Know About Antiviruses
Demystifying antivirus software: internals, detection methods, and trade-offs. Explores AV engines, whitelists, signatures, real-time monitoring, and network inspection across Windows, Linux, and Android platforms.