
CompTIA Network+ Full Course
Comprehensive networking guide covering theory, hardware, protocols, security, and troubleshooting. Ideal for CompTIA Network+ exam preparation and IT professionals seeking in-depth knowledge.

Zabbix - Open Source, Self Hosted Server, Network, and Device Monitoring System With Power
Learn to install and configure Zabbix, an open-source monitoring system, using Docker. Covers setup, environment variables, web UI overview, and adding client machines for comprehensive network monitoring.
CheckMK - An Open Source, Self Hosted, Network and System Monitoring Tool That Is Easy to Setup
Learn to set up and use CheckMK, an open-source network and system monitoring tool. Covers installation, configuration, and usage of the web UI for effective monitoring of hosts and servers.
A Practical Guide to SNMP Monitoring with Dynatrace
Learn to extend Dynatrace observability using SNMP monitoring. Explore SNMP basics, build custom extensions, and gain hands-on experience with a live demo. Master troubleshooting and discover valuable resources.
Rapid Triage and Lower MTTR with Dynatrace's Role-Focused Platform Apps
Explore Dynatrace's role-focused platform apps for multicloud optimization, covering infrastructure, operations, networks, clouds, and databases through live demos and future roadmaps.
Dynatrace Tips and Tricks - Network Latency, RUM Troubleshooting, and Trace Diagnostics
Explore advanced Dynatrace techniques: network latency monitoring, RUM troubleshooting, and performance hotspot identification. Enhance your observability skills with expert insights.
Wireshark
Learn to use Wireshark for network traffic analysis, covering installation, environment, capture options, filters, OSI model, and tcpdump for comprehensive packet inspection.
Basics of Wireshark Tool
Learn network packet analysis with Wireshark, covering installation, traffic capture, and powerful filters across Windows, Linux, and Mac. Ideal for beginners and intermediate users.
Who's in the Club Room? From FreeRADIUS to ARP Scanner
WiFi 접속 정보를 활용해 동아리방 재실 여부를 확인하는 프로젝트 구현 과정과 문제 해결 방법을 탐구합니다. FreeRADIUS부터 ARP 스캐너까지 다양한 기술을 활용한 접근법을 소개합니다.
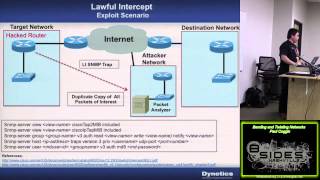
Bending and Twisting Networks: Advanced Router Techniques - Session 300
Explore network security, routing protocols, and advanced techniques for bending and twisting networks to enhance security and control in this comprehensive overview.
The Great Trojan Demo - Understanding Remote Access Tools
Explore remote access tools, network security, and live Trojan demonstrations to understand potential threats and defensive strategies for protecting your digital infrastructure.
Advanced Breaches of 2013 vs Behavioral Detection - GrrCON 2014
Explore advanced breach detection techniques, comparing signature-based and behavioral methods. Learn about NetFlow, metadata analysis, and real-world case studies from 2013 attacks.
Ambush - Catching Intruders at Any Point
Learn advanced techniques for detecting and intercepting network intruders using the Ambush system, enhancing your cybersecurity skills and defensive capabilities.
Netflow for Incident Response
Learn to leverage Netflow data for effective incident response, enhancing network security and threat detection capabilities.
An Introduction to Traffic Analysis - A Pragmatic Approach
Practical introduction to network traffic analysis, covering packet capture techniques, processing mechanisms, performance optimization, and analysis tools for both FreeBSD and Linux systems.
Achieving OT Network Visibility and Detective Controls for NERC CIP Compliance
Explore NERC CIP standards, balancing technology for resilient operations, cybersecurity, and compliance. Learn to choose optimal OT solutions and understand unique operating models for effective implementation.
Dragos Asset Visibility Platform Demonstration for ICS Cybersecurity
Explore ICS network visibility with Dragos platform demo. Learn to identify critical assets, investigate device details, and track communication paths for enhanced OT security and compliance.
Detecting and Understanding Unusual Network Activity in Plant Environments
Explore techniques for identifying assets, understanding threats, and guiding incident response in interconnected plant environments to ensure safe and reliable output.
Collection Management Framework for ICS Security Operations and Incident Response
Extend asset inventory value with a Collection Management Framework for ICS security operations and incident response. Learn to gather requirements, plan, and implement use cases for efficient threat monitoring and response.
Dragos ICS Threat Detection and Response Platform Demo
Comprehensive demo of Dragos platform for industrial cybersecurity, showcasing passive monitoring, threat detection, alerts, case management, and guided response with integrated intelligence and expertise.
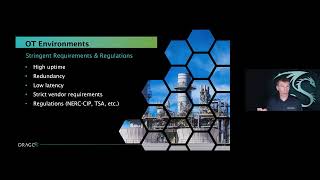
OT Cybersecurity for IT Professionals - Understanding ICS Environments
Explore key differences between IT and OT cybersecurity, focusing on unique challenges in industrial control systems and strategies for aligning people, processes, and technology.