Hacking Exposed - LIVE - Bypassing NextGen
Live demonstrations of cutting-edge hacking techniques bypassing NextGen solutions, with insights on defensive strategies and audience participation in attack technique discussions.
Learning Mainframe Hacking - Where the Hell Did All My Free Time Go
Explore mainframe hacking techniques, from initial denial to acceptance, and learn about tools like Metasploit and shell types for effective penetration testing on legacy systems.
Give Me Your Data - Obtaining Sensitive Data Without Breaking In
Learn techniques for legally obtaining sensitive data, exploring data loss prevention, hardware analysis, and social media investigations with cybersecurity expert Dave Chronister.
Powershell and Windows Throw the Best Shell Parties
Explore Windows shell parties with PowerShell, learning combat techniques, configuration, and leveraging PowerShell for enhanced system interaction and security testing.
Introduction to Metasploit Post Exploitation Modules
Explore Metasploit post-exploitation modules: structure, development, and integration. Learn to create effective modules, manage data, and contribute to the framework.
How Adversary Emulation Can Enhance Blue Team Performance
Explore adversary emulation to enhance blue team performance, addressing cybersecurity expert shortages and evolving attack methods. Learn to design attack playbooks and test security products effectively.
Industrial Control Systems - Pentesting PLCs 101
Hands-on workshop exploring penetration testing techniques for industrial control systems, focusing on PLCs. Learn to identify vulnerabilities and attack Siemens and Schneider devices.
Even The LastPass Will Be Stolen, Deal With It!
Uncover vulnerabilities in LastPass password manager, including methods to steal master passwords, bypass 2FA, and access encrypted vaults, highlighting the importance of robust security measures.
Metasploit Town Hall
Metasploit experts discuss latest developments, answer questions, and share insights on the popular penetration testing framework in this informative town hall session.
Operating in the Shadows
Explore stealthy cybersecurity techniques, evading detection methods, and understanding evolving security controls to enhance operational effectiveness in challenging environments.
Purple Dome - Kein Schwein greift mich an
Simulationsumgebung für Hacking-Angriffe: Testen von Sicherheitssystemen, Beobachtung von Reaktionen und Verbesserung der Systemhärtung mit Purple Dome.
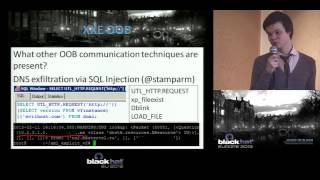
XML Out-of-Band Data Retrieval
Explore innovative XML out-of-band data retrieval techniques for accessing files and resources from victim's machines, even with normal output from vulnerable applications.
Mainframes - The Past Will Come Back to Haunt You
Unveiling mainframe security: Learn configuration, access methods, and potential vulnerabilities in this eye-opening talk for IT security professionals unfamiliar with mainframe systems.
The Dirty Little Secrets They Didn't Teach You In Pentesting Class
Uncover advanced penetration testing techniques, from domain admin strategies to post-exploitation tactics. Learn covert persistence methods and efficient data discovery for enhanced cybersecurity assessments.
Win32 Exploit Development With Mona and Metasploit
Learn advanced Win32 exploit development techniques using Mona and Metasploit, covering vulnerability exploitation, debugging plugins, and protection bypass methods.
Intro to Scanning - Nmap, Hping, Amap, TCPDump, Metasploit, etc.
Learn essential network scanning tools like Nmap, Hping, Amap, TCPDump, and Metasploit for cybersecurity. Gain practical skills in network analysis and vulnerability assessment.
Antipwny - A Windows Based IDS IPS for Metasploit
Explore a Windows-based IDS/IPS for Metasploit, enhancing network security and threat detection capabilities through innovative defense mechanisms.
Intro to Metasploit Class at IU Southeast
Learn essential techniques for penetration testing and ethical hacking using Metasploit, covering installation, exploitation, and post-exploitation strategies for network security assessment.
Macro Malware Lives - Putting the Sexy Back into MS Office Document Macros
Explore advanced macro techniques in MS Office for payload delivery, including PowerShell integration, obfuscation methods, and automation strategies for enhanced effectiveness.
Check Your Privileges - Futzing with File Shares for Low Hanging Fruit
Explore SMB/CIFS vulnerabilities, bad defaults, and privilege escalation techniques in Windows networks. Learn practical security tweaks and tools for identifying and mitigating common file share risks.
The Dark Side of PowerShell
Explore PowerShell's dark side: offensive techniques, persistence, and defense strategies. Learn to leverage and protect against powerful scripting capabilities in cybersecurity.