Steel Mountain Walkthrough - Manual Windows Exploitation
Gain initial foothold and elevate privileges on Windows target by exploiting Unquoted Service Paths manually and with Metasploit. Learn practical techniques for Windows penetration testing.
Metasploit for Detecting Null Sessions and Exploiting Samba Server (SMB)
Explore SMB protocol, enumerate vulnerable Linux machines, and exploit Samba servers using Metasploit Framework's samba_symlink_traversal module. Gain insights into SMB security risks.
Finding and Exploiting Critical Vulnerabilities in RPC Services - NorthSec 2023
Comprehensive walkthrough of finding, exploiting, and reporting critical vulnerabilities in an RPC service, covering reverse engineering, authentication bypass, and coordinated disclosure.
Metasploit Auxiliary Modules Demo - TCP Port Scanners, FTP Login, SSH Version, and SSH Login
Explore Metasploit Auxiliary modules, including TCP port scanners, FTP login, and SSH tools. Learn practical techniques for network reconnaissance and vulnerability assessment.

Ethical Hacking: Using Metasploit to Crack Passwords
Explore ethical password cracking using Metasploit. Learn to create dictionaries, launch attacks, and understand techniques for responsible penetration testing and system security enhancement.
Metasploit Framework Introduction - Modules in Metasploit
Explore Metasploit's core modules: Auxiliary, Exploit, Payload, Encoder, Evasion, and Post-Exploitation. Learn their functions and applications in penetration testing.
Runtime Kubernetes Security: Threat Detection with Falcosidekick
Explore runtime Kubernetes security and threat detection using Falcosidekick. Learn practical scenarios, UI demonstrations, and testing techniques for enhanced cluster protection.
Teaching Old Shellcode New Tricks
Explore advanced techniques to bypass security measures and enhance Metasploit x86 shellcode, incorporating automation for improved effectiveness in various deployment scenarios.
Metasploit Hardware Bridge Hacking
Explore hardware hacking techniques using Metasploit's Hardware Bridge, enabling IoT device exploitation and automotive system penetration testing.
Meterpreter Internals
Dive deep into Meterpreter's inner workings, exploring its lifecycle, Reflective DLL Injection, and migration techniques. Gain technical insights into this powerful Metasploit payload for Windows systems.
Meterpreter - Understanding the New Shiny
Explore Meterpreter's evolution, new features, and advanced techniques for red team engagements. Learn about stageless payloads, transport modification, and persistence to enhance network penetration capabilities.
Is That a Penguin in My Windows?
Explore Windows Subsystem for Linux: architecture, processes, system calls, and security implications. Learn about cross-process access and Linux-Windows interactions.
Implementing Continuous Offense to Measure and Monitor Cybersecurity Defenses - DefCamp - 2019
Explore continuous offense techniques to assess and enhance cybersecurity defenses. Learn about breach simulation tools, vulnerability assessment, and practical strategies for improving network security.
Pen Test War Stories - Why My Job Is So Easy and How You Can Make It Harder
Discover common penetration testing vulnerabilities and learn effective remediation strategies to enhance your organization's cybersecurity posture.
Modern Evasion Techniques
Explore modern evasion techniques for cybersecurity, including Metasploit tips, email controls, Apache ModRewrite, and PowerShell, with practical demonstrations and expert insights.
Bash Can Get Uglier - Using Bashfuscator to Generate Bash Obfuscation
Explore advanced Bash obfuscation techniques using Bashfuscator, from basic methods to complex strategies like subshells and parameter expansions, enhancing your scripting skills.
Introducing DeepBlueCLI v2 Now Available in PowerShell and Python
Explore DeepBlueCLI v2's enhanced features for Windows malware detection, including PowerShell and Python implementations, regex improvements, and automated whitelisting techniques.
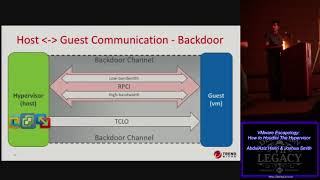
VMware Escapology - How to Houdini The Hypervisor
Explore VMware architecture, vulnerabilities, and escape techniques. Learn about backdoors, PCI, HDFS, and Host Open exploits. Includes live demo and Metasploit module discussion.
Practical Techniques for AV Bypass
Explore practical techniques for bypassing antivirus software, covering various scenarios, tools, and programming languages to enhance your cybersecurity skills.
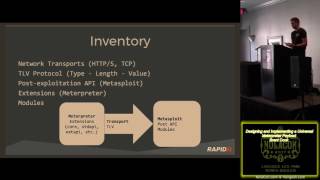
Designing and Implementing a Universal Meterpreter Payload
Explore universal Meterpreter payload design and implementation for embedded exploitation, covering system detection, compatibility layers, and event loops. Learn to build custom payloads for various platforms.
Weaponizing Splunk - Using Blue Team Tools for Evil
Explore how Splunk, a popular security tool, can be exploited for malicious purposes. Learn about vulnerabilities, attack surfaces, and practical demonstrations of potential threats.