Ret2page - The Art of Exploiting Use-After-Free Vulnerabilities in the Dedicated Cache
Explore a new exploitation technique for Use-After-Free vulnerabilities, focusing on SLUB and BUDDY allocators to improve efficiency and success rates in physical page reuse and Android rooting.
Leaving Legacy Behind - Deutsche Übersetzung
Reduzierung des CO2-Fußabdrucks von Netzwerkdiensten durch MirageOS-Unikernels: Minimalistischer Ansatz für sichere Services mit OCaml, kleinen Bibliotheken und geringerem Ressourcenverbrauch.
Leaving Legacy Behind
Reducing carbon footprint and enhancing security of network services using MirageOS unikernels. Explores minimalist approach with OCaml, showcasing various applications and deployment strategies for efficient, secure digital infrastructure.
The Not Fake News Hour
Humorous tech policy update in "SNL Weekend Update" style, covering security, privacy, and current events. Delivered by Stanford researcher at USENIX Enigma conference.
The Limits of Sandboxing and Next Steps
Exploring sandboxing limitations in Chrome security, discussing OS constraints, and introducing memory safety as a complementary approach to enhance software resilience.
Writing Linux Kernel Modules in Safe Rust
Explore safe Rust for Linux kernel module development, addressing memory vulnerabilities, binary compatibility, and C integration. Learn techniques for creating secure kernel APIs and potential upstream integration.
Attacking iPhone XS Max
Explore iPhone XS Max vulnerabilities, including PAC implementation, XNU bug exploitation, and kernel read/write access. Learn about Unix Domain Socket, race conditions, and unprotected control flow transfer points.
Use-After-Use-After-Free - Exploit UAF by Generating Your Own
Explore a novel exploitation technique for UAF vulnerabilities in Adobe Flash, transforming them into multi-class type confusions for full memory access despite recent mitigations.
Level Up Your Concurrency Skills With Rust
Explore Rust's approach to safe concurrent programming, learning how it catches errors at compile time and enhances your skills across languages. Gain insights into race conditions and memory safety.
Taking Kernel Hardening to the Next Level
Explore advanced kernel hardening techniques, focusing on CFI and UAF defense. Learn about new approaches to enhance OS security against evolving exploitation methods.
The Art of Exploiting UAF by Ret2bpf in Android Kernel
Explore Android kernel exploitation techniques, focusing on a Use-After-Free vulnerability in xt_qtaguid. Learn about KASLR bypass, rooting methods, and security measures against such attacks.
The Memory Corruption Safety Dance
Explore memory safety vulnerabilities, their mitigation strategies, and the future of cybersecurity in this comprehensive analysis of defense-in-depth approaches and exploit techniques.
The Power of Pair - One Template that Reveals 100+ UAF IE Vulnerabilities
Discover a unique fuzzing strategy that revealed over 100 IE use-after-free vulnerabilities. Learn about the vulnerability hunting system and techniques used to find critical browser security flaws.
Abusing Silent Mitigations - Understanding Weaknesses Within Internet Explorer
Explore Internet Explorer's silent exploit mitigations, their weaknesses, and potential attack vectors. Learn techniques to bypass these security measures and gain insights into hardening browser defenses.
Rust 2018 - Access All Areas
Explore Rust 2018's versatility across platforms, from microcontrollers to servers. Learn about memory safety, ergonomic improvements, and Rust's unique ability to function in diverse contexts without a runtime.
Exploiting a Limited UAF on Ubuntu 22.04 to Achieve LPE
Detailed exploration of exploiting a Linux kernel vulnerability in Ubuntu 22.04 to achieve local privilege escalation, focusing on advanced exploitation techniques and bypass methods.
Exploiting UAF by Ret2bpf in Android Kernel
Exploiting a 10-year-old Use-After-Free vulnerability in Android's xt_qtaguid kernel module, demonstrating local privilege escalation on Mi9 device using ret2bpf technique to bypass protections.
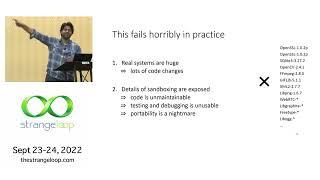
Don't Get Owned by Your Dependencies
Explore innovative techniques for mitigating memory safety vulnerabilities in third-party C libraries, focusing on Firefox's lightweight in-memory sandboxing approach and the RLBox framework for efficient, secure application development.
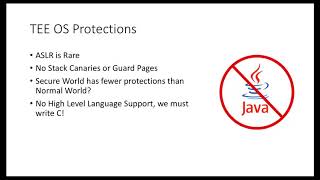
Writing Trusted Applications in Rust
Explore using Rust for Trusted Applications, leveraging its security features like memory safety and error handling for system-level code development in secure environments.
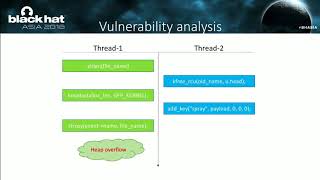
Breaking Android Kernel Isolation and Rooting with ARM MMU Features
Explore a new Android rooting solution, ReVent, exploiting a Use-After-Free vulnerability in 3.18 Linux kernels. Learn about breaking kernel isolation and ARM MMU features for device security.
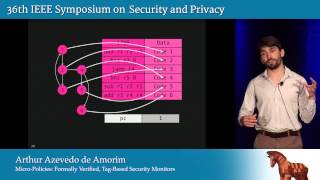
Micro-Policies - Formally Verified, Tag-Based Security Monitors
Explore formally verified tag-based security monitors for low-level policies. Learn about dynamic sealing, compartmentalization, control-flow integrity, and memory safety implementation.