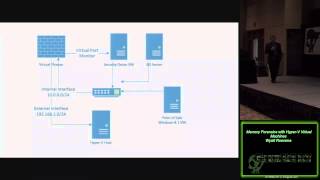
Memory Forensics with Hyper V Virtual Machines
Explore memory forensics techniques for Hyper-V virtual machines, enhancing your ability to investigate and analyze digital evidence in virtualized environments.
Building a Muscle Memory with Rekall Memory Forensic Framework
Explore memory forensics using Rekall framework. Learn process enumeration, malware identification, and rootkit detection techniques. Gain practical skills for digital investigations and incident response.
Memory Acquisition in Digital Forensics and Incident Response
Learn memory acquisition techniques for digital forensics, including hardware and software methods, challenges, and anti-forensic considerations in this comprehensive overview.
Memory Based Library Loading - Someone Did That Already
Explore memory-based library loading techniques and their existing implementations, focusing on advanced cybersecurity concepts and practical applications in system exploitation.
IR with Volatility Framework
Explore incident response techniques using the Volatility Framework for memory forensics and malware analysis in this informative cybersecurity presentation.
Leaving No Stone Unturned
Explore memory forensics techniques for digital investigations, covering attack methodologies and analysis steps. Learn to uncover hidden evidence in volatile memory samples for more comprehensive case insights.
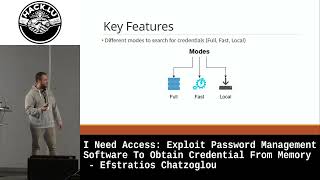
Exploit Password Management Software to Obtain Credentials from Memory
Discover techniques for exploiting password management software vulnerabilities to extract credentials from system memory, focusing on security assessment and penetration testing methodologies.
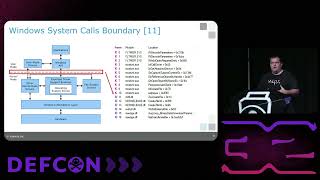
Defeating EDR Evading Malware with Memory Forensics
Discover advanced memory forensics techniques to detect and analyze EDR-evading malware, including system call manipulation, module overwriting, and debug register abuse.
Hivemind - Distributed File Storage Using Javascript Botnets
Explore distributed file storage using JavaScript botnets, covering WebSockets, Redis, and web workers. Learn about data prioritization, network traffic optimization, and potential security implications.
Detecting and Triaging Modern Windows Rootkits
Discover modern Windows rootkit detection techniques, memory forensics, and event log analysis methods to combat evolving kernel-level malware threats in Windows 10 and beyond.
StackMoonwalk: Advanced Memory Evasion Techniques Through Call Stack Tampering
Delve into advanced memory evasion techniques for cybersecurity, exploring novel "Full Moon" and "Half Moon" approaches to call stack tampering, plus learn detection methods using the Eclipse algorithm.