Its Malware Time - A Bar Crawl from Skunked Homebrew to Rotten Apples
Explore the evolution of malware through real-world examples, from initial infection to advanced techniques. Learn detection and prevention strategies for various attack vectors.
Deception at Scale - How Malware Abuses Trust
Explore techniques used by attackers to disguise malware as legitimate, including stolen certificates and hiding malicious files in trusted applications.
pip install malware
Live demonstration of creating and installing malware from PyPI, highlighting security risks in package dependencies and emphasizing the importance of vigilance when using external libraries.
Hackers, Hooligans, Heists, & History
Explore real-life cybersecurity cases spanning decades, from mechanical computers to modern threats. Gain insights into diverse attack motives, actors, and methods, while examining new approaches to enhance security effectiveness.
Defending JavaScript Projects from Supply Chain Attacks - Running Code from the Internet Safely
Explore proactive defenses against JavaScript supply chain attacks, including access control and future JS features for enhanced project security.
Everyday Cybercrime - and What You Can Do About It
Discover everyday cybersecurity risks and learn practical strategies to protect yourself from malware, data breaches, and sophisticated cybercriminals in this eye-opening talk by security expert James Lyne.

Tracking the World's Dumbest Cyber Mercenaries - A Dark Caracal Investigation
Dive into a fascinating investigation of Dark Caracal cyber-mercenaries, exploring their operational blunders, victim patterns, and surprising effectiveness despite major security mishaps.
BadUSB Attacks on MacOS - Beyond Using Terminal and Shell Commands
Discover advanced BadUSB attack techniques for MacOS, leveraging Apple-signed LOLBINs and native scripting languages to execute stealthy code without terminal commands.
The Ouroboros of Cybercrime - From Pwn to Pwned
Explore the cyclical nature of cybercrime as threat actors transition from attackers to victims, examining real-world cases and evolving cybersecurity dynamics.
Wizard Spider: Analysis of Criminal Infrastructure and Threat Group Partnerships
Delve into the uncovered infrastructure and partnerships of Wizard Spider, revealing operational details and connections between major cybercrime groups through OPSEC analysis.
Discord as Malware Infrastructure - Emerging Threats and Attack Trends
Explore how cybercriminals leverage Discord as malware infrastructure and discover emerging threats targeting hackers, with insights into Turkish threat actors' tactics.
Indirect Syscalls: A Journey From High to Low
Dive into the mechanics of system calls, exploring both direct and indirect implementations while understanding their journey from high-level to low-level programming concepts and security implications.
The Current State of Ransomware
Explore the evolving landscape of ransomware threats, attack patterns, and defense strategies through expert analysis of current trends and real-world cases.
MFT: Using NFTs as Attack Vectors for Command and Control
Explore how NFTs can be weaponized as attack vectors for C2 commands, featuring the mFT tool for creating malicious payloads and understanding blockchain-backed threats in cybersecurity.
Relative Path File Injection: The Next Evolution in RPO
Discover how Relative Path File Injection attacks can turn trusted websites into malware delivery platforms, exploring detection methods and real-world implementations through practical demonstrations.
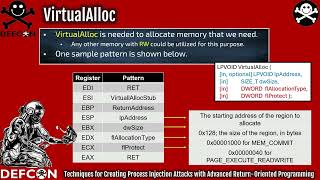
Process Injection Attacks with Return-Oriented Programming - Advanced Techniques and Methodologies
Discover advanced process injection techniques using return-oriented programming (ROP), including unique string comparison solutions, multiple WinAPI patterns, and practical methodologies for reliable implementation.
랜섬웨어 관련 보안 위협 및 대응방안 - 2022
Discover comprehensive insights into ransomware security threats, attack groups, and defense strategies through real-world cases and expert analysis from SK Shields' top security researcher.
Nothing To See Here - On Cloaking Malicious Web Content Delivery
Uncover sophisticated techniques used by cybercriminals to hide malicious web content delivery through cloaking mechanisms and learn effective detection and prevention strategies.
Malware and Hunting for Persistence - How Adversaries Exploit Windows
Discover how adversaries exploit Windows systems through malware and persistence techniques, enhancing your cybersecurity defense capabilities and threat detection skills.
Tactics and Impacts of Adversarial Machine Learning
Explore adversarial attacks on ML systems, AI jailbreaks, and their impact on popular AI models. Gain insights into cybersecurity risks and preparedness strategies in the rapidly evolving AI landscape.
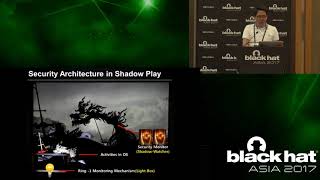
Myth and Truth About Hypervisor-Based Kernel Protector - The Reason Why You Need Shadow-Box
Explore hypervisor-based kernel protection, its limitations, and the need for higher-privilege solutions like Shadow-Box to combat rootkits and kernel exploits effectively.