OPSEC and Personal Security Guide - Cybertalk Episode 7
Comprehensive guide on personal security and OPSEC, covering tools, techniques, and best practices to enhance digital safety and protect against cyber threats.
Invasive Roots of Anti-Cheat Software - Analysis and Detection Techniques
Explore invasive anti-cheat software, its impact on gaming, and detection methods. Learn about rootkits, memory analysis, and the ethical implications of game security measures.
From BYOVD to 0-Day - Unveiling Advanced Exploits in Cyber Recruiting Scams
Unveiling sophisticated cyber-attacks disguised as job recruitment, featuring 0-day exploits and advanced rootkit capabilities. Explores novel attack methods targeting Asia, bypassing security measures.
Breaching the Depths of the Abyss: Exposing Rootkits - Track 2, Session 4
Dive deep into rootkits: explore their inner workings, detection techniques, and countermeasures. Learn to identify and neutralize these stealthy threats using advanced tools like Living Off The Land Drivers.
Windows Systems and Code Signing Protection - Hack.lu 2016
Explores Windows code signing mechanisms, kernel implications, rootkit bypass techniques, and user-land protections, focusing on authenticode and its impact on system security.
Kernelspace Fault Injection with KRF - Discovering Vulnerabilities Through System Call Errors
Explore kernelspace fault injection with KRF to discover vulnerabilities and improve software resilience through targeted system call error induction and analysis.
Breaking Business as Usual: Attacking Android Enterprise Solutions
Explore Android Work Profiles' security, threats, and vulnerabilities in enterprise settings. Learn about stakeholder perspectives, potential exploits, and actionable steps for enhancing mobile security configurations.
Tracing: The Bane of Security Folks - Understanding Kernel Tracing Techniques
Explore kernel tracing techniques, their security implications, and the tension between transparency and protection in Linux systems. Learn about live patching and function tracing methods.

The Advanced Threats Evolution- REsearchers Arm Race - Alex Matrosov - Ekoparty Security Conference - 2019
Explore the evolution of advanced threats and defensive software, focusing on persistent methods at hardware and firmware levels. Gain insights into modern security gaps and potential solutions.
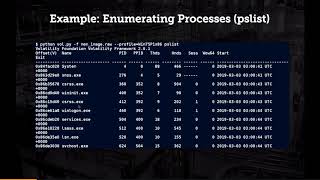
Investigating Malware Using Memory Forensics - A Practical Approach
Practical approach to memory forensics for malware detection and investigation, covering techniques, demonstrations, and analysis of various malware types and rootkits.
Demystifying Modern Windows Rootkits
Explore Windows rootkit development, from basic drivers to advanced hooking techniques. Learn about kernel-mode malware, network stack manipulation, and innovative methods to evade detection.
Exploring Yosemite - Abusing Mac OS X 10.10
Comprehensive analysis of Mac OS X 10.10 Yosemite's security features, demonstrating vulnerabilities, offensive techniques, and introducing a new security tool for detecting rootkits and abnormalities.
Orchestrate This! Kubernetes Rootkit
Explore container-focused rootkits in Kubernetes, their anatomy, potential consequences, and strategies for mitigating risks and securing clusters against such attacks.
BlackBerryOS 10 from a Security Perspective
Comprehensive analysis of BlackBerryOS 10's security architecture, exploring attack surfaces, privilege escalation, remote entry points, rootkit persistence, and the effectiveness of BlackBerry Balance.
Close Encounters of the Advanced Persistent Kind - Leveraging Rootkits for Post-Exploitation
Explore advanced Windows kernel post-exploitation techniques, including 0-day vulnerability exploitation, DKOM for altering OS telemetry, and NDIS modules for disrupting EDR cloud telemetry and establishing covert persistence.
Myth and Truth About Hypervisor-Based Kernel Protector - The Reason Why You Need Shadow-Box
Explore hypervisor-based kernel protection, its limitations, and the need for higher-privilege solutions like Shadow-Box to combat rootkits and kernel exploits effectively.
Kernel Games: The Ballad of Offense and Defense in Rootkit Methodologies
Dive into advanced kernel rootkit techniques for red team operations and defense strategies, covering stealthy persistence, EDR evasion, and practical detection methods with hands-on demos.

Black Hat USA 2025
Black Hat USA 2025

Black Hat Asia 2025
Black Hat Asia 2025