Breaking Barriers and Boundaries in IT Security - TROOPERS24
Explore cutting-edge IT security insights with experts Alexander Heinrich and Jiska Classen at TROOPERS24 conference, focusing on breaking barriers and pushing boundaries in cybersecurity.
Leveraging Online Sandboxes for Triage Analysis - MM#07
Explore popular online sandboxes for malware analysis, including AnyRun, Triage, and VirusTotal's behavioral output. Learn effective techniques for leveraging these tools in investigations.
Analyzing Malicious Network Traffic with Suricata - Malware Mondays Episode 06
Learn to analyze malicious network traffic using Suricata in REMnux. Explore alert generation, protocol dissection, file identification, and contextual flow information for effective threat detection.
The AddressOfEntryPoint and Tips for Finding Main in PE Files
Explore the AddressOfEntryPoint field in PE files, its relation to the main function, and techniques for locating it. Learn about PE file structure and entry point analysis.
TLS Callbacks in PE Files - Detection and Analysis
Explore TLS callbacks in PE files, their use in malware, and detection methods. Learn to identify and analyze these anti-debugging techniques using various tools and Yara rules.
Finding Digital Certificates in PE File Format
Learn to identify and extract digital signatures in PE files using the DATA_DIRECTORY structure, RVAs, and tools like Malcat for enhanced cybersecurity and malware analysis skills.
Tales from Incident Response - Unmasking the Threat Actor's Inner Sanctum
Unmasking threat actors' inner workings through incident response tales. Gain insights into cybersecurity challenges and strategies from a principal advisor's real-world experiences at a major hacking conference.
War Stories from the SOC - Cybersecurity Incident Response Lessons
Cybersecurity expert shares real-world experiences from Security Operations Center, offering insights into threat detection, incident response, and best practices for defending against cyber attacks.
Performing Basic Triage Analysis and Unpacking with x64dbg - Ransomware Analysis - Part 2
Perform basic triage analysis on ransomware binaries, compare obfuscated and unobfuscated versions, and learn to unpack using x64dbg and Scylla for effective malware analysis.
Open-source Projects in Cyber Security
Explore open-source cybersecurity projects, including YARA-related tools like GenRex, YARI, and YLS. Gain insights into innovative developments enhancing malware analysis and industry protection.

Lockbit's DLL Name Seeding Technique for API Hashing - Part 5
Explore Lockbit's runtime-linking technique, focusing on DLL name usage for API hashing seed creation and its impact on reverse engineering efforts.
Identifying Signs of Runtime-Linking and Building Context for API Hashes in Lockbit Malware - Part 3
Explore Lockbit's runtime linking techniques and API hash obfuscation. Learn to reverse engineer malware by understanding dynamic import table construction and decoding precomputed values.
Integrating Cyber Security and Machine Learning for Applications in Transportation Systems
Explore integrating cybersecurity and machine learning in transportation systems. Learn about challenges, research, and innovative solutions for securing Internet of Transportation and Intelligent Transportation Systems.
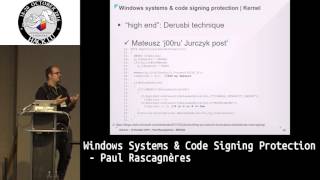
Windows Systems and Code Signing Protection - Hack.lu 2016
Explores Windows code signing mechanisms, kernel implications, rootkit bypass techniques, and user-land protections, focusing on authenticode and its impact on system security.
The Art of Compromising Command and Control Servers - A Web Application Vulnerabilities Perspective
Dive into techniques for exploiting command and control server vulnerabilities, uncovering infrastructure weaknesses, and exposing threat actors through common web application security flaws.
Runtime Riddles: Abusing Manipulation Points in the Android Source
Delve into advanced Android runtime manipulation techniques for bypassing decompilers and emulators, featuring practical demonstrations of native C++ manipulators and custom library implementation.
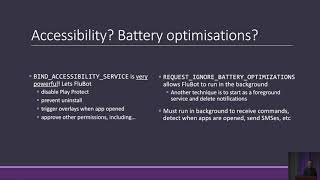
FluBot
Explore the inner workings of FluBot, an Android malware that impersonates banking apps, and learn about its sophisticated countermeasures against detection and analysis.
Asm2Vec - Boosting Static Representation Robustness for Binary Clone Search
Innovative assembly code representation learning model for robust binary clone search, addressing challenges in reverse engineering against code obfuscation and compiler optimization.
Android App Protection Techniques: Obfuscation, Packing, and Protection - APPSEC Cali 2018
Explore Android app protection techniques, including obfuscation, packing, and protection. Learn to analyze and counter these methods to identify potential malware and enhance app security.
CopperDroid: Reconstructing Android Malware Behaviors
Explore CopperDroid, an innovative system for analyzing Android malware behaviors through VMI-based dynamic analysis, capturing both OS-specific and Android-specific actions to enhance mobile security.
AMD Hypervisor Implementation in Rust
Explore the process of creating an AMD hypervisor using Rust, discussing its applications in FaaS, virtual machines, and security, as well as potential misuse in malware and game hacks.