Meet Operational Challenges with MISP on an Air-Gapped Network
Explore strategies for implementing MISP on air-gapped networks to address operational challenges in secure environments.
HZ Rat Goes China - Following the Tail of an Unknown Backdoor
Uncover the journey of an elusive backdoor malware as it traverses from Europe to China, exploring its origins, capabilities, and potential impact on cybersecurity.
The Glitch in the Matrix
Explore advanced malware analysis techniques and cutting-edge evasion methods used by sophisticated threats. Gain insights into detecting and countering elusive malicious software.
Introducing HAMISPA - High Availability MISP in AWS
Learn to deploy a highly available MISP (Malware Information Sharing Platform) in AWS for enhanced threat intelligence sharing and collaboration.
The New Indicator Scoring Method Introduced in MISP 2.4.116
Explore the updated indicator scoring system in MISP 2.4.116, enhancing threat intelligence analysis and improving decision-making for cybersecurity professionals.
KillTheHashes - 30 Million Malware DNA Profiling Exercise - Hack.lu 2016
Explore malware profiling techniques and tools for identifying unique digital fingerprints, enabling early detection and categorization of new threats through characteristic family analysis.
MISP Project - One Year of Improvements
Explore recent advancements in the MISP threat intelligence platform, including enhanced features, improved performance, and expanded capabilities for cybersecurity professionals.
Let Me YARA That For You
Explore advanced YARA rule creation techniques for malware detection and analysis, enhancing your cybersecurity skills and threat hunting capabilities.
The Telenovela of Latin American Banking Trojans - A Dramatic Story About Cybercrime
Uncover the dramatic rise of Latin American banking malware, exploring their anatomy, tactics, and global impact. Learn why these cybercrime threats are so persistent and difficult to eradicate.
OH-SINT: Merging OSINT Into Reverse Engineering Workflows to Simplify Analysis
Leveraging OSINT in reverse engineering to overcome anti-analysis techniques, track down information from developers, and speed up malware analysis workflows for quicker insights.
Ongoing EvilEye Campaigns Targeting CCP Adversaries
Explore ongoing EvilEye campaigns targeting CCP adversaries, analyzing tactics, targets, and implications for cybersecurity professionals and policymakers.
Malware AV Evasion Tricks - Cryptography in Malware
Explore advanced malware evasion techniques using cryptography, enhancing your cybersecurity knowledge and defensive strategies against sophisticated threats.
MISP Updates - Hack.lu 2023
Explore the latest updates and enhancements to MISP, the open-source threat intelligence platform, presented by Andras Iklody at Hack.lu 2023.
Analyzing and Reverse Engineering Antivirus Signatures
Explore antivirus signature analysis and reverse engineering, gaining insights into detection evasion techniques and evaluating Microsoft Defender's effectiveness for improved cybersecurity strategies.
Lazarus Group's Undercover Operations in South Korea 2022-2023
Detailed analysis of Lazarus Group's recent cyber campaigns in South Korea, covering infiltration methods, lateral movement techniques, and data exfiltration strategies used by this sophisticated threat actor.
Unveiling the Trails of Infostealer Malware Ecosystems
Unveiling infostealer malware ecosystems: types, operations, and YouTube spread. Explores Traffer Groups, defense strategies, and a case study on execution and impact of significant attacks.
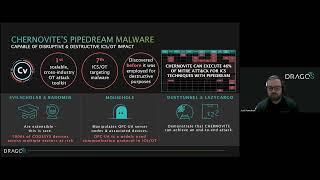
2022 ICS/OT Year in Review Threat Landscape
Comprehensive analysis of industrial cybersecurity threats in 2022, covering new threat groups, ICS-targeting malware evolution, reconnaissance activities, and ransomware impact on ICS/OT environments.

Hands-On Ransomware: Exploring Cybercrime
Explore hands-on ransomware analysis with demos of RAASNet, Yashma, and Lockbit. Learn configuration, building, and detonation techniques from a malware analyst's perspective.
IDA Pro, Malware Analysis, and Python Libraries for Cybersecurity - Episode 4
Explore IDA Pro, assembly language for malware analysis, and Python libraries for penetration testing in this informative cybersecurity discussion with experts from HackerSploit.
Malware Analysis Bootcamp - Analyzing the PE Header
Comprehensive guide to analyzing PE headers using pestudio, covering File Header, Optional Header, Libraries, Imports, and Indicators for malware sample understanding and origin determination.

Flare-On FireEye 2018 CTF - Malware Analysis of Flare Minesweeper
Expert malware researcher Amr Thabet discusses the Flare-On FireEye 2018 CTF challenge, providing insights into malware analysis techniques and sharing experiences from high-profile cybersecurity investigations.