Elevating Cloud Forensics - Hypervisor-Level Methods for Evidence Unveiling
Explore innovative hypervisor-level methods for cloud forensics using AI and machine learning to detect and preserve potential evidence in cloud platforms.
Machine Learning for Enhanced Malware Detection and Classification
Leverage AI and machine learning to enhance malware detection and classification, analyzing large datasets and creating a new ensemble classification facility for improved cybersecurity.

Reverse Engineering Python Binaries - There and Back Again
Uncover Python bytecode secrets: Learn to interpret and decompile .pyc files, explore challenges in automated decompilation, and gain insights into recovering source code from bytecode.
Industroyer2 - Sandworm's Cyberwarfare Targets Ukraine's Power Grid Again
Detailed analysis of Industroyer2 malware targeting Ukraine's power grid, comparing it to the original Industroyer and exploring its communication with ICS hardware using industrial protocols.
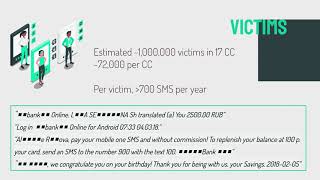
Money Doesn't Stink - Cybercriminal Business Insight of a New Android Botnet
Explore the inner workings of a cybercriminal group operating an Android botnet, including their hierarchy, challenges, and impact on victims' security.
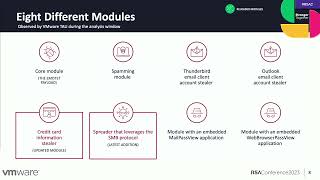
Emotet Exposed - Insider the Cybercriminal's Supply Chain
Uncover Emotet botnet's inner workings, including malware delivery, execution chains, and development lifecycle. Gain insights from VMware researchers who bypassed anti-analysis techniques to map its dynamic infrastructure.
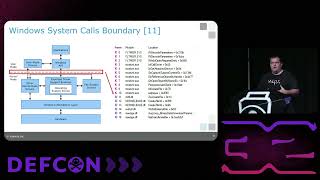
Defeating EDR Evading Malware with Memory Forensics
Discover advanced memory forensics techniques to detect and analyze EDR-evading malware, including system call manipulation, module overwriting, and debug register abuse.
Malware Management Framework - We Detected WinNTI With It
Explore a comprehensive Malware Management Framework and its successful application in detecting WinNTI. Learn effective strategies for identifying and mitigating malware threats in cybersecurity.
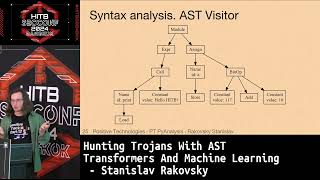
Hunting Trojans with AST Transformers and Machine Learning
Discover advanced techniques for detecting malicious Python projects using AST Transformers and machine learning, focusing on obfuscation methods and countermeasures in cybersecurity.
Tracking and Defining Winnti - A History of Chinese Cyber Espionage
Delve into the complex history and evolution of China's Winnti cyber espionage group, exploring attribution challenges, incident patterns, and effective tracking methodologies for threat intelligence.

Busting Red Team Trends with Style - Building a Custom ETW-Based Sysmon Replacement
Dive into advanced threat hunting with a custom ETW-based Sysmon replacement, exploring enhanced telemetry capabilities for detecting sophisticated red team techniques and threat actor fingerprinting.
Detecting and Triaging Modern Windows Rootkits
Discover modern Windows rootkit detection techniques, memory forensics, and event log analysis methods to combat evolving kernel-level malware threats in Windows 10 and beyond.
Analysis of North Korean Nation-State Attacks Using MagicRAT Malware
Dive into North Korean APT group Lazarus's cyber-kill chain tactics, examining their MagicRAT malware and attack strategies against global energy companies through detailed MITRE ATT&CK analysis.
Identifying North Korean State-Sponsored Threat Actors Through Malware Analysis and OSINT
Uncover the journey of identifying a North Korean state-sponsored threat actor through malware analysis, OSINT investigation, and interviews with intelligence agencies and security forces.
Unparalleled RDP Monitoring to Reveal Attackers' Tradecraft
Dive into advanced RDP attack monitoring techniques and threat actor behaviors through a unique D&D-themed analysis of cybersecurity tradecraft and defensive strategies.
Game Changing Advances in Windows Shellcode Analysis Using SHAREM Framework
Discover groundbreaking advances in Windows shellcode analysis through SHAREM framework, offering enhanced emulation, complete code coverage, and superior disassembly capabilities for security professionals.
WINE Pairing with Malware - Using Linux Tools for Malware Analysis
Discover how to leverage WINE and Linux tools for malware analysis, extracting forensic evidence, and testing offensive security techniques without expensive sandboxes.
Defending KA-SAT: Analysis and Response to the 2022 Cyberattack
Delve into the forensic analysis and defense strategies of the 2022 KA-SAT network cyberattack, exploring malware deployment tactics, network-based attacks, and rapid incident response techniques used to protect satellite communications.
Behind Enemy Lines: Engaging and Disrupting Ransomware Web Panels
Dive into advanced strategies for infiltrating and disrupting ransomware operations by targeting their web panels, APIs, and command centers while gathering vital intelligence on threat actors.
Digital Forensics and Technical Analysis of Phishing Email Campaigns
Dive into comprehensive digital forensics techniques for analyzing phishing emails, from examining suspicious attachments to investigating malicious websites and understanding SOC response protocols.
Understanding File Type Identifiers and Scanners
Dive into file type identification techniques and scanning mechanisms, exploring how different systems detect and process various file formats for enhanced digital forensics and security.