
Malware Analysis and Reverse Engineering Course
Learn techniques for analyzing and reverse engineering malware to understand its behavior and protect systems from threats.
Ekoparty Summer Workshops 2021 - Threat Intelligence, the Malware Analysis Way
Aprende a utilizar eficazmente herramientas de análisis de malware para automatizar procedimientos, construir detectores propios y agilizar futuros análisis, partiendo de una muestra desconocida.
Staatstrojaner for Past Crimes: Legal and Technical Challenges
Analyse der aktuellen Probleme und rechtlichen Herausforderungen von Staatstrojanern in Deutschland, mit Fokus auf Prüfbarkeit, Datenschutz und verfassungsrechtliche Bedenken.
Pyrrha - Navigating System Binaries Easily
Discover Pyrrha, a tool for effortlessly exploring system binaries, enhancing your understanding of executable files and improving reverse engineering capabilities.
Estrategias de Detección de Cyber-Amenazas
Explora estrategias avanzadas para detectar ciberamenazas modernas, analizando objetivos, métodos y herramientas de adversarios en ataques como Loaders, Trojans, Info Stealers y Ransomware.
The Cyber War That (Won't) Happen
Esplorazione dell'evoluzione del rapporto tra informatica e guerra, analizzando le strategie di aggressione digitale e le implicazioni per la sicurezza globale nell'era delle reti interconnesse.
Introducción al Reversing - Ingeniería Inversa para Seguridad Informática
Introducción a la Ingeniería Inversa: fundamentos, aplicaciones en seguridad informática y herramientas esenciales. Ideal para principiantes interesados en exploits, análisis de malware y más.
Memory Forensics with Volatility - HackerSploit Blue Team Series
Explore memory forensics with Volatility in this hands-on tutorial. Learn to analyze system crashes, identify hidden processes, extract crucial information, and enhance your incident response skills.
Spotless Sandboxes: Evading Malware Analysis Systems Using Wear-and-Tear Artifacts
Explore techniques for evading malware analysis systems by exploiting wear-and-tear artifacts on real devices, with insights on detection accuracy and potential defensive strategies.
Backward-Bounded DSE - Targeting Infeasibility Questions on Obfuscated Codes
Explores backward-bounded DSE for solving infeasibility questions in software deobfuscation, demonstrating its effectiveness for opaque predicates and call stack tampering in malware analysis and reverse engineering.
PMP - Cost-Effective Forced Execution with Probabilistic Memory Pre-planning
Explores a cost-effective forced execution technique for malware analysis, using probabilistic memory pre-planning to expose hidden behaviors and overcome self-protection mechanisms.
Understanding Linux Malware
Explore Linux malware analysis challenges, infrastructure design, and insights from a large-scale study of 10,548 samples, addressing the growing threat in embedded devices and IoT.
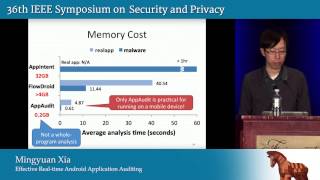
Effective Real-Time Android Application Auditing
Innovative approach combining static and dynamic analysis for efficient, real-time Android app auditing to detect data leaks, offering improved speed and accuracy over existing methods.
A Generic Approach to Automatic Deobfuscation of Executable Code
Explore a generic approach to automatically deobfuscate executable code, applicable to various obfuscation techniques. Learn about semantics-preserving transformations and their effectiveness in extracting internal logic from obfuscated malware.
Malware Analysis With Ghidra - Stuxnet Analysis
Explore Ghidra's features for malware analysis through a hands-on examination of Stuxnet, demonstrating reverse engineering techniques and tool capabilities.
What's in My Hacking Tool Box? by Richard Rushing
Explore a seasoned hacker's toolkit and methodology for penetration testing, covering various domains including malware analysis, mobile app exploitation, and API security.
What You Missed During Black Hat and DEFCON - Security Conference Highlights
Explore key highlights from Black Hat and DEFCON, including car hacking, Android security, policy changes, and malware analysis, as presented by Bugcrowd's VP of Operations.
Malware Clustering - Static and Dynamic Behavior Analysis
Explore innovative malware clustering techniques using static and dynamic behavior analysis, machine learning, and similarity search for robust, scalable, and repeatable results.
Detecting Sandbox Evasion Techniques in Malware Analysis
Explore malware sandbox evasion techniques and learn how to detect them using the MITRE ATT&CK Framework. Discover innovative approaches to improve analysis systems and stay ahead of cyber threats.
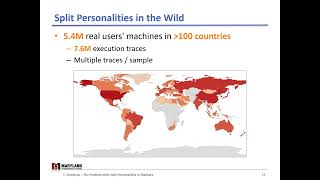
When Malware Changed Its Mind - How Split Personalities Affect Malware Analysis and Detection
Explore the impact of malware behavior variability on analysis and detection techniques, based on a large-scale study of 5.6 million hosts worldwide.
Perfect Storm - Introduction to Ransomware
Explore ransomware types, mechanisms, and trends, including Ransomware-as-a-Service and cryptocurrency wallets, in this comprehensive cybersecurity overview.