And the Beats Go On
Explore new data shippers for Elasticsearch: Packetbeat for network packets, Metricbeat for machine metrics, and Filebeat for log files. Learn to build custom beats with Libbeat.
Velocity, Variety & Volume - Gaining Insights from Your Logs at Scale
Explore log management at scale, covering Kafka, microservices, behavioral detection, and GDPR considerations for effective insights from high-volume data streams.
All Your Logs Are Belong To You!
Discover effective log management techniques and their crucial role in cybersecurity. Learn to harness the power of logs for enhanced threat detection and incident response.
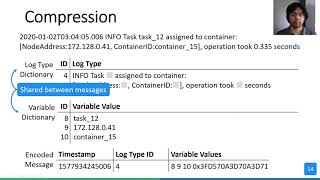
CLP - Efficient and Scalable Search on Compressed Text Logs
Innovative tool for lossless log compression with fast search capabilities, outperforming existing solutions in compression ratio, search speed, and ingestion performance for petabyte-scale log management.
Plotting Hackers - Visualizing Attack Patterns
Explore data visualization techniques for analyzing hacker attack patterns using logs, APIs, and tools like Elastic Search to create informative charts and graphs.
Security Onion Essentials 2024 - Introduction and Overview
Explore Security Onion 2.4.70's features, deployment options, and support in this concise introduction. Learn about training resources and enterprise solutions for enhanced network security monitoring.
Security Onion Essentials 2024 Installation - Part 2
Comprehensive guide to finalizing Security Onion 2.4.70 setup, covering advanced configuration steps and best practices for optimal network security monitoring.

State of the Onion 2023 - Security Onion Platform Overview and Future Directions
Explore Security Onion's evolution from 2008 to present, including platform development, company growth, and future directions in threat hunting and enterprise security monitoring.
What Healthcare Can Learn from the Banking Industry
Exploring how healthcare can enhance security by adopting banking industry practices, covering wireless security, authentication, log management, and risk assessment.
Garbage in Garbage Out - Generating Useful Log Data in Complex Environments
Explore effective log data generation in complex environments, focusing on meaningful data, thresholds, and log management systems for improved security and analysis.
Kubeflow 1.0 Update by a Kubeflow Community Product Manager
Comprehensive overview of Kubeflow 1.0, covering community processes, user survey results, key features, business benefits, and a live demonstration of building and deploying a Kubeflow Pipeline.
A New Approach to Logging as a Stack - Fluent Bit + PostgreSQL
Explore an innovative logging stack using Fluent Bit and PostgreSQL for efficient log collection, processing, and analysis at scale. Learn how JSONB storage enhances performance for trillions of records.
Build Advanced Search Experiences with a Custom Query Language
Explore advanced search techniques using custom query languages for efficient data retrieval in complex structures, enhancing user experience and search precision.
Practical Microservice Security
Explore microservice security through real-world examples, attacks, and defense techniques. Learn practical tools and strategies to secure architectures without compromising benefits.
Monitor Your Containers with the Elastic Stack
Explore container monitoring using the Elastic Stack, focusing on Beats for data collection, log fetching, metrics gathering, and network traffic analysis in containerized environments.
Telemetry Data Understanding and Optimization for Cost-Effective Observability with Mezmo
Discover how to effectively manage and optimize telemetry data pipelines for enhanced observability, cost control, and faster incident response in enterprise systems.
Using and Abusing Python's Logging Module for More Readable Logs
Discover unconventional yet practical techniques for enhancing Python's logging module, drawing from real production experiences to improve log readability and effectiveness.
Using and Abusing Python's Logging Module for More Readable Logs
Dive into advanced techniques and unconventional approaches for enhancing Python log readability, featuring real-world production examples and their long-term impact.
Ask Your Logs - Structured Logging for Rails Applications
Explore structured logging techniques to transform Rails logs into actionable data, enabling efficient debugging and insightful analysis of production issues.
μSlope - High Compression and Fast Search on Semi-Structured Logs
Innovative system for compressing and searching semi-structured log data, offering superior compression ratios and faster search speeds compared to existing solutions for managing large-scale log datasets.
Getting the Most Out of Your Logs at 3 AM - Effective Logging Practices
Learn effective logging practices for troubleshooting, monitoring, and security. Explore structured logging, proper log levels, and storage solutions to optimize your application's observability and performance.